
Quantum-Safe Security Solution
Helping Australian organizations protect long-lived data and connected systems as encryption moves to post-quantum standards.
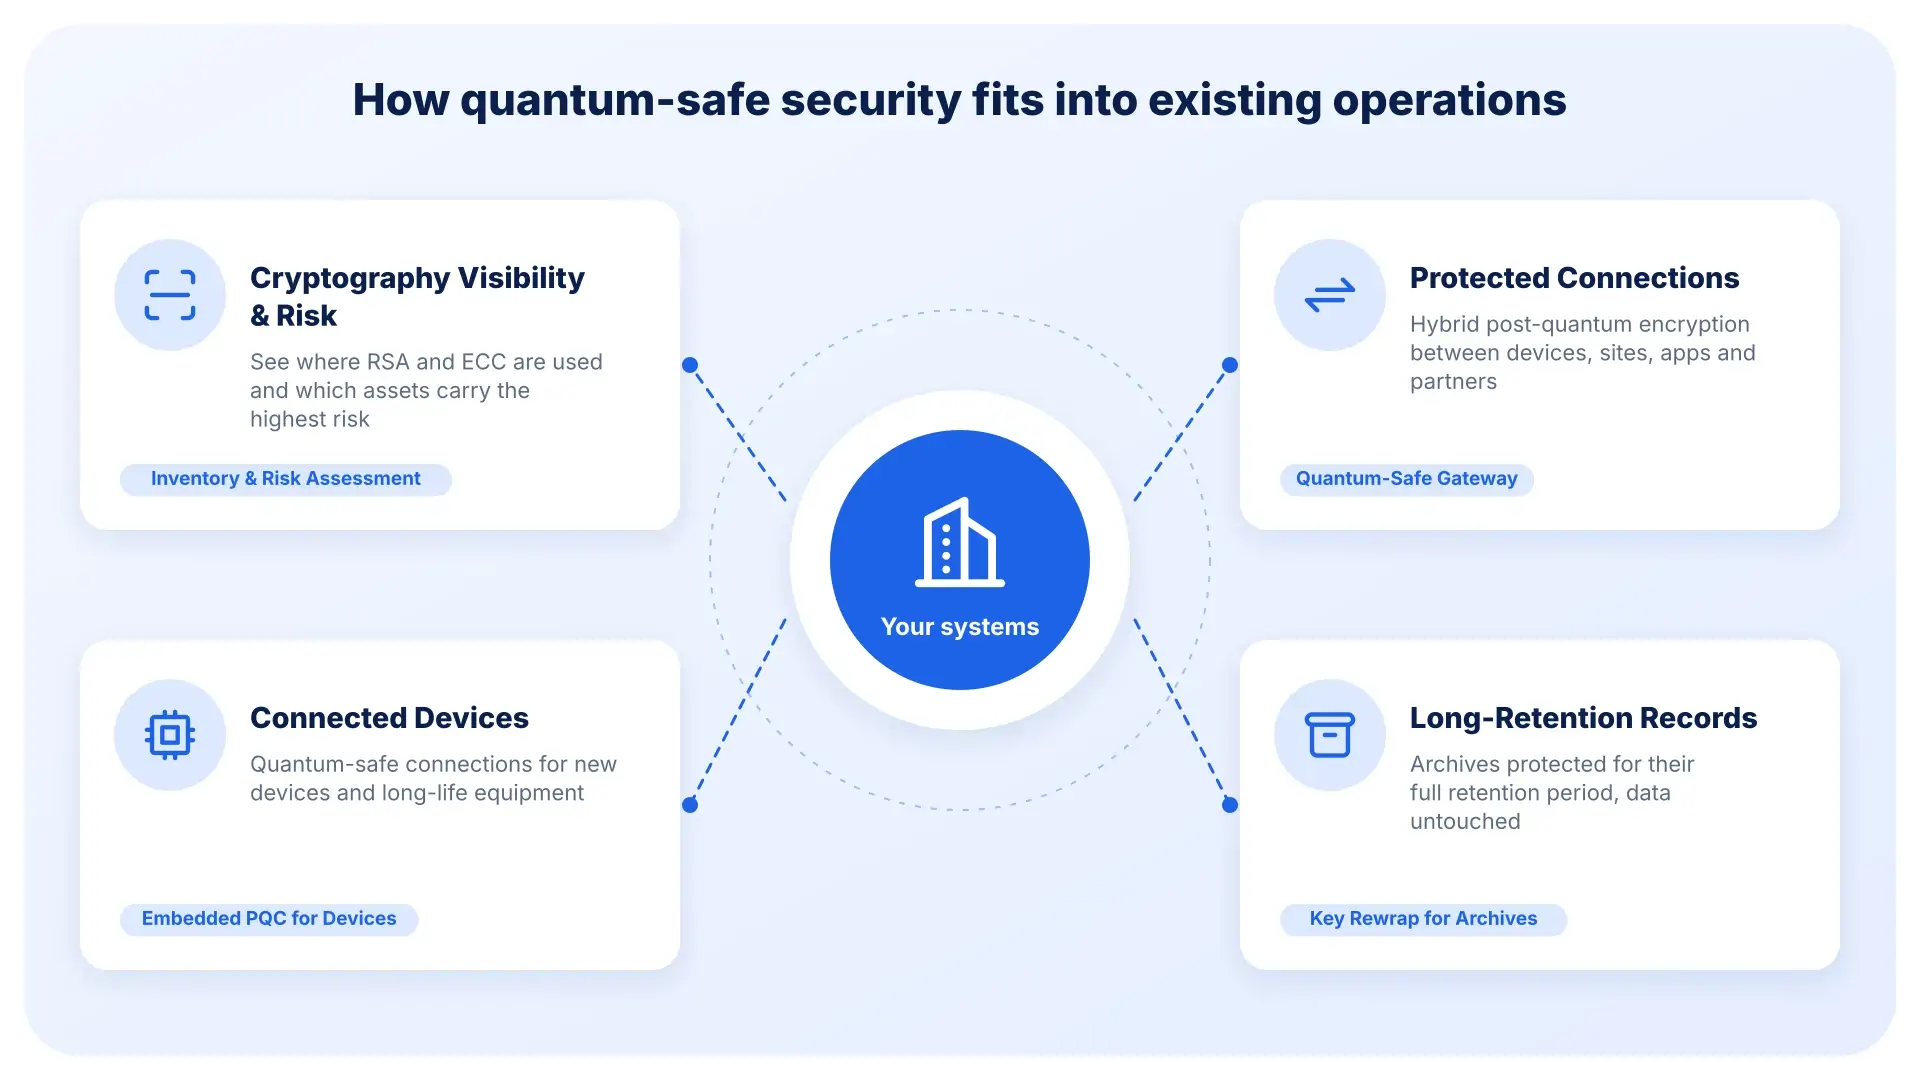
How quantum-safe security fits into existing operations
Data captured today can be stored and decrypted later, once quantum computers can break today’s RSA and ECC encryption. Australian organizations are encouraged to start moving to post-quantum cryptography now, well before quantum computers become a practical threat. KPS works with partners to find where vulnerable cryptography is used, then upgrade systems step by step through system integration and solution customisation, without disrupting day-to-day operations.
Supporting organisations from first visibility of their cryptography through to protected devices, networks and records.
Cryptography Visibility & Risk: See where RSA and ECC are used across code, configurations and certificates, and which assets carry the highest risk.
Protected Connections: Keep traffic between devices, sites, apps and partners protected with hybrid post-quantum encryption.
Connected Devices: Bring quantum-safe connections to new devices and to long-life equipment that is hard to update.
Long-Retention Records: Keep archived records protected for their full retention period without re-encrypting the data.
KPS Quantum-Safe Solutions
Purpose-built components that can be combined and customised for each environment. All are available in the customer’s own environment.
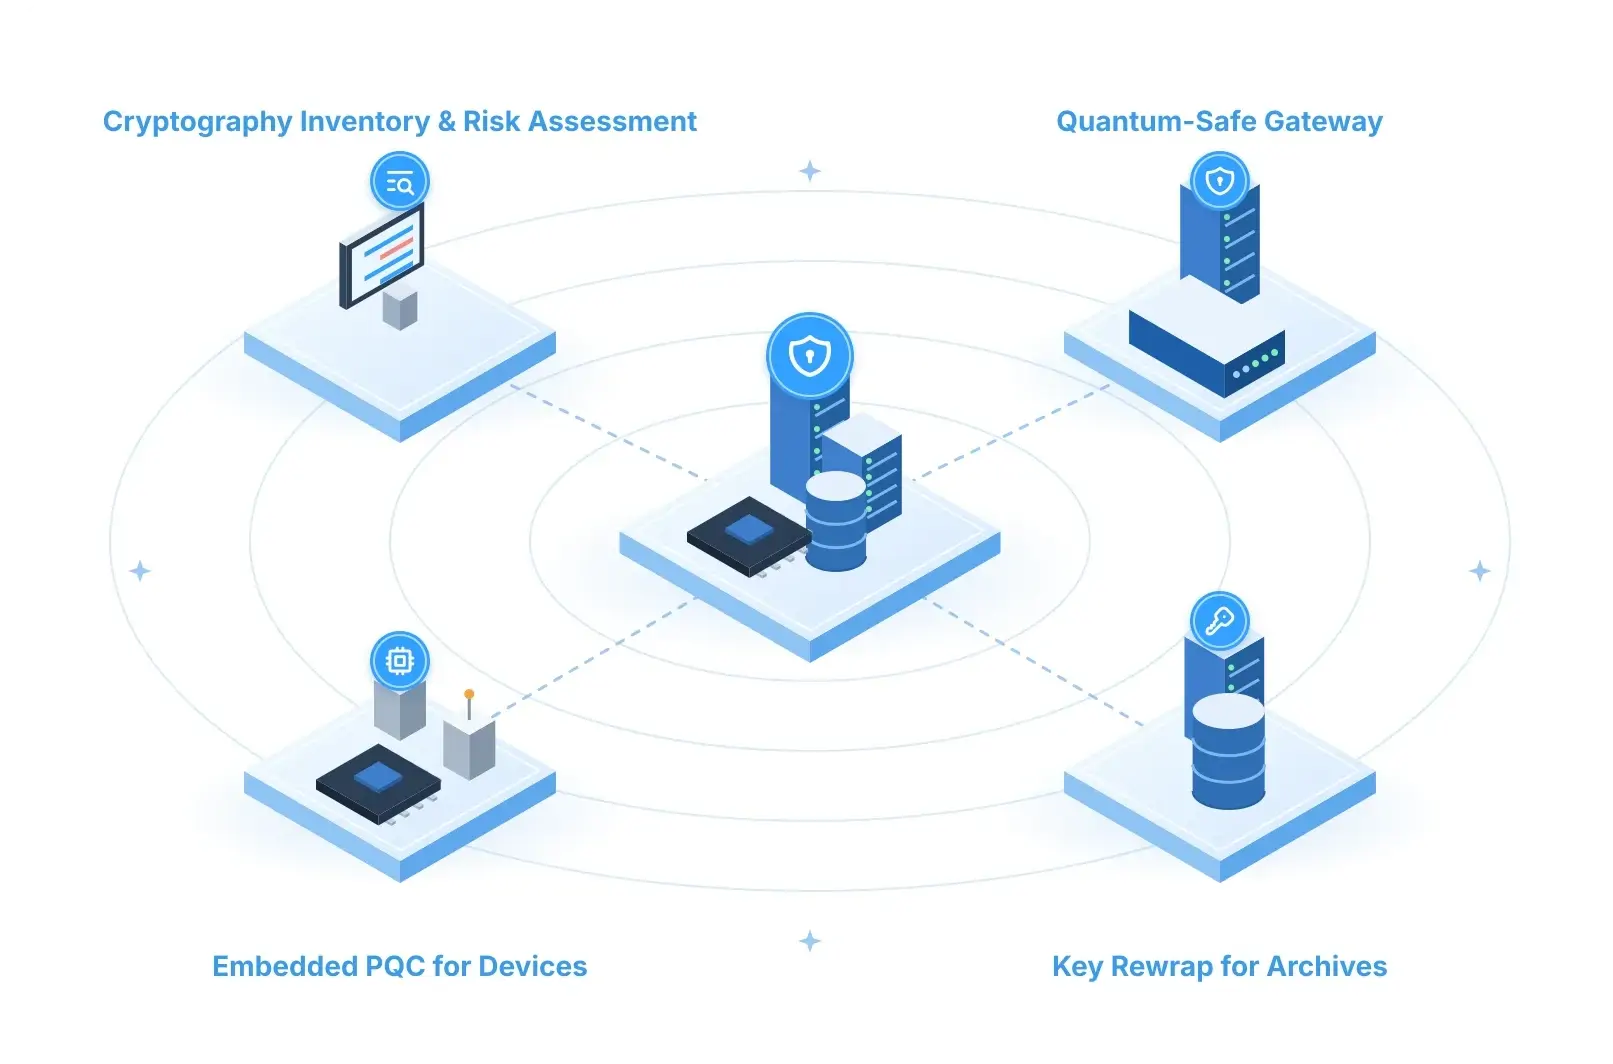
Cryptography Inventory & Risk Assessment
An automated assessment that builds an inventory of cryptography across code, dependencies, configurations and certificates, rates each asset high, medium or low, and recommends the next step.
Quantum-Safe Gateway
A gateway placed in front of existing devices, sites or APIs that upgrades their connections to hybrid post-quantum TLS, with no changes to the devices or back-end systems.
Quantum-Safe API Gateway
A gateway adds post-quantum protection to customer, adviser and partner APIs, without changing the applications behind them.
Practical outcomes of moving early
Helping organisations reduce long-term exposure while keeping existing operations running.
Reduce Exposure to “Harvest Now, Decrypt Later”
Sensitive data in transit and in archives stays protected against future decryption.
Plan with Evidence
A clear inventory and risk ranking turns post-quantum migration into a scheduled programme instead of a guess.
Upgrade Without Disruption
Hybrid encryption keeps current clients, partners and devices working while protection improves.
Prepare for Regulatory Timelines
Support transition plans aligned with Australian and international timelines to phase out RSA and ECC between 2030 and 2035.

Contact Us
For any questions, support requests or partnership opportunities, please reach out to us via:


