
Key Rewrap for Archives
Keep long-retention records protected against future quantum attacks, without re-encrypting or moving the data.
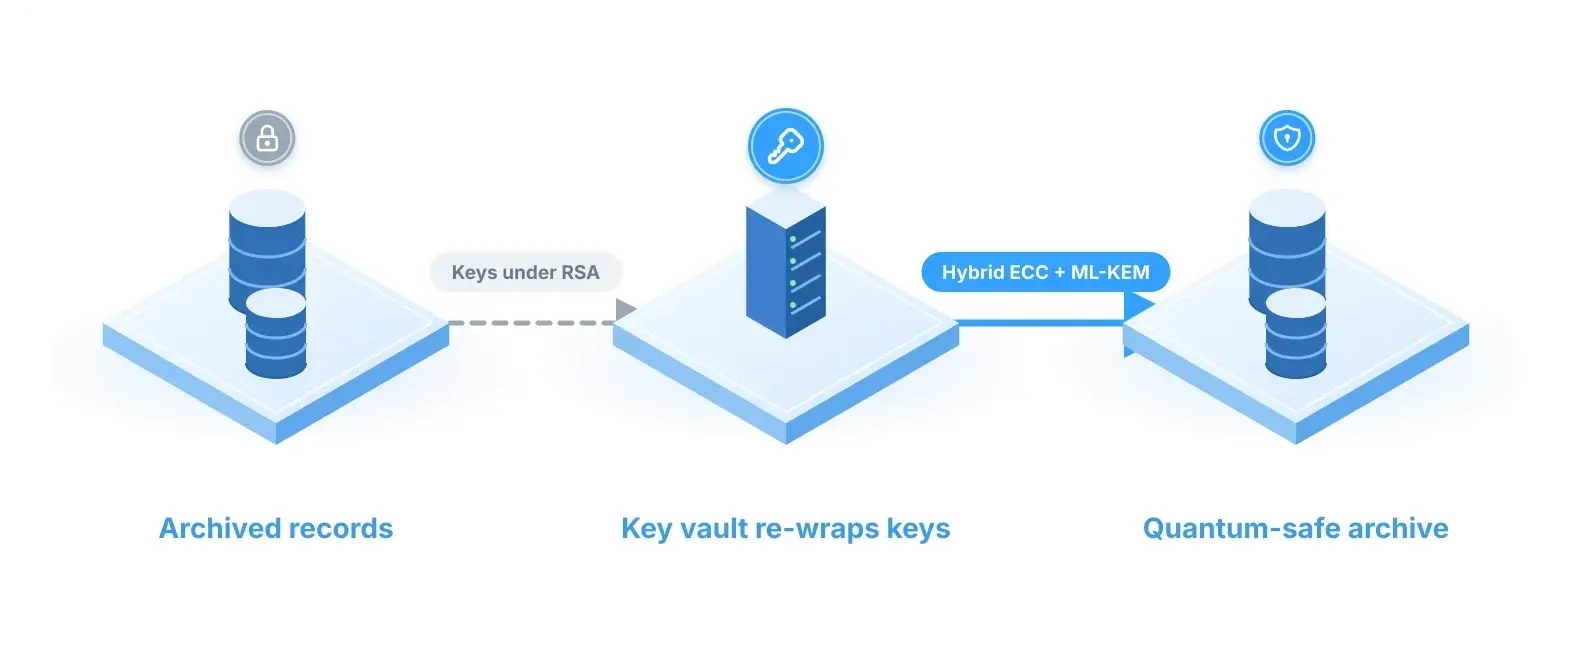
Long-lived records, protected for their full retention period
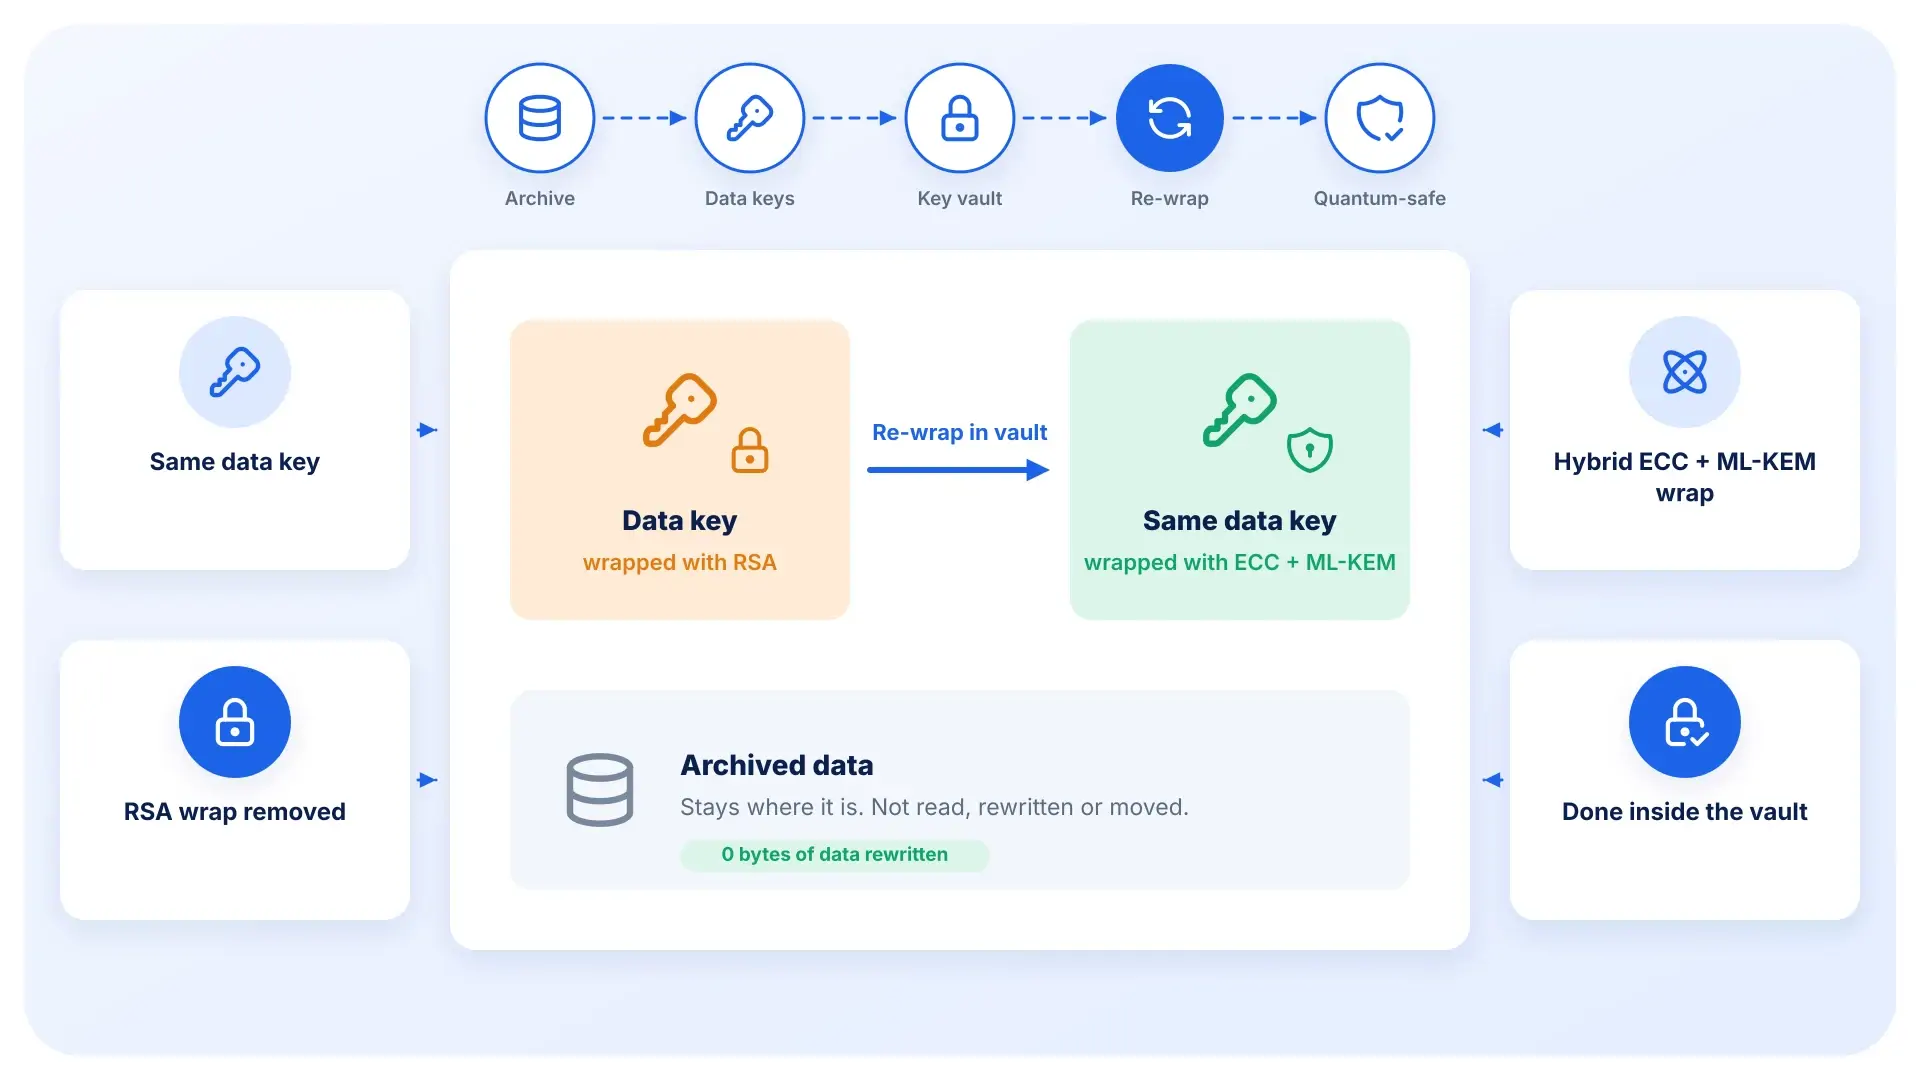
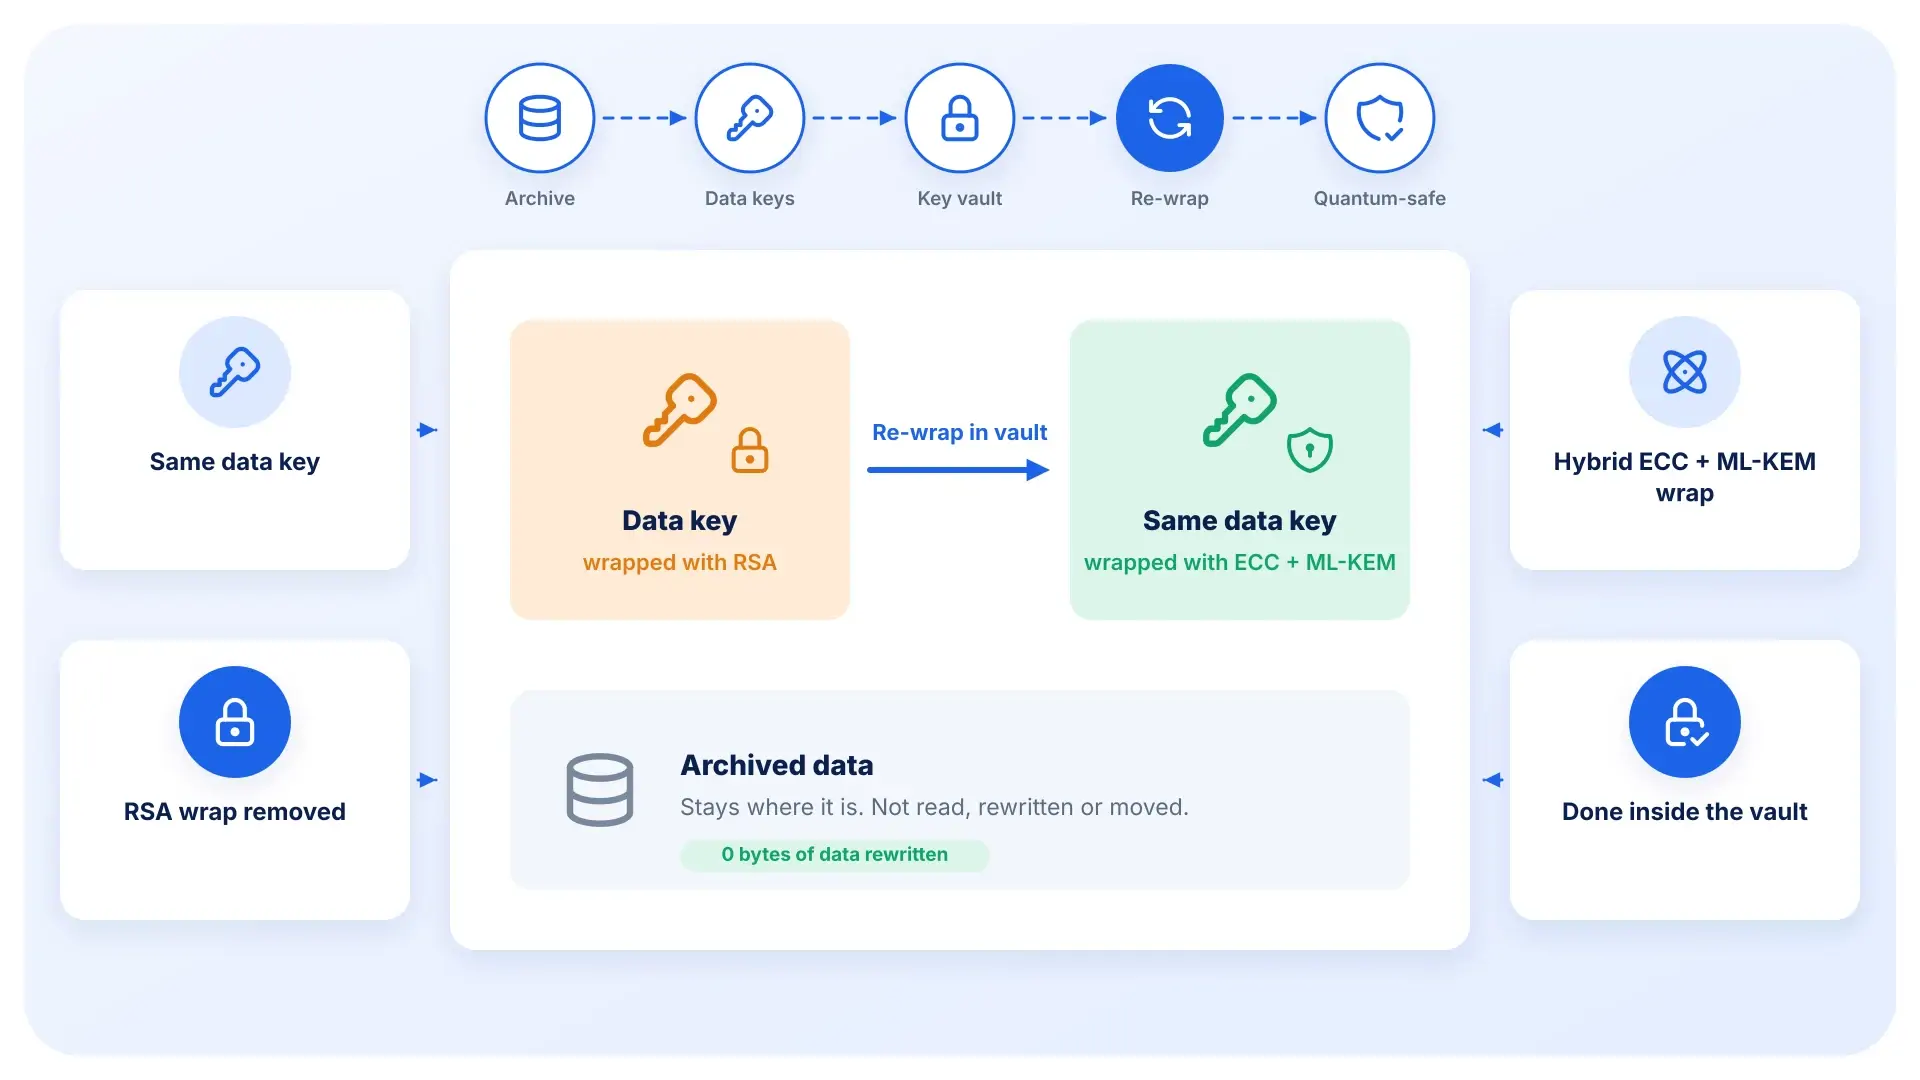
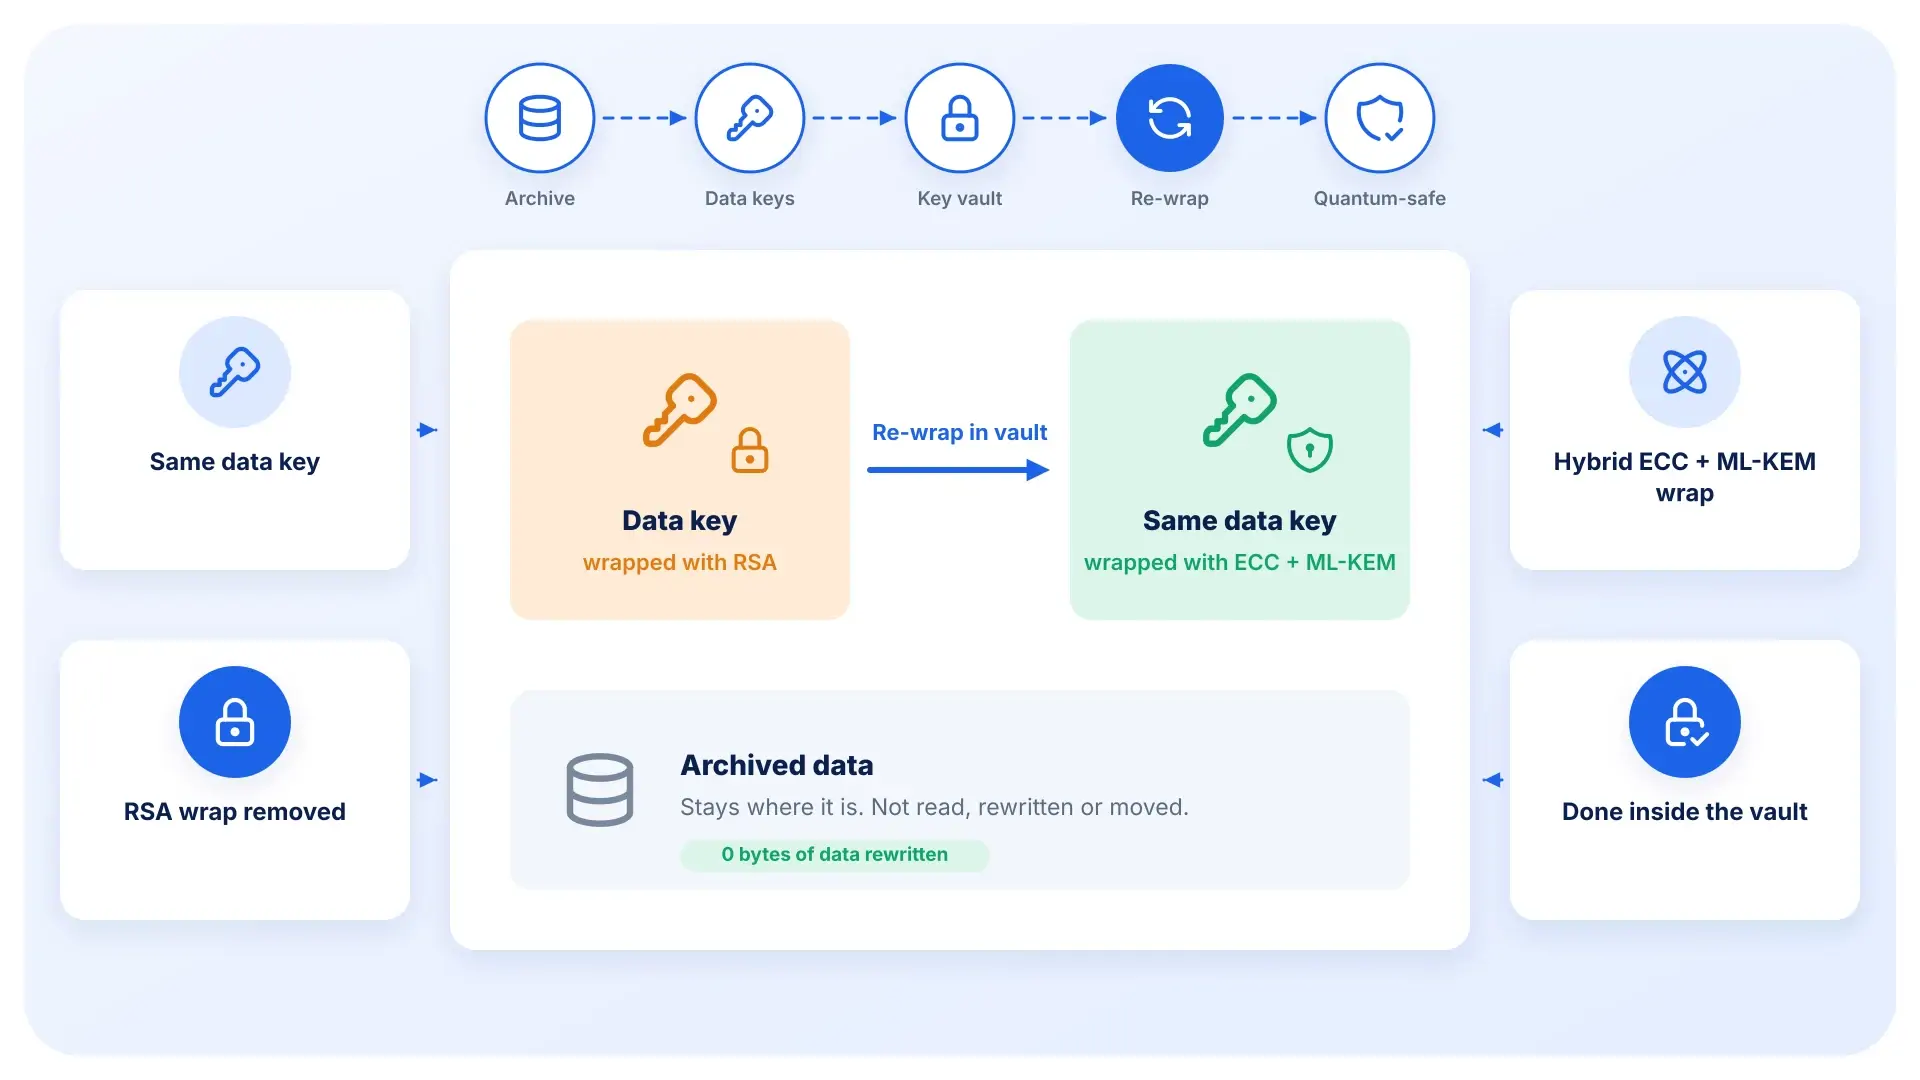
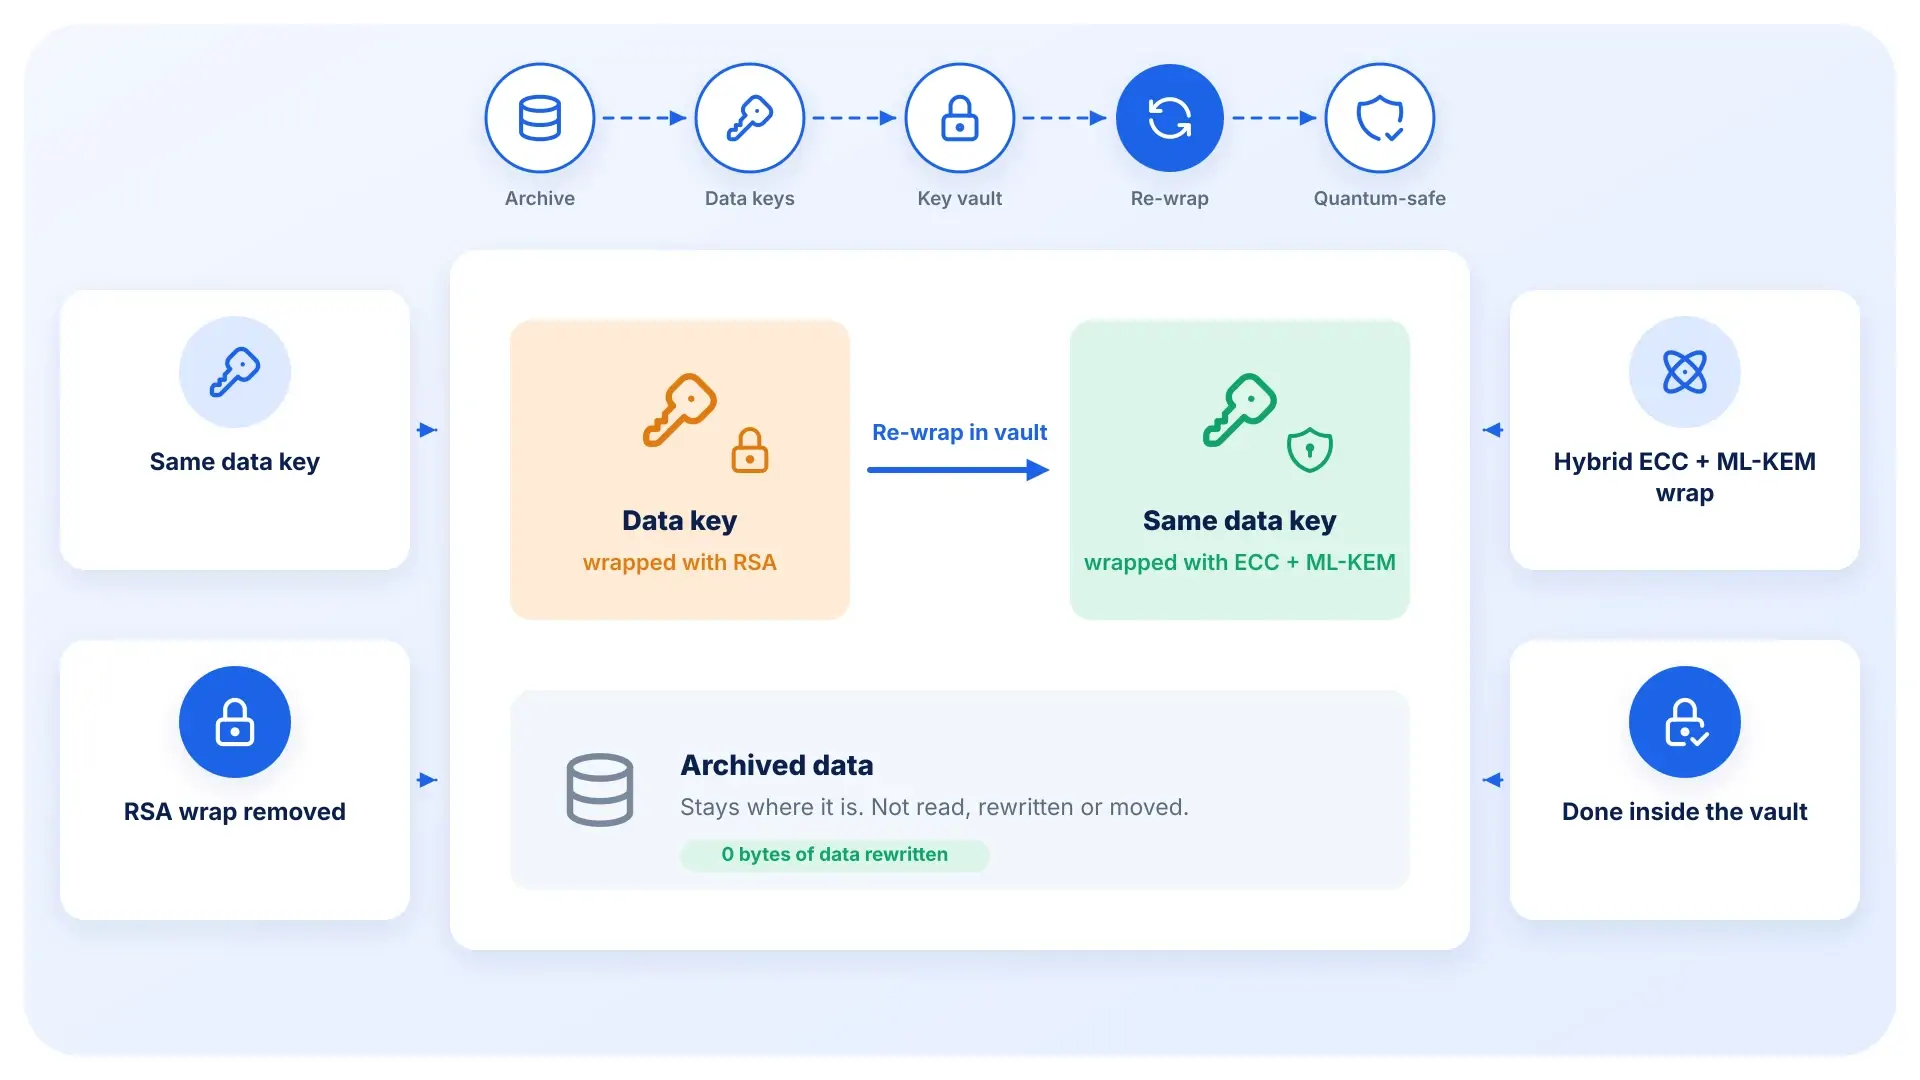
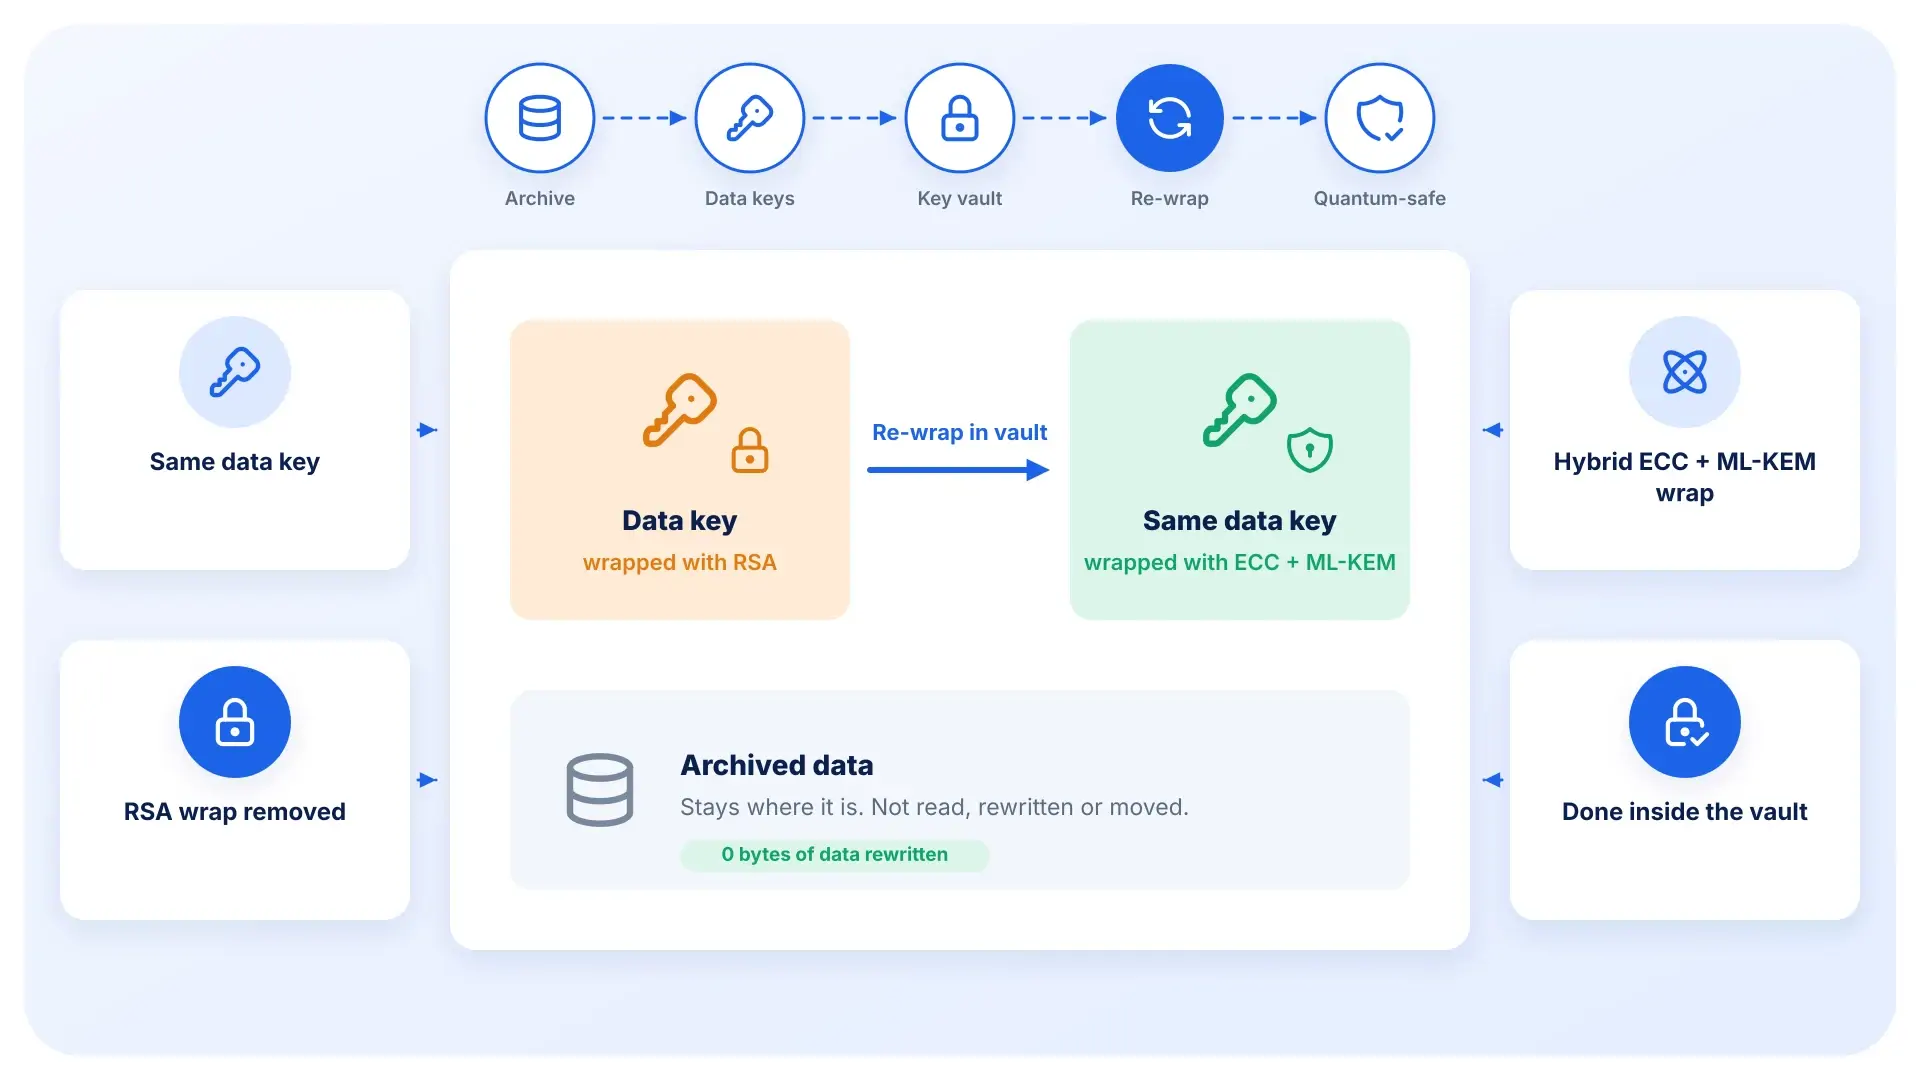
Many organisations must keep records for seven years or longer: financial and superannuation records, health records and long-term backups. These archives are usually encrypted with data keys that are themselves protected by RSA. If those keys are captured today, the archive could be opened once quantum computers can break RSA. Re-encrypting large archives is slow and risky. Key Rewrap for Archives works inside the existing key vault and moves the data keys to hybrid post-quantum protection (ECC + ML-KEM), while the stored data stays exactly as it is.
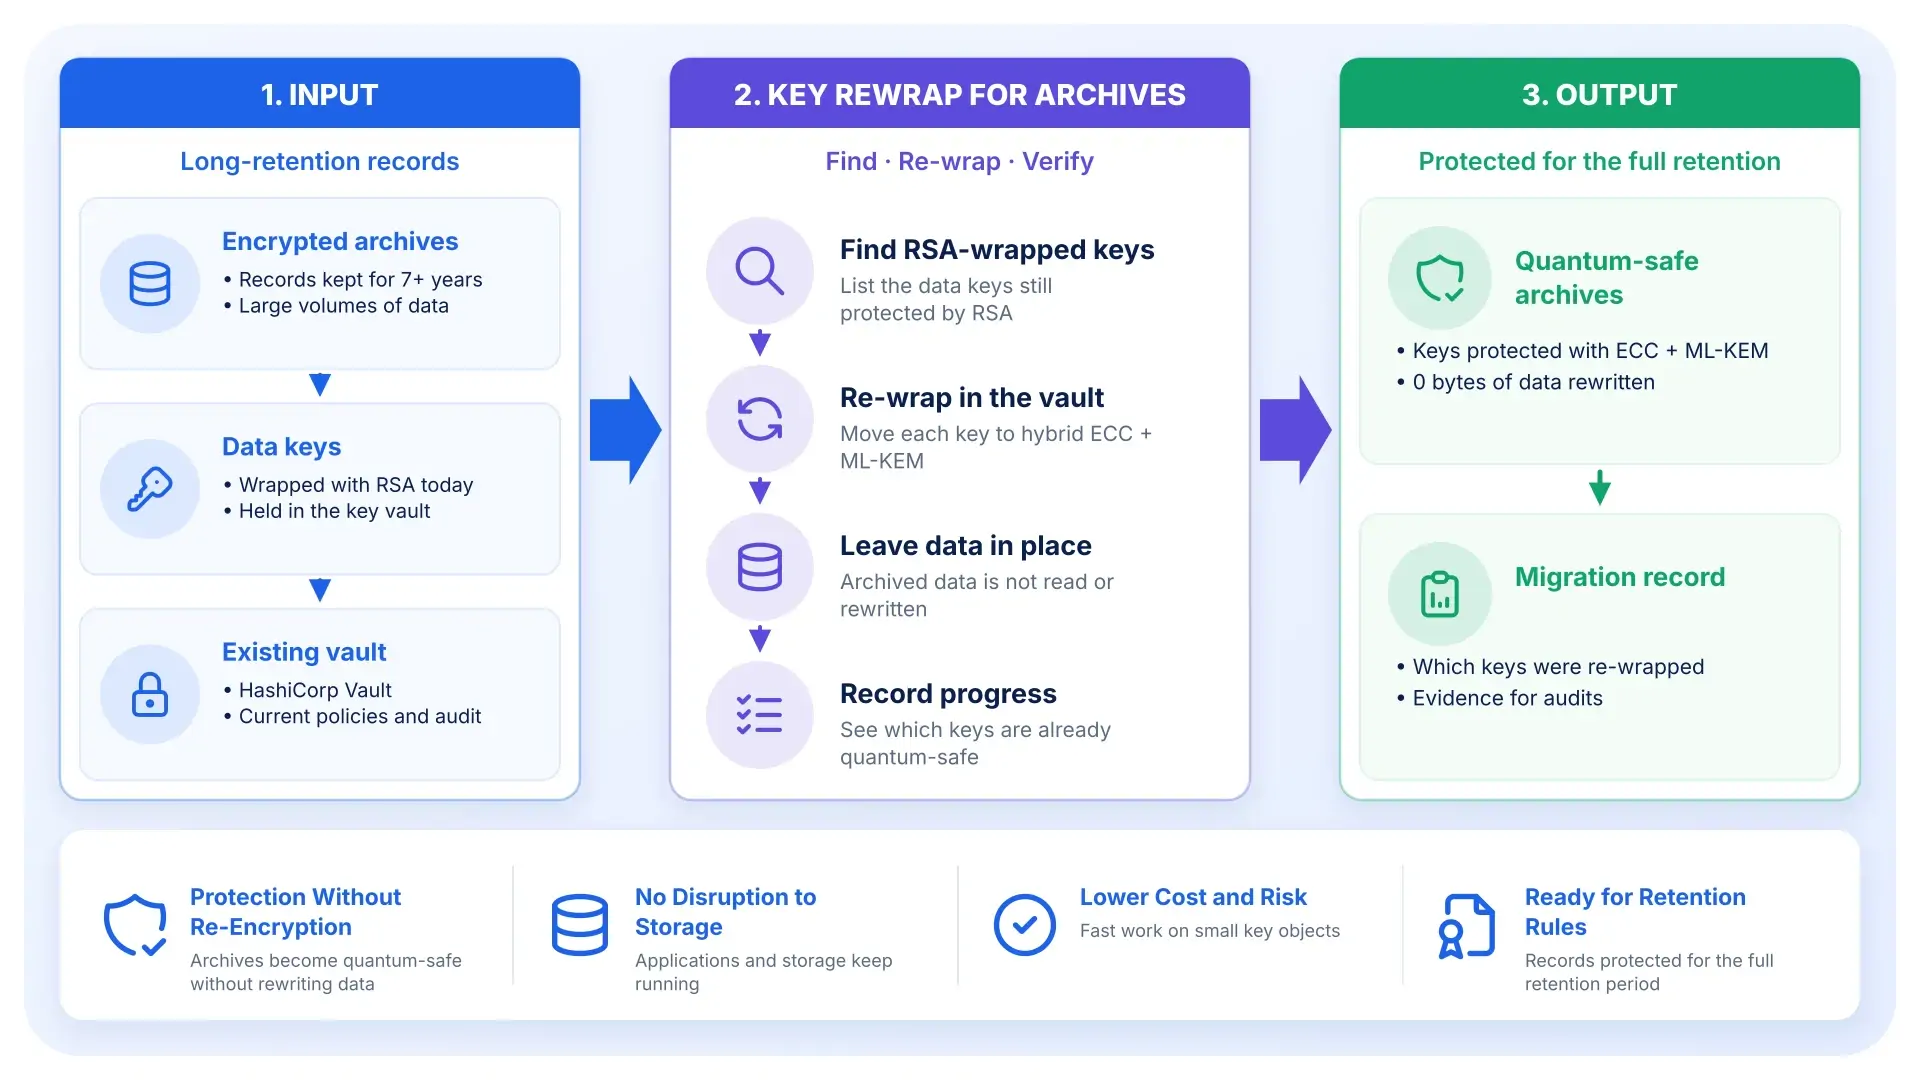
Re-wraps data keys from RSA to hybrid ECC + ML-KEM inside the key vault
0 bytes of stored data rewritten
Built as a plugin for HashiCorp Vault
Re-wraps data keys from RSA to hybrid ECC + ML-KEM inside the key vault
0 bytes of stored data rewritten
Built as a plugin for HashiCorp Vault
Protects archives against “harvest now, decrypt later”
Avoids long re-encryption projects and storage downtime
Keeps records safe for their full legal retention period
Protects archives against “harvest now, decrypt later”
Avoids long re-encryption projects and storage downtime
Keeps records safe for their full legal retention period
Where It Fits
Environments where data must stay confidential long after it was written.
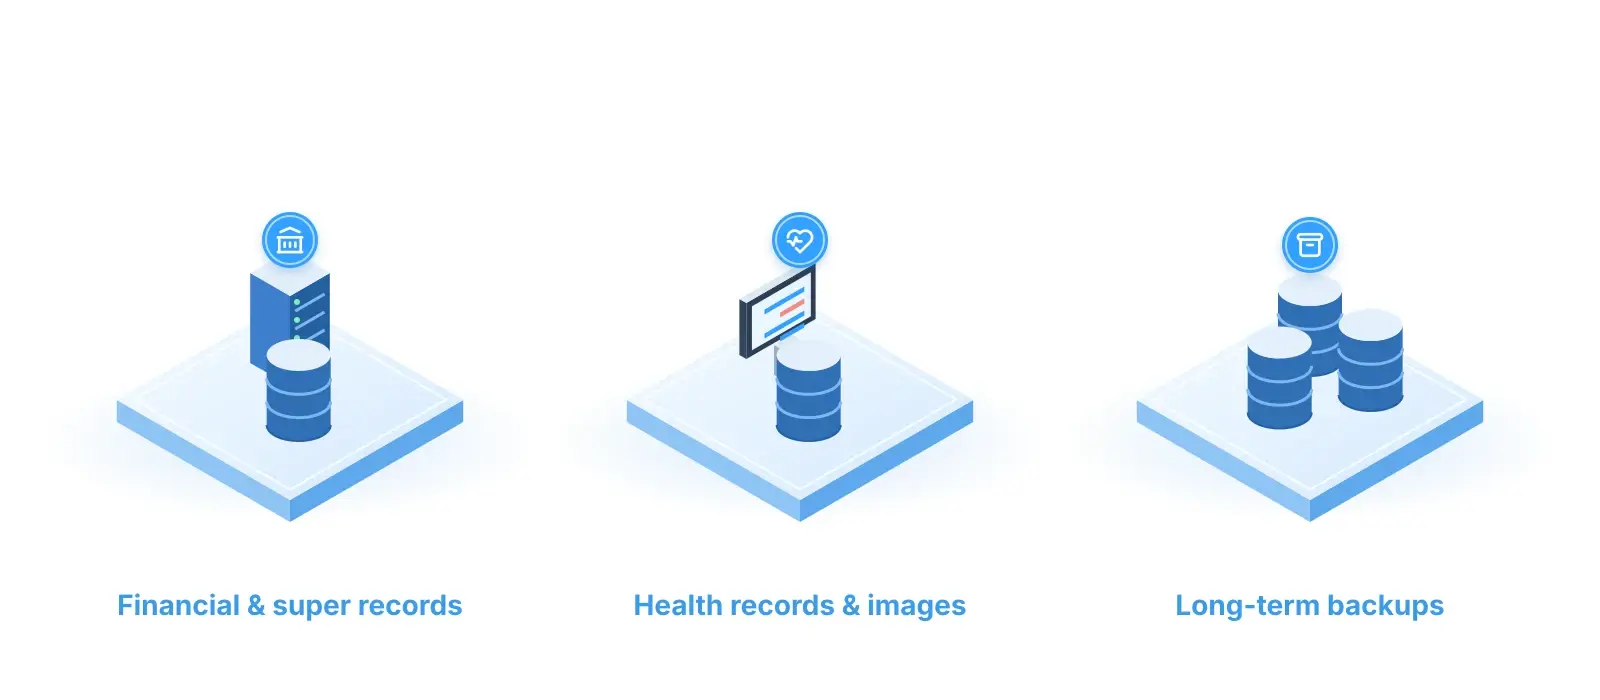
Financial and Superannuation Records
Statements, transactions and member records kept for many years stay protected without touching the archive itself.
Health Records and Images
Patient records and medical images that must remain confidential for decades are protected at the key level.
Long-Term Backups
Encrypted backups and snapshots keep their contents unchanged, while the keys that unlock them become quantum-safe.
Business Impact
Practical outcomes of protecting archives at the key level.
Protection Without Re-Encryption
Large archives become quantum-safe without rewriting the data.
No Disruption to Storage
Applications and storage systems keep running while keys are re-wrapped.
Lower Cost and Risk
Only small key objects change, so the work is fast and easy to verify.
Ready for Retention Rules
Records stay protected for the full period that the law requires them to be kept.
Key Capabilities
What the solution enables for security and storage teams.
Re-Wrap Keys in Place
Moves each data key from RSA protection to hybrid ECC + ML-KEM inside the vault.
Leave Data Untouched
Track Progress
Use the Existing Vault
Deployment & Integration
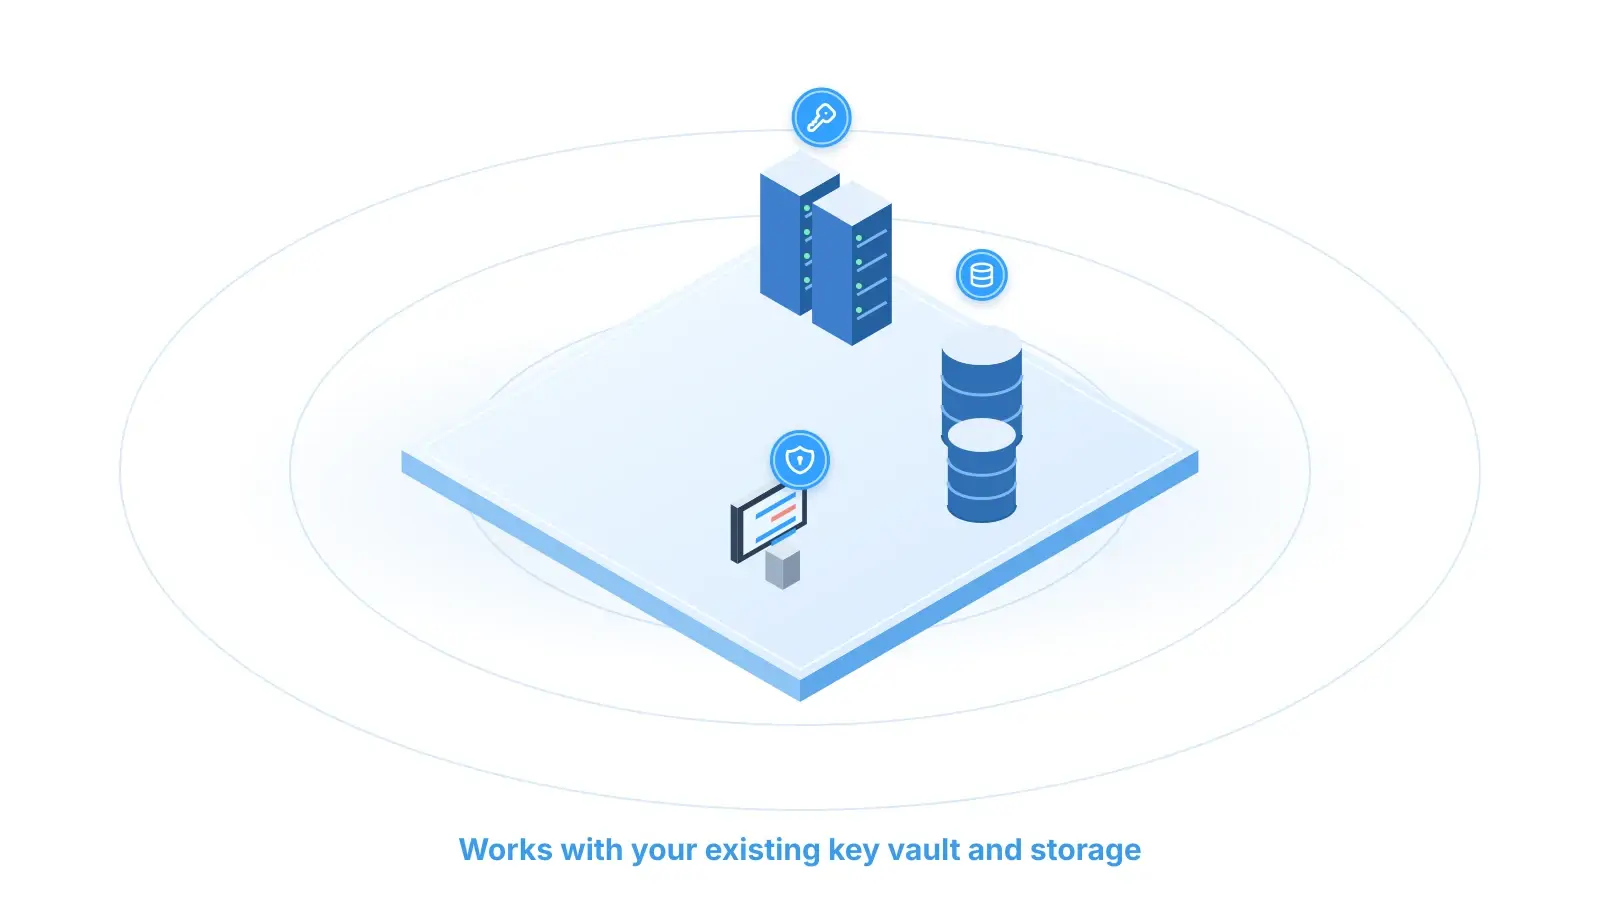
The solution runs inside the key-management setup the organisation already has.
Inside the Key Vault: Installed as a plugin to the existing HashiCorp Vault deployment.
No Change to Storage: Databases, file stores and backup systems are not modified.
On-Premise or Private Cloud: Runs wherever the vault already runs; keys stay in the customer’s environment.
Delivered with Partners: KPS and its partners adapt the rollout to each key-management setup, starting with a proof of concept.
Designed to fit your setup
Reference scenarios
A financial services organisation keeps client records and statements for seven years under RSA-wrapped keys. The vault plugin re-wraps the keys with hybrid ECC + ML-KEM, while the archive stays in place.
Key Outcomes
Archive protected without re-encryption
No downtime for reporting systems
Clear record of which keys were migrated

Contact Us
For any questions, support requests or partnership opportunities, please reach out to us via:


