
Cryptography Inventory & Risk Assessment
Find where quantum-vulnerable cryptography is used across your systems, and know what to fix first.
The first step of every post-quantum migration
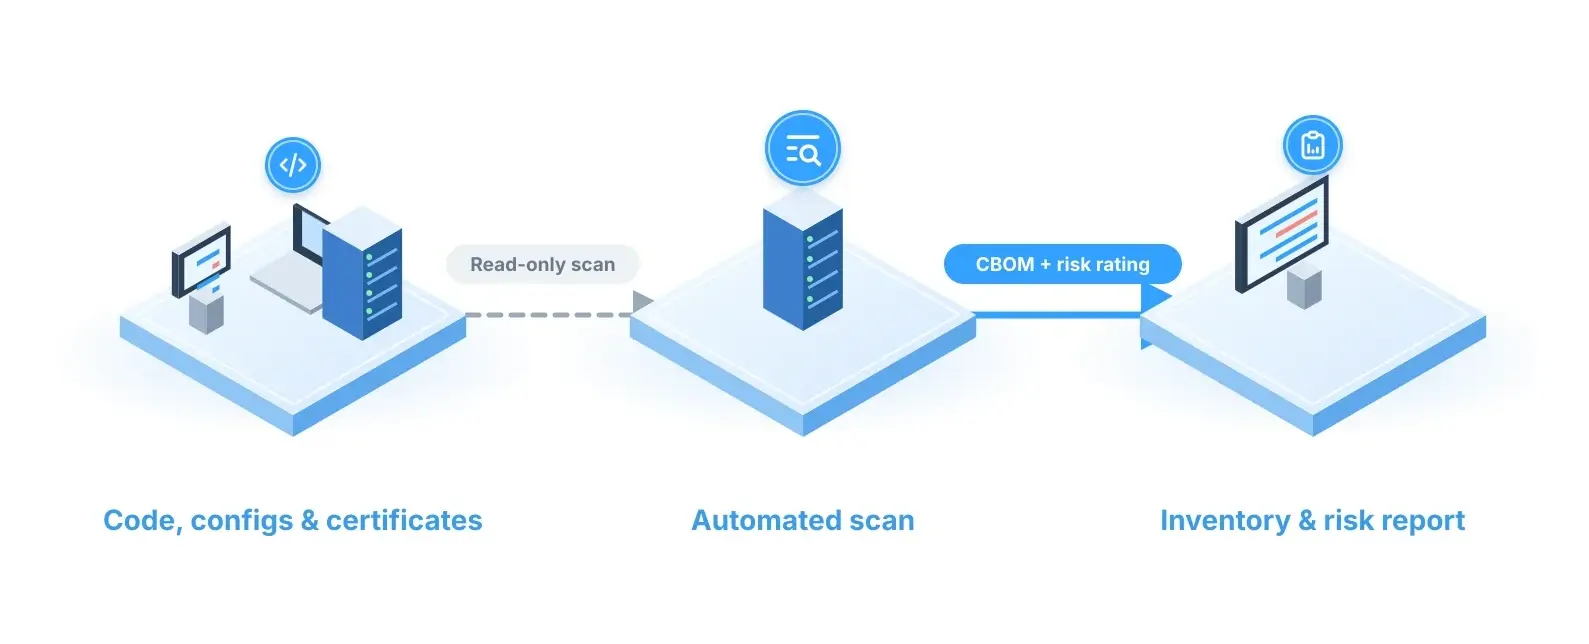
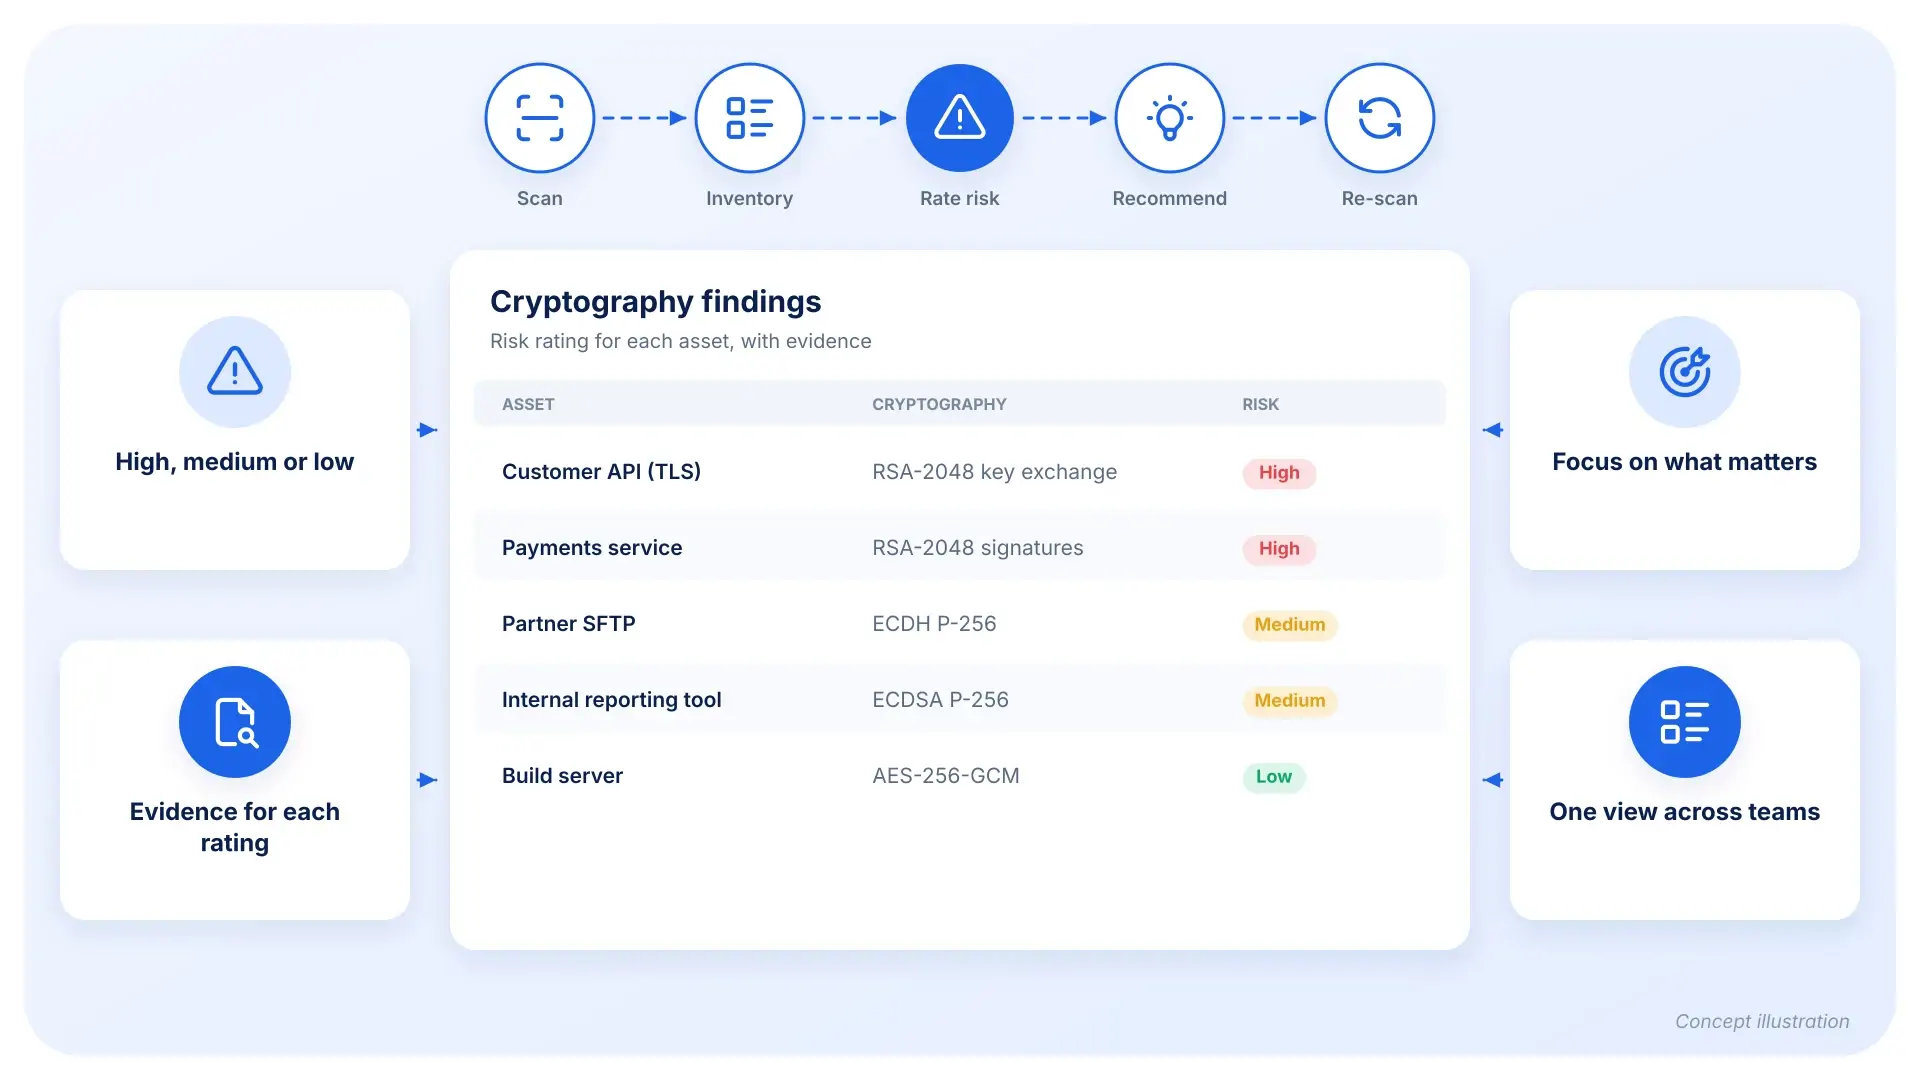
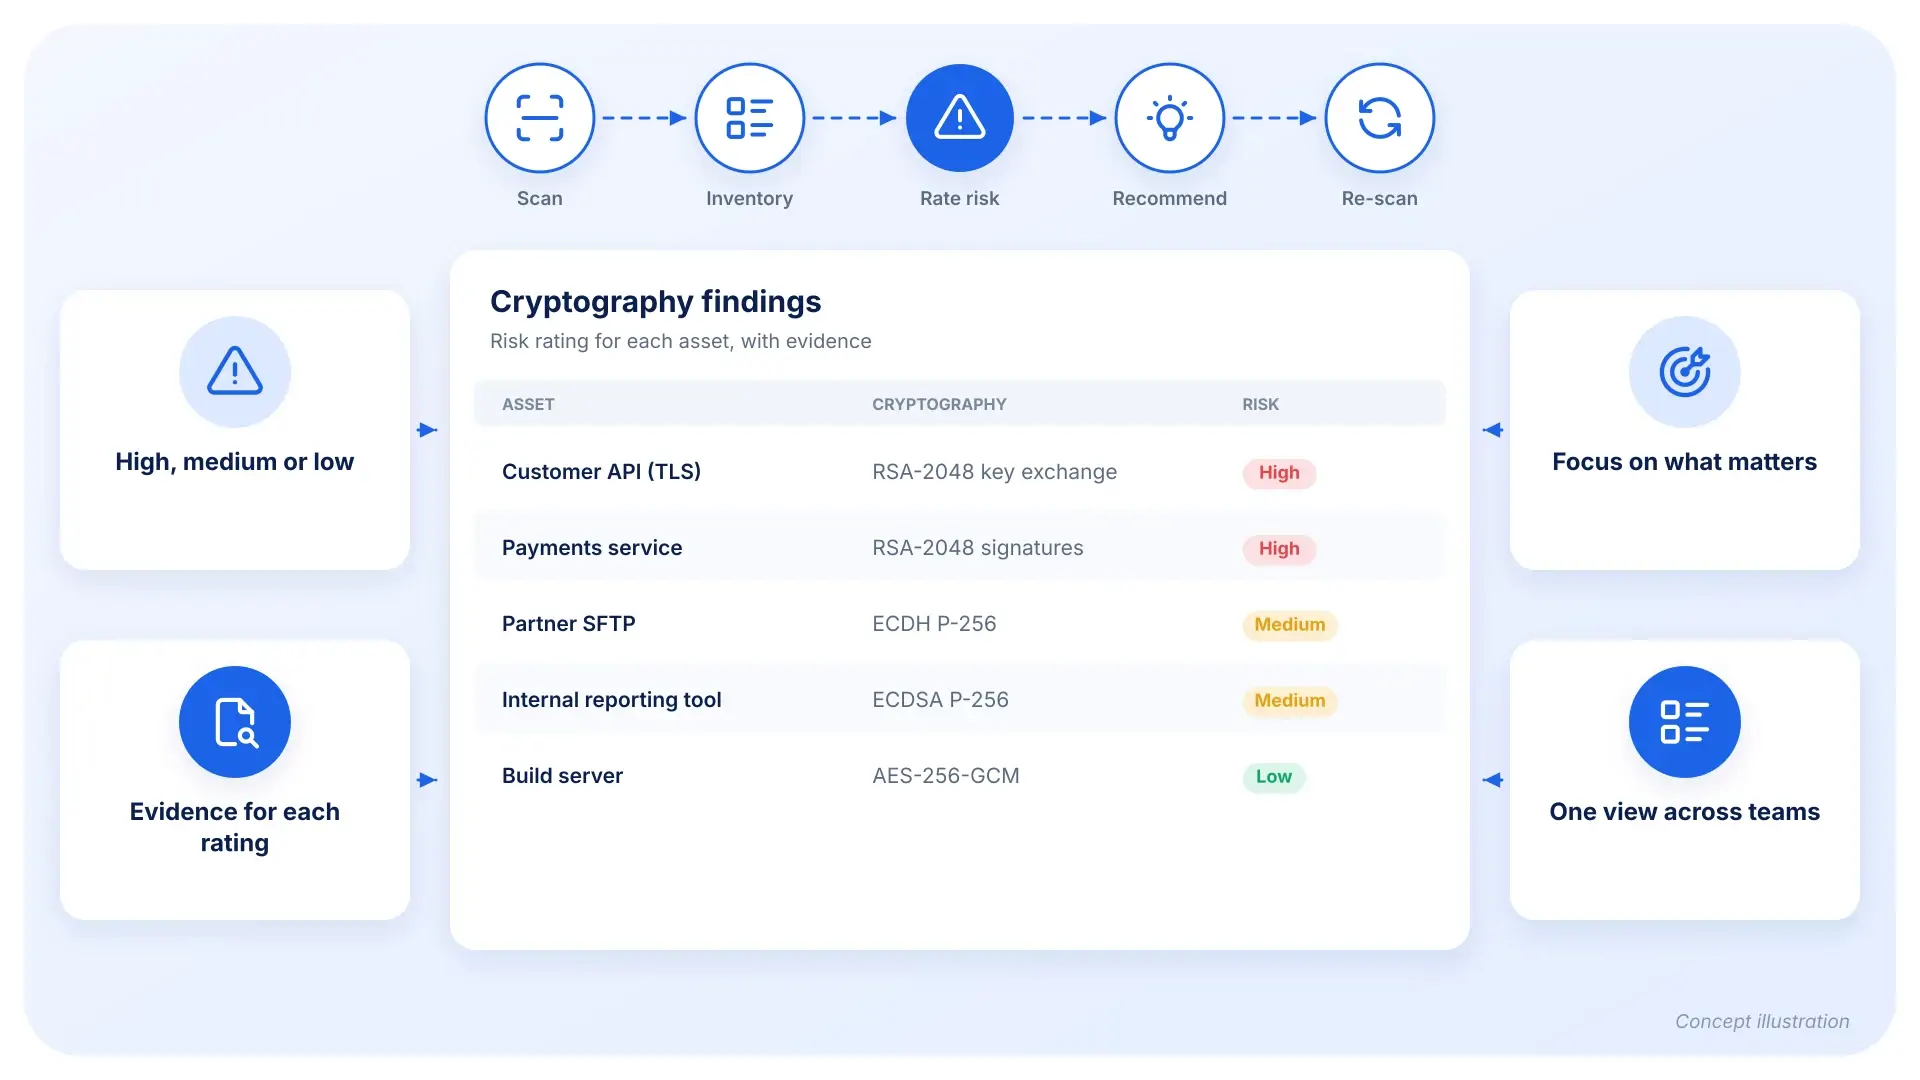
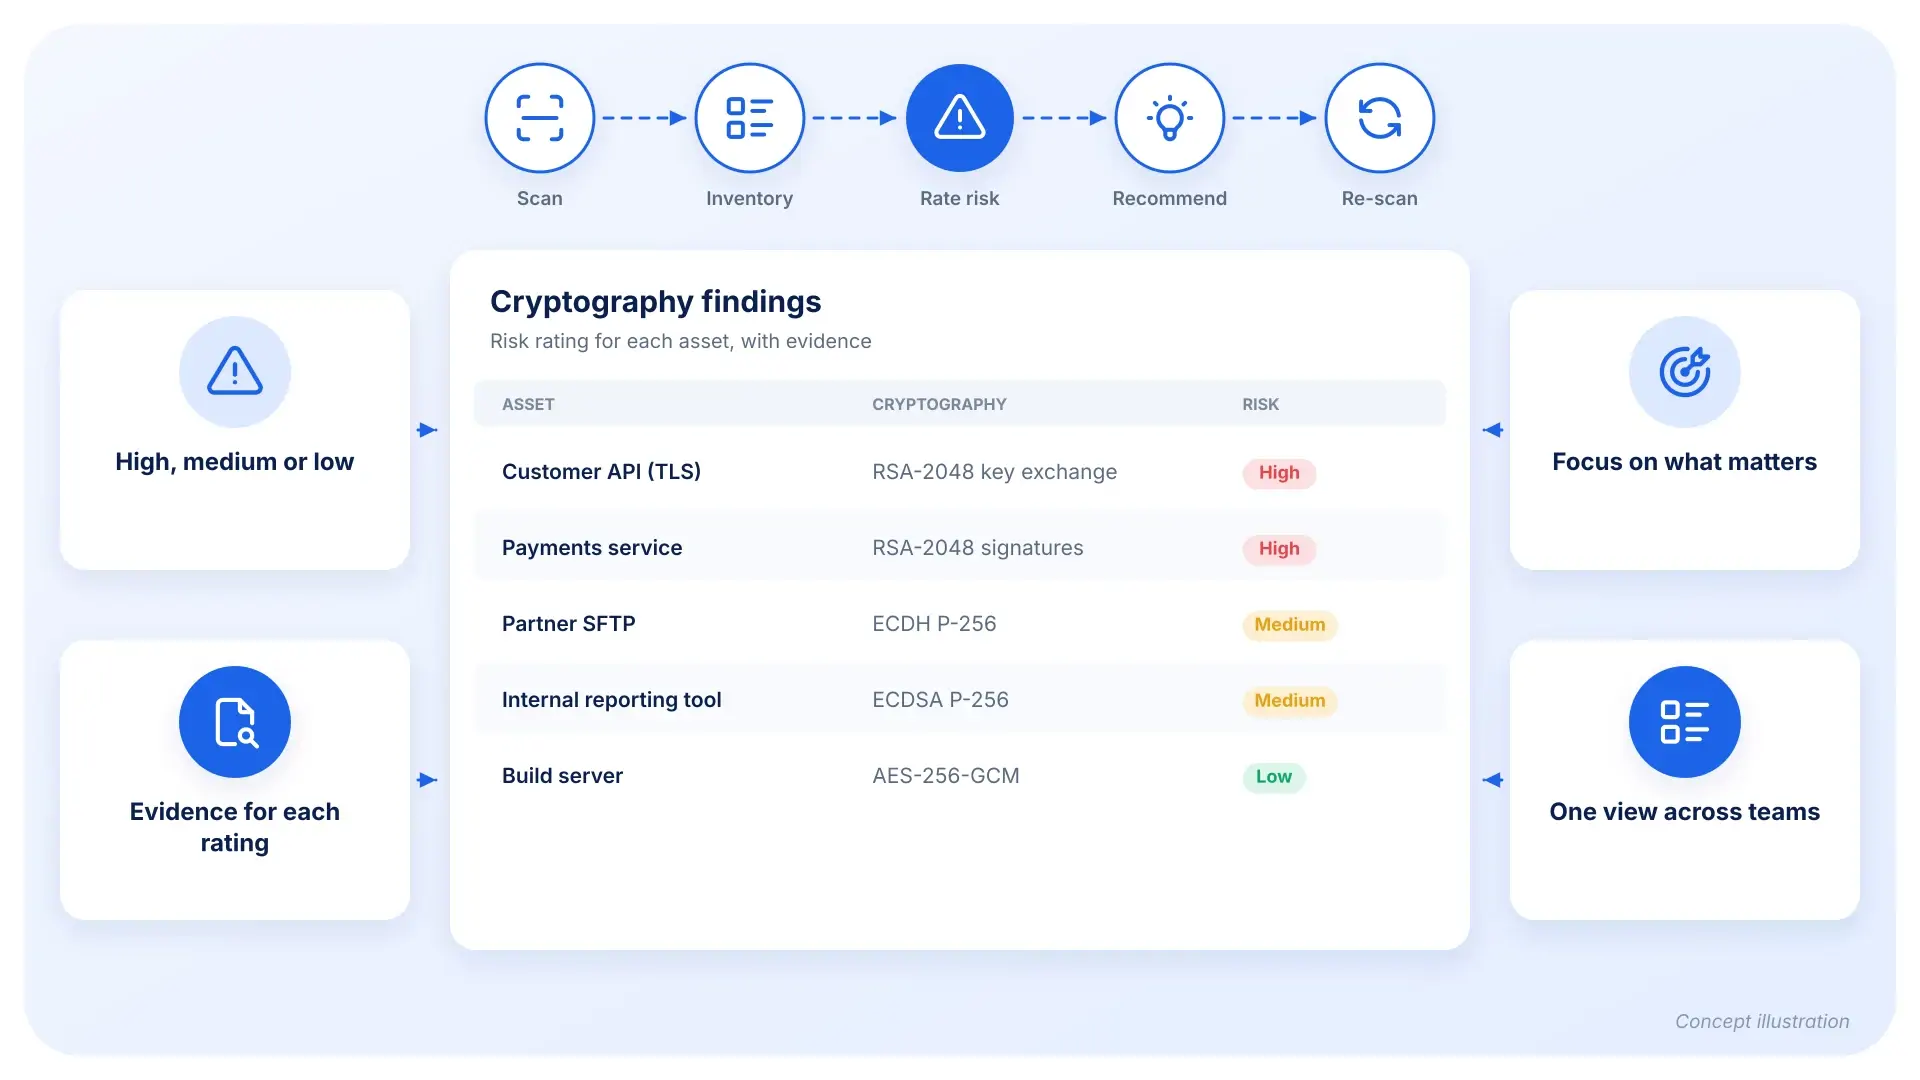
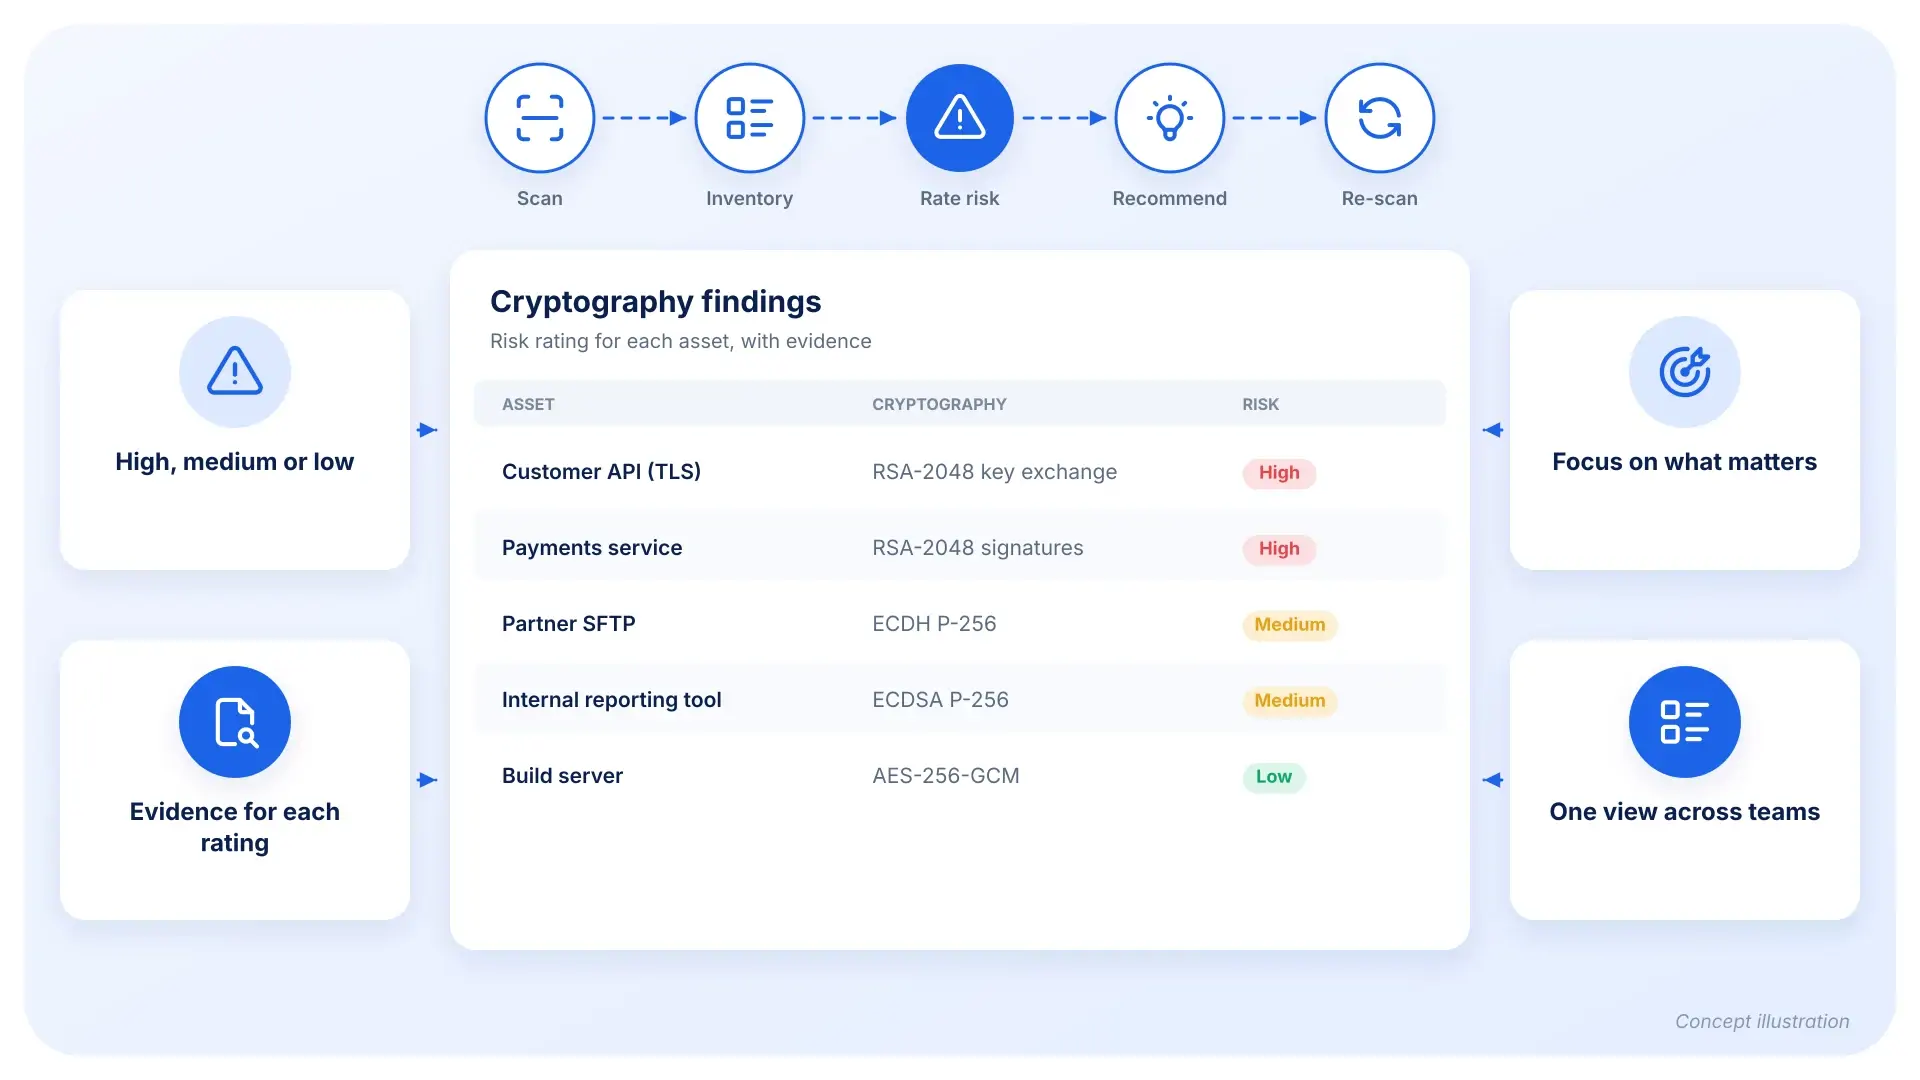
Most organisations cannot say where RSA and ECC are used today. Cryptography sits in application code, third-party libraries, TLS settings, certificates and stored secrets, spread across many teams. Without a clear inventory, post-quantum migration cannot be planned or prioritised. Cryptography Inventory & Risk Assessment scans these sources automatically, builds a cryptography inventory (CBOM), rates each asset high, medium or low risk with evidence, and recommends the next step.
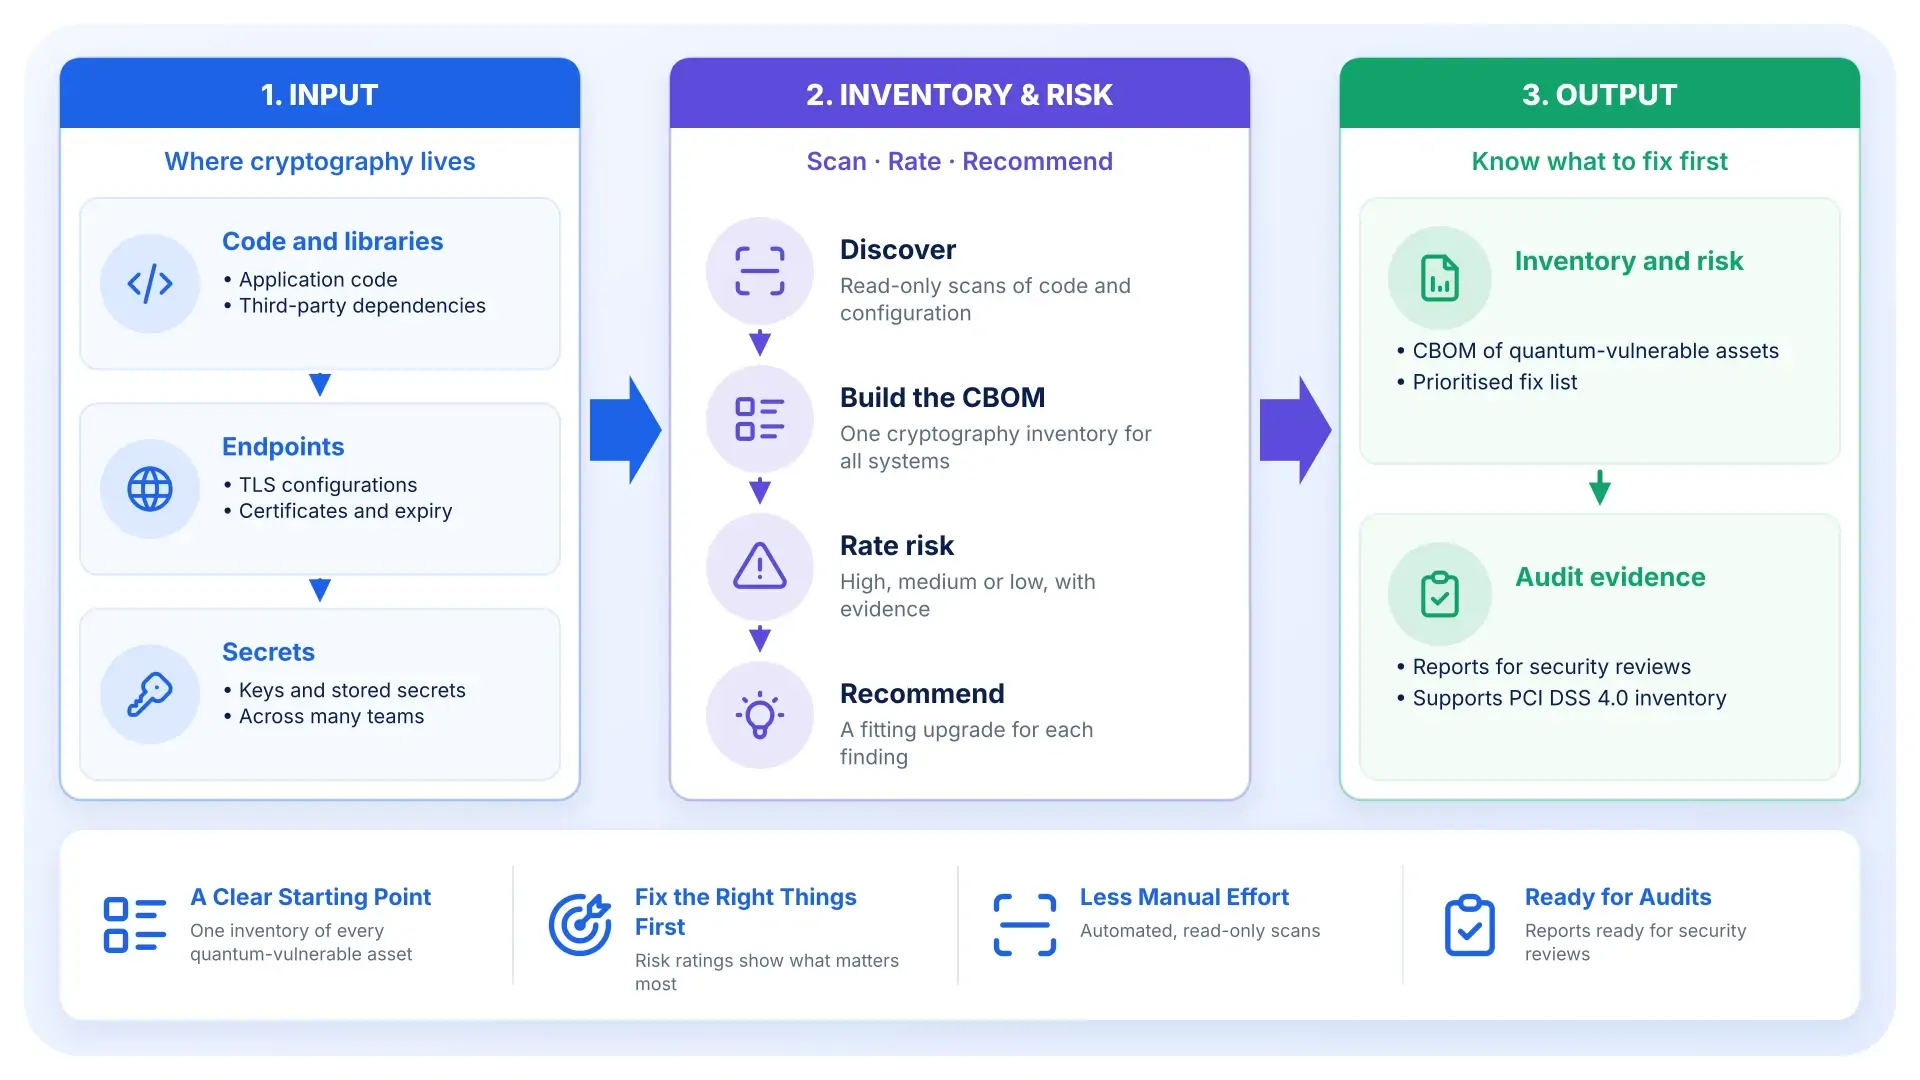
Scans code, dependencies, TLS configurations, certificates (including expiry) and secrets
Produces a cryptography bill of materials (CBOM)
Rates each asset high, medium or low, with evidence and a recommended fix
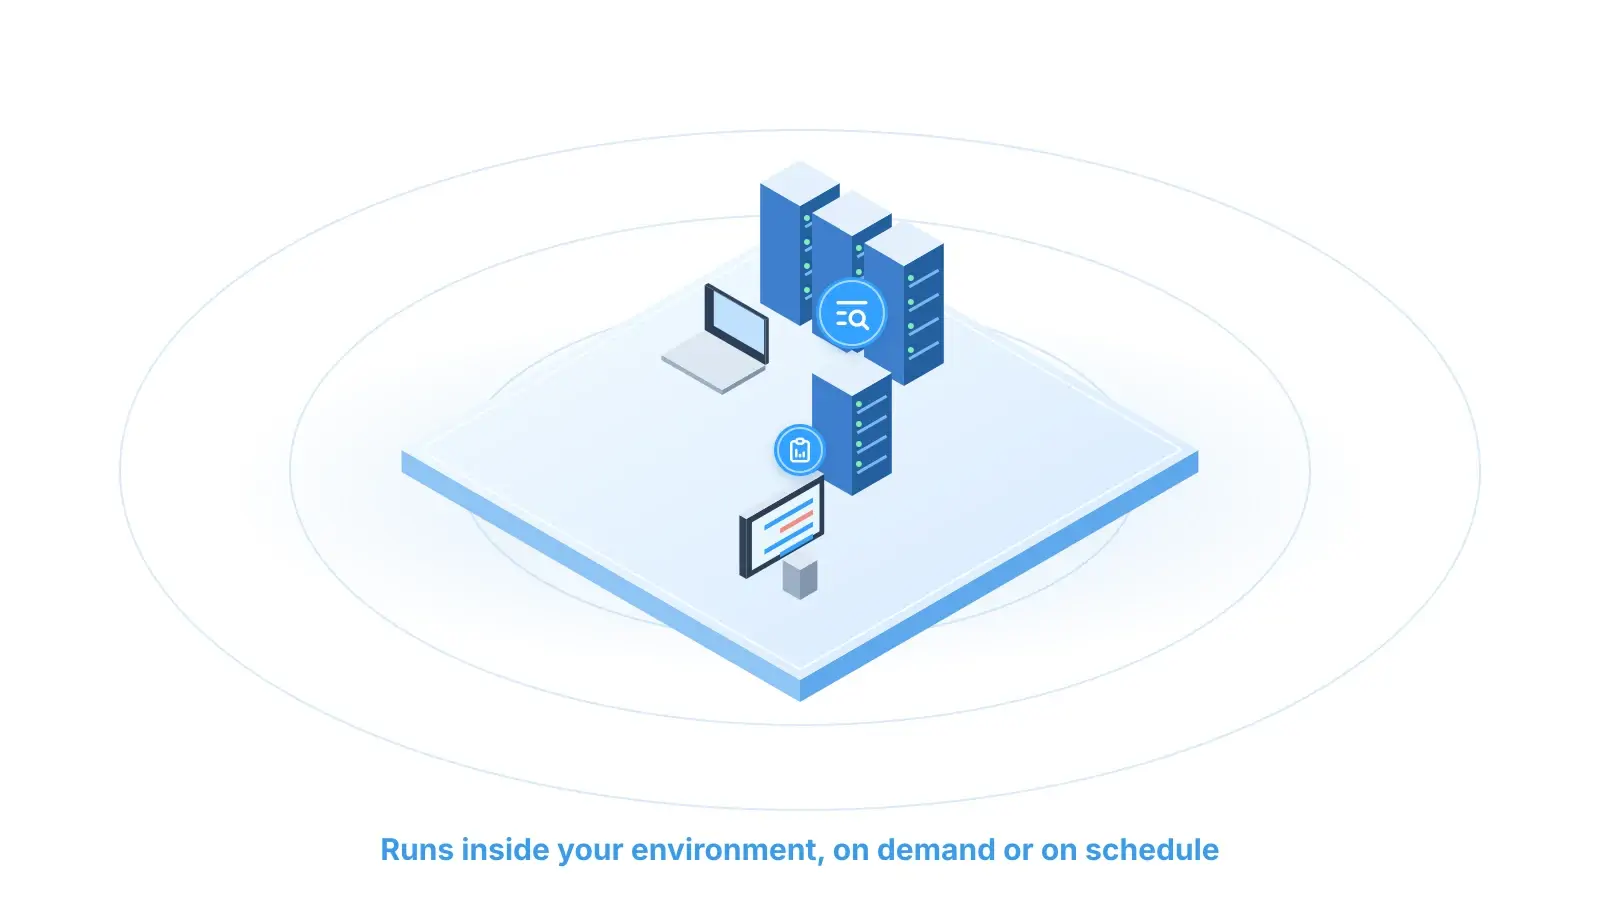
Runs on demand or on a schedule
Scans code, dependencies, TLS configurations, certificates (including expiry) and secrets
Produces a cryptography bill of materials (CBOM)
Rates each asset high, medium or low, with evidence and a recommended fix
Runs on demand or on a schedule
Turns post-quantum migration into a planned, prioritised programme
Replaces slow manual inventories that miss assets
Supports audit needs such as the PCI DSS 4.0 cipher inventory
Turns post-quantum migration into a planned, prioritised programme
Replaces slow manual inventories that miss assets
Supports audit needs such as the PCI DSS 4.0 cipher inventory
Where It Fits
Environments where cryptography is spread across many systems and teams.
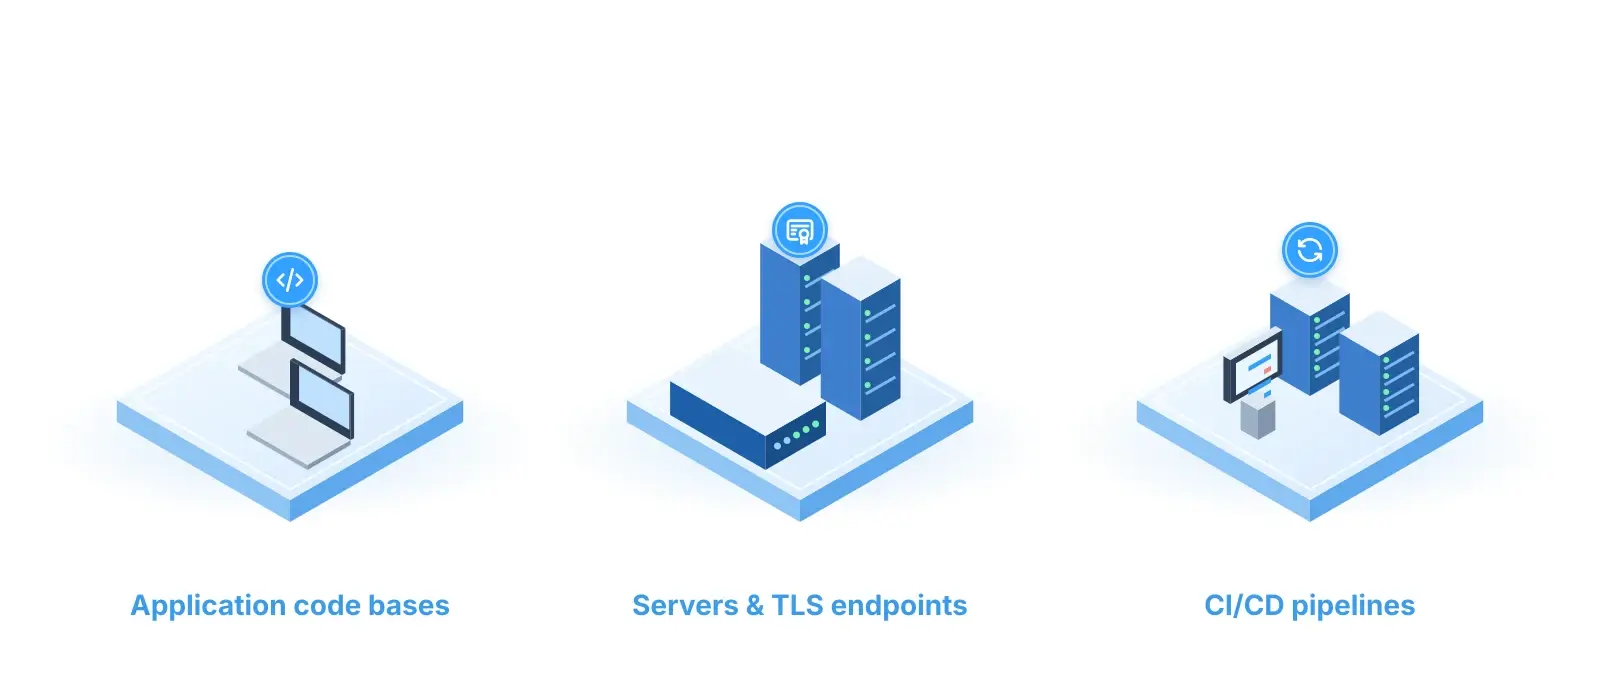
Application Code Bases
Source code and third-party libraries are scanned to find where RSA, ECC and weak algorithms are called.
Servers and TLS Endpoints
TLS settings and certificates on servers and gateways are checked for quantum-vulnerable key exchange and upcoming expiry.
CI/CD Pipelines
Scheduled scans in the build pipeline keep the inventory current as code and configurations change.
Business Impact
Practical outcomes of knowing where cryptography is used.
A Clear Starting Point
One inventory shows every quantum-vulnerable asset across teams and systems.
Fix the Right Things First
Risk ratings focus effort on the assets that matter most.
Less Manual Effort
Automated scans replace spreadsheets and interviews.
Ready for Audits
Reports give evidence for security reviews and compliance checks.
Key Capabilities
What the assessment enables for security and engineering teams.
Discover Cryptography Everywhere
Finds algorithms, keys, certificates and protocols across code and configuration.
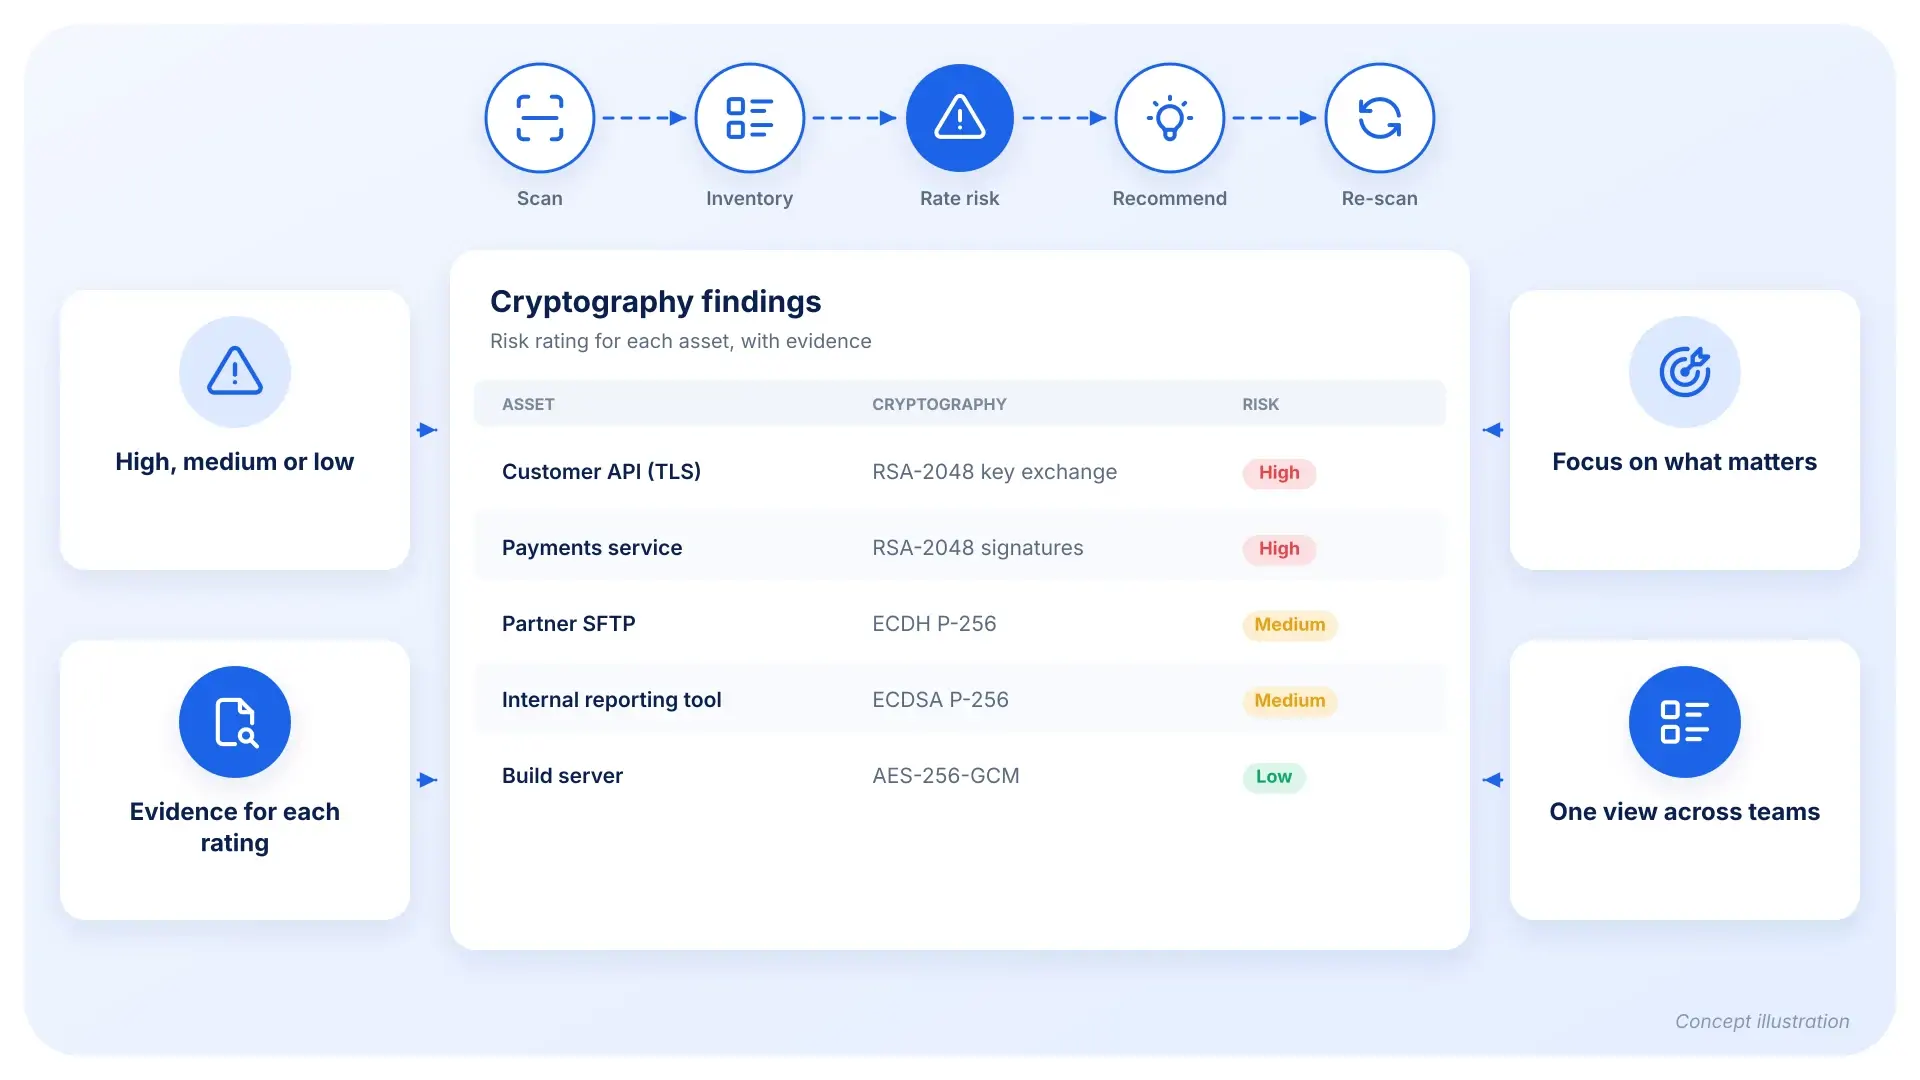
Rate Every Asset
Recommend the Next Step
Keep It Current
Deployment & Integration
The assessment runs inside the customer’s environment and reads, but does not change, the systems it scans.
Inside Your Environment: Code and configurations stay on the customer’s systems.
Read-Only Scans: Systems are inspected, not modified.
Fits the Pipeline: Can run on demand or as a scheduled step in existing CI/CD.
Delivered with Partners: KPS and its partners adapt the scope to each environment, starting with a proof of concept.
Designed to fit your setup
Reference scenarios
A financial services organisation needs to start its post-quantum transition plan. A first scan of its main platforms produces an inventory and risk ranking that becomes the basis of the plan.
Key Outcomes
Complete view of quantum-vulnerable assets
Prioritised migration list
Evidence for leadership and auditors

Contact Us
For any questions, support requests or partnership opportunities, please reach out to us via:


