
Quantum-Safe API Gateway
Add post-quantum protection to customer, adviser and partner APIs, without changing the applications behind them.
Quantum-safe APIs for financial services
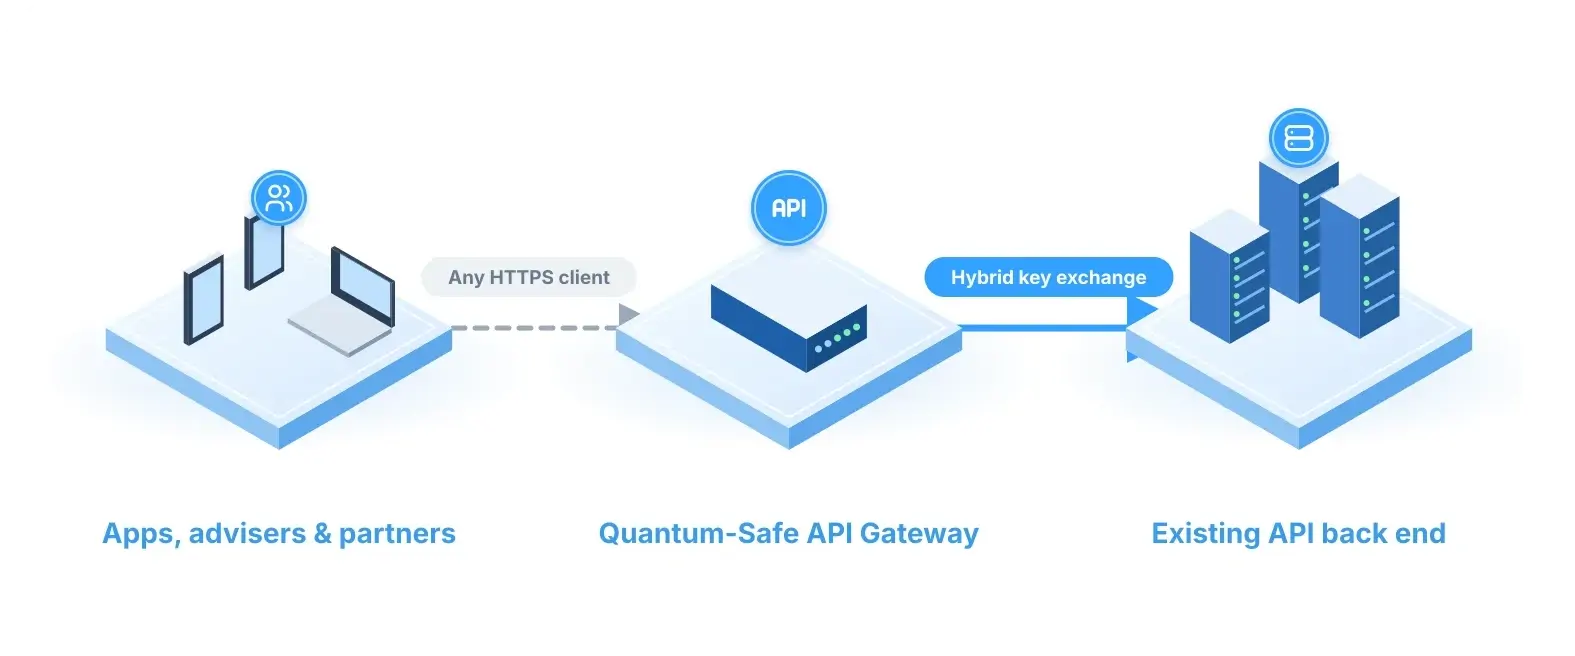
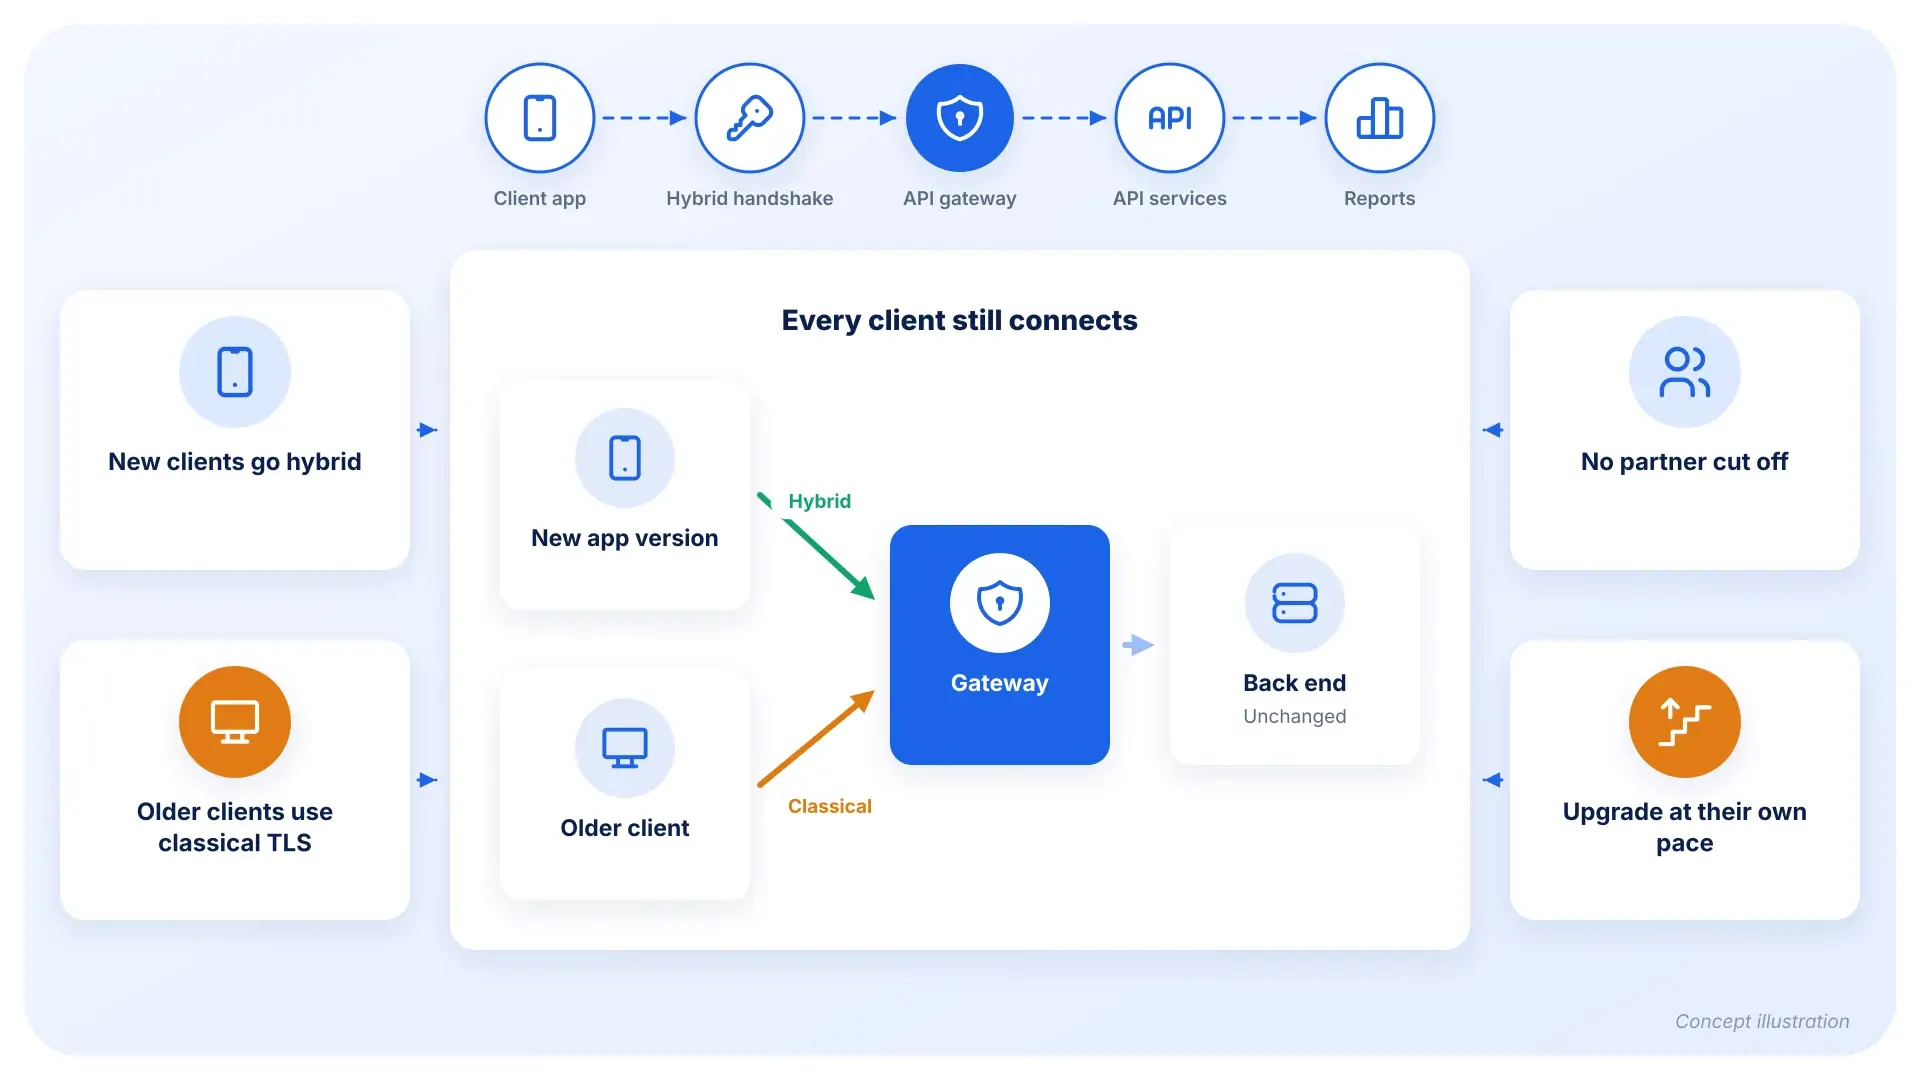
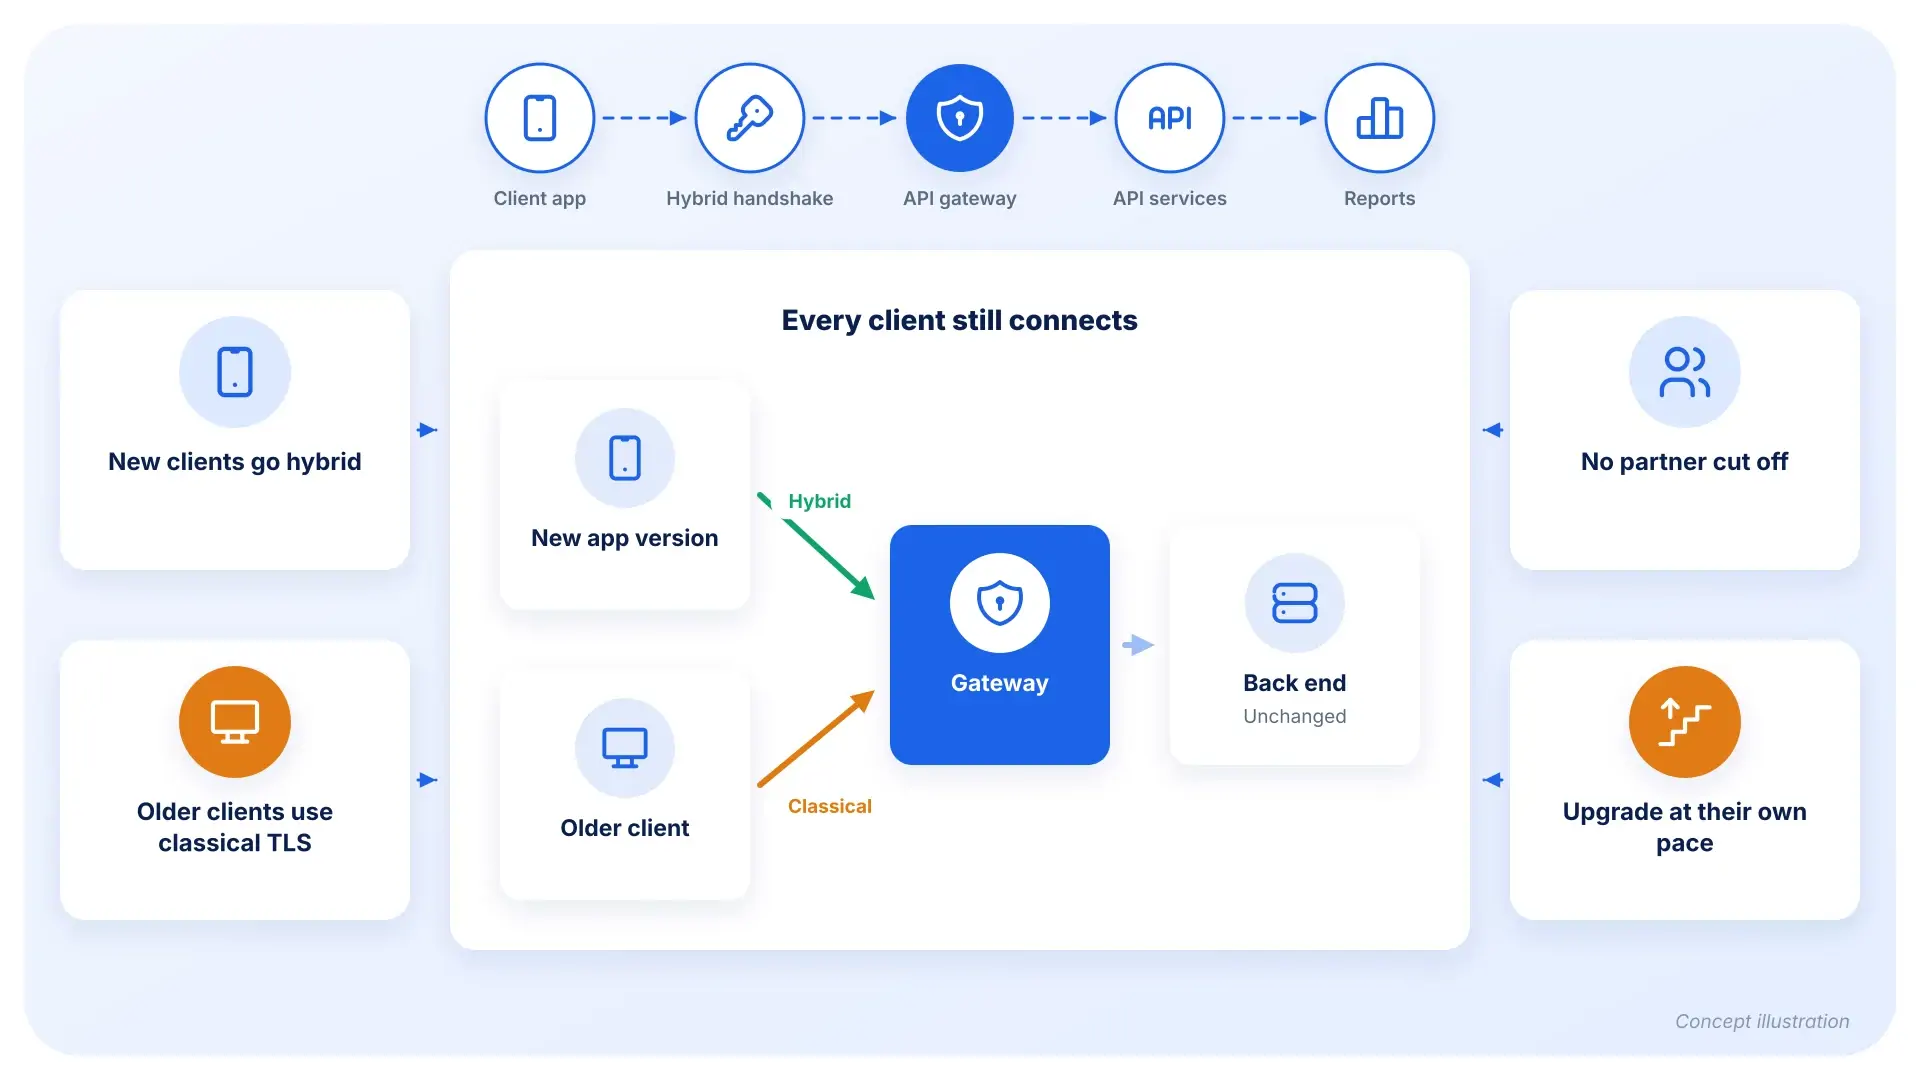
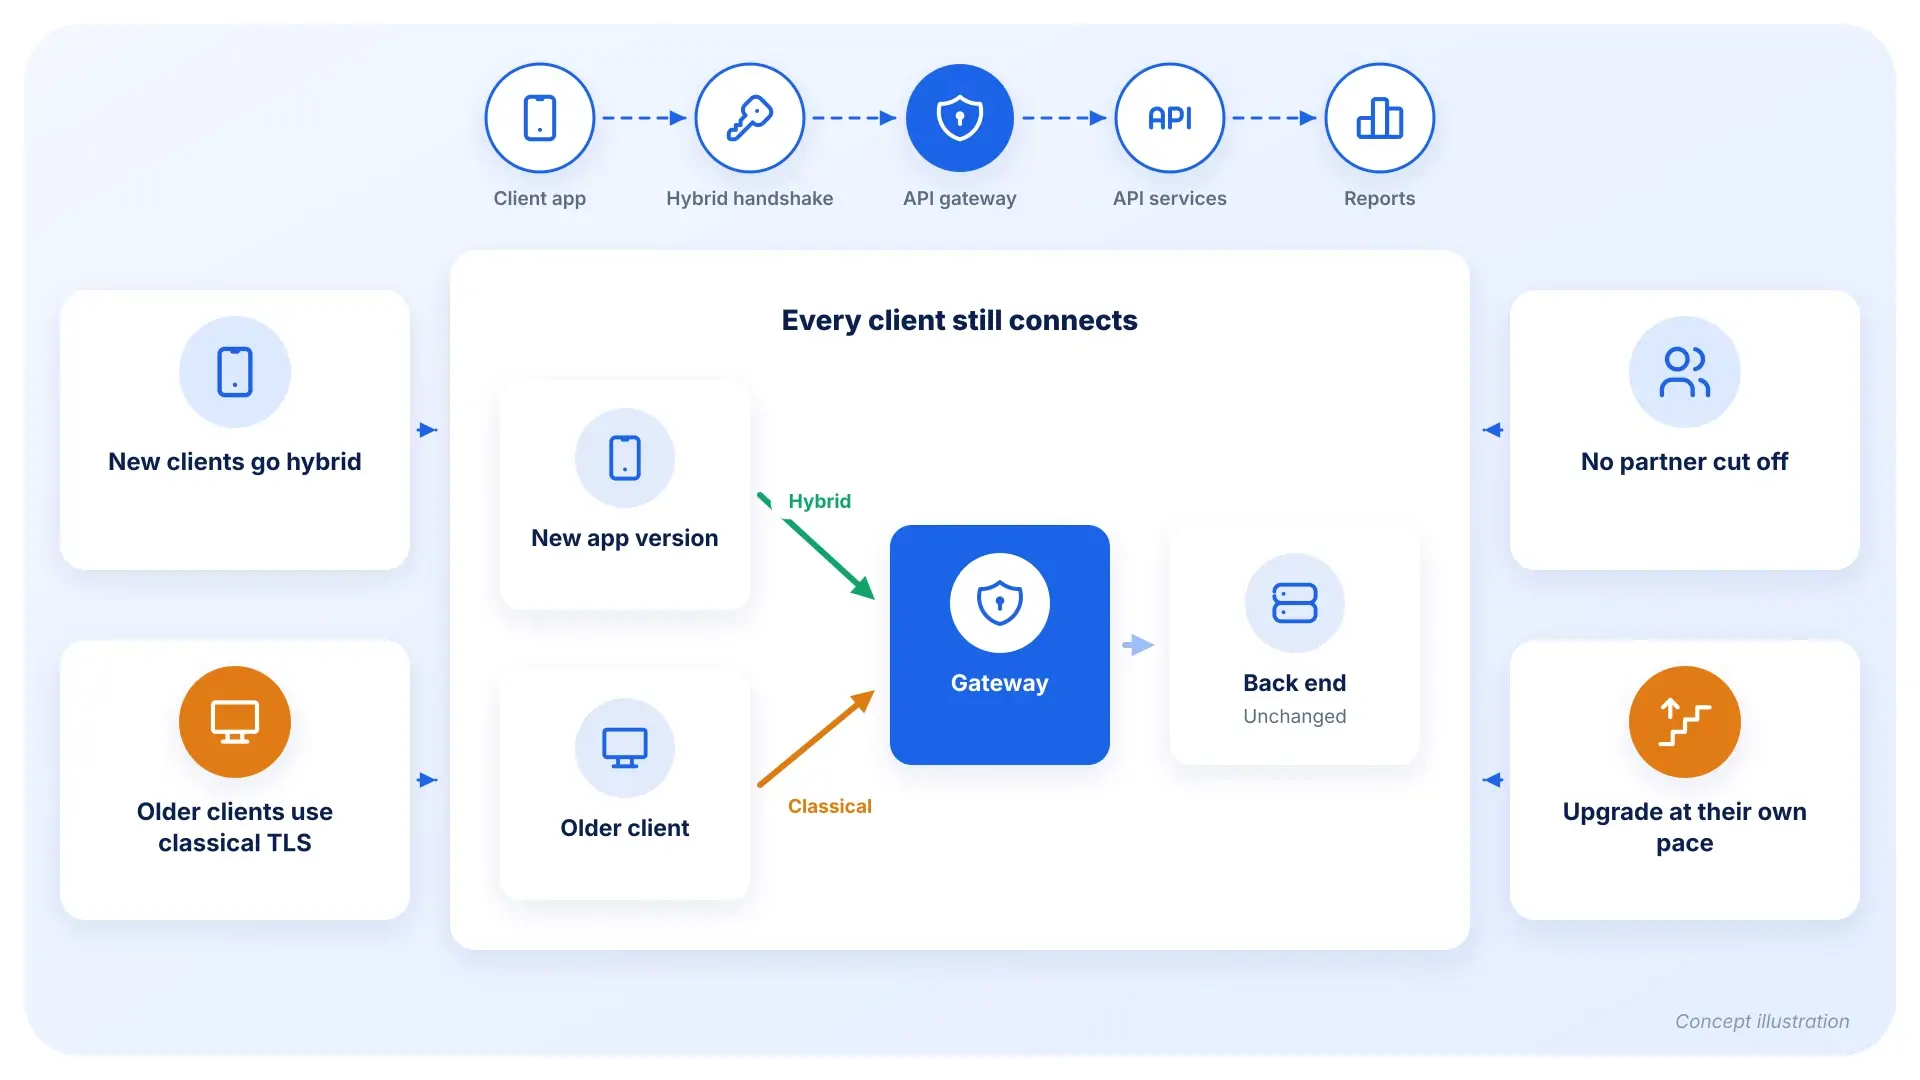
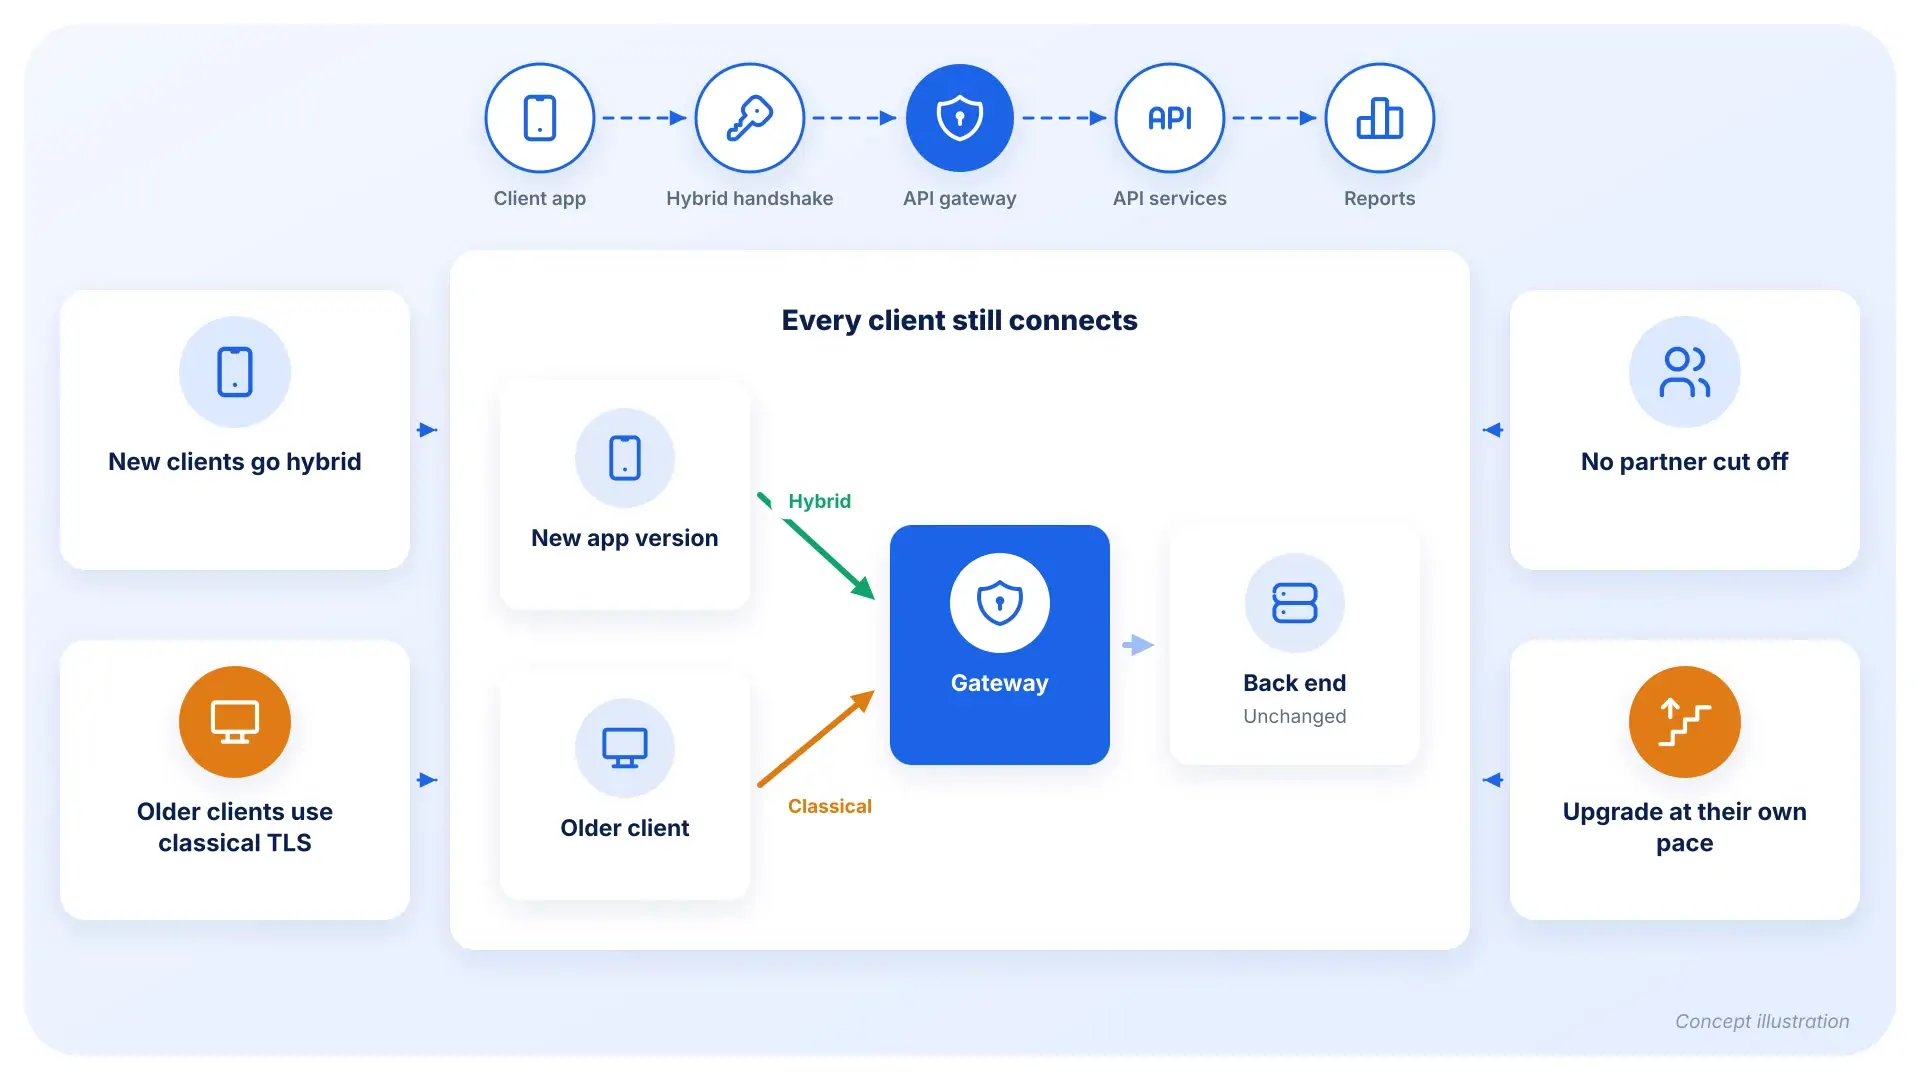
Banks, wealth platforms and fintechs run APIs used by mobile apps, web portals, advisers and partners. Client and transaction data sent over these APIs could be recorded today and decrypted later. Upgrading every back-end service and every client at once is not practical. The Quantum-Safe API Gateway sits at the API entry point and adds hybrid post-quantum key exchange to inbound HTTPS traffic, so data in transit is protected while back-end services and older clients keep working.
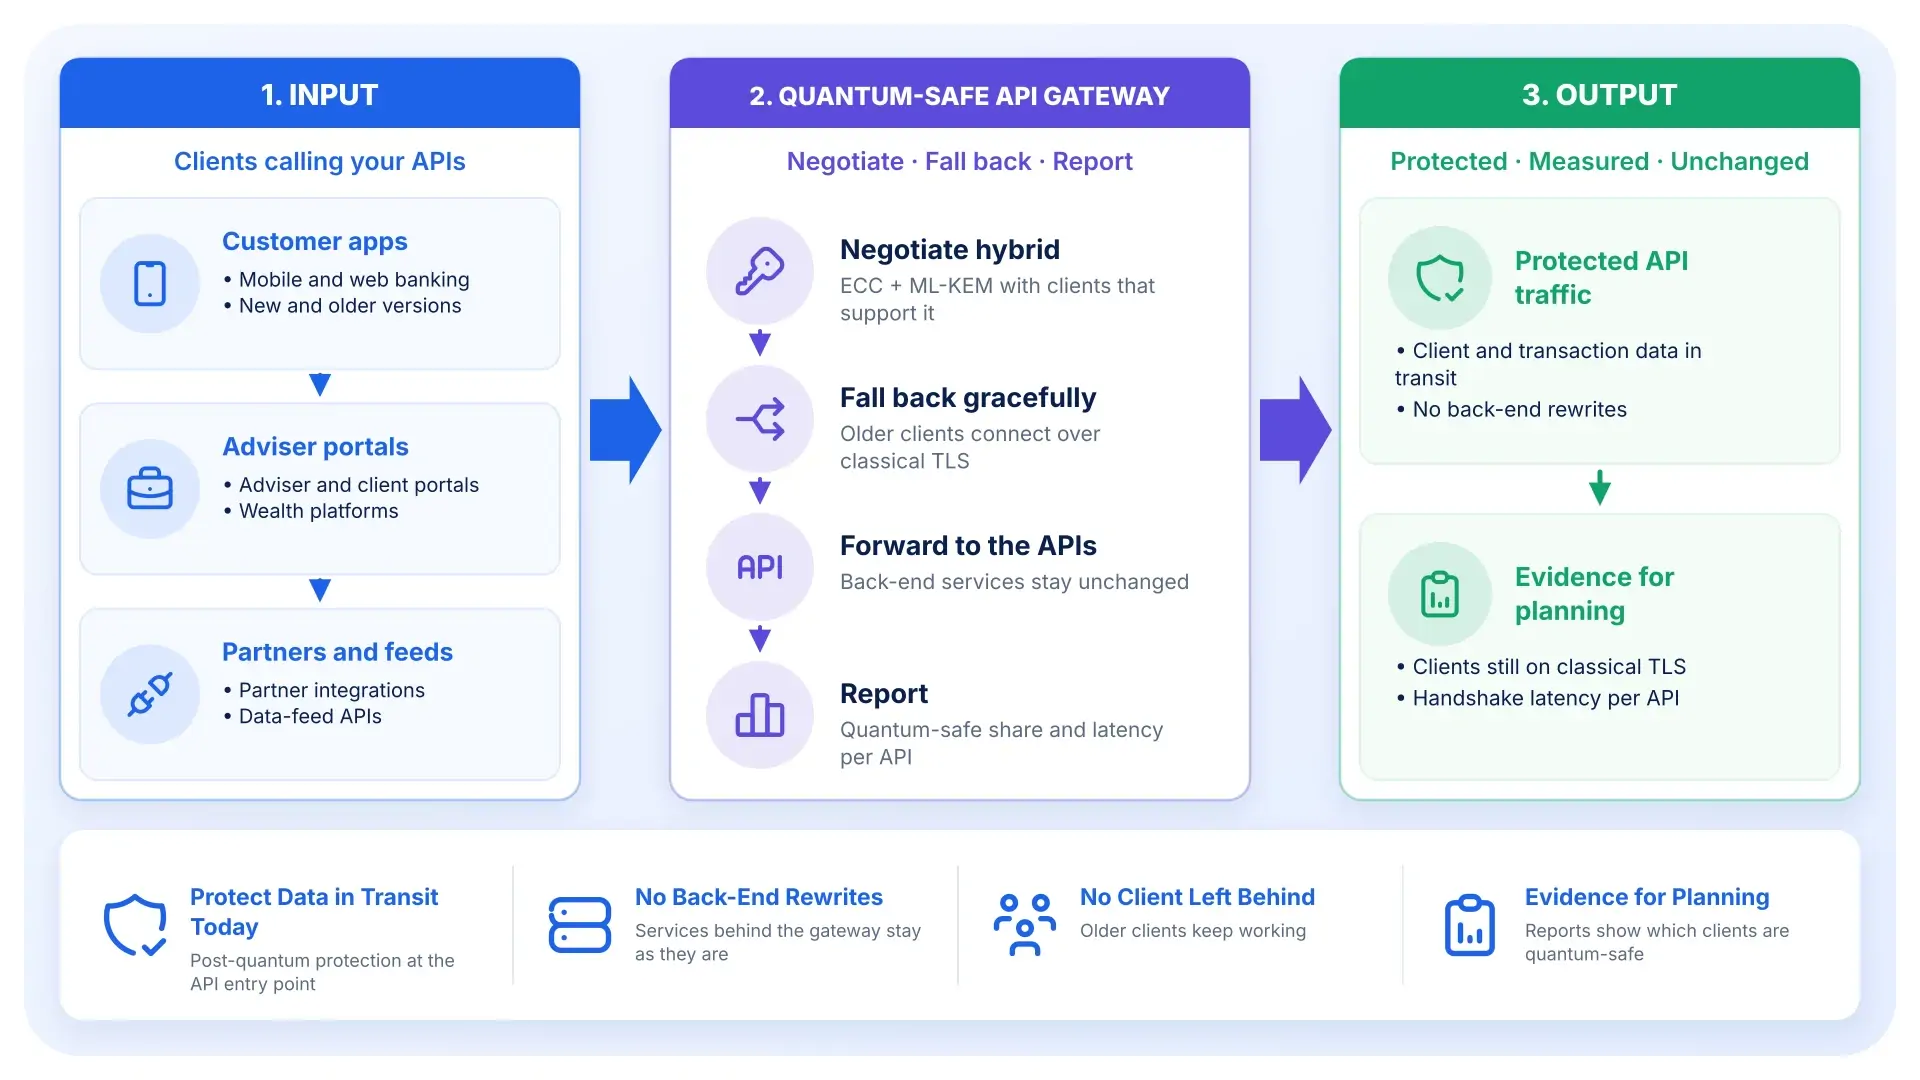
Hybrid post-quantum key exchange (ECC + ML-KEM) for inbound API traffic
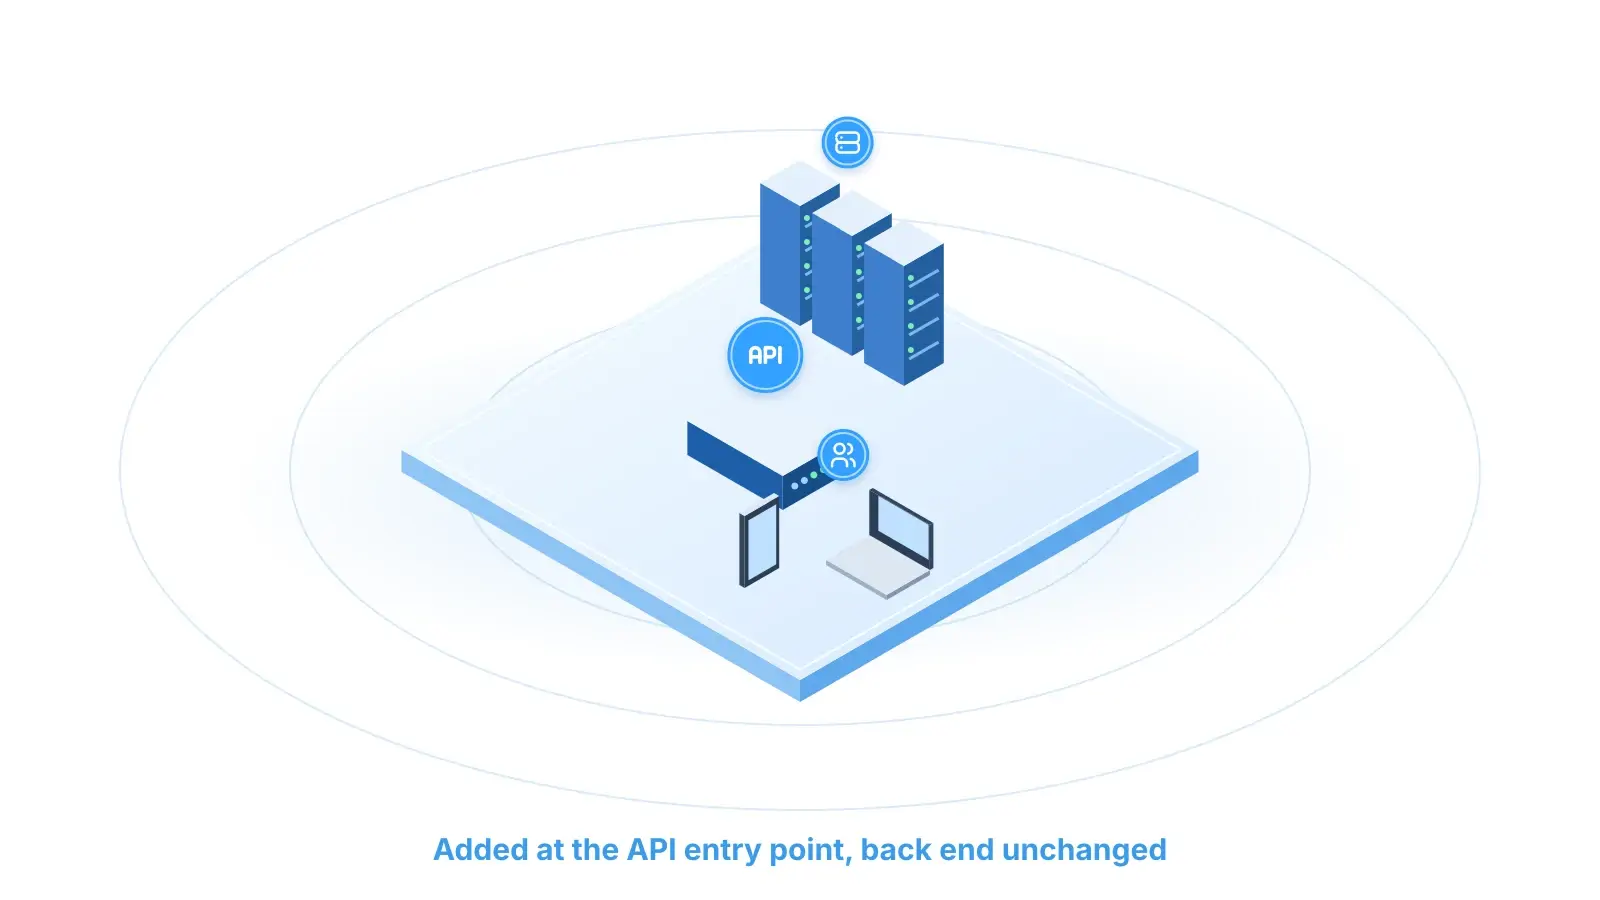
Placed in front of existing APIs; no changes to back-end services
Older clients still connect over classical TLS
Latency and compatibility reporting for every API
Hybrid post-quantum key exchange (ECC + ML-KEM) for inbound API traffic
Placed in front of existing APIs; no changes to back-end services
Older clients still connect over classical TLS
Latency and compatibility reporting for every API
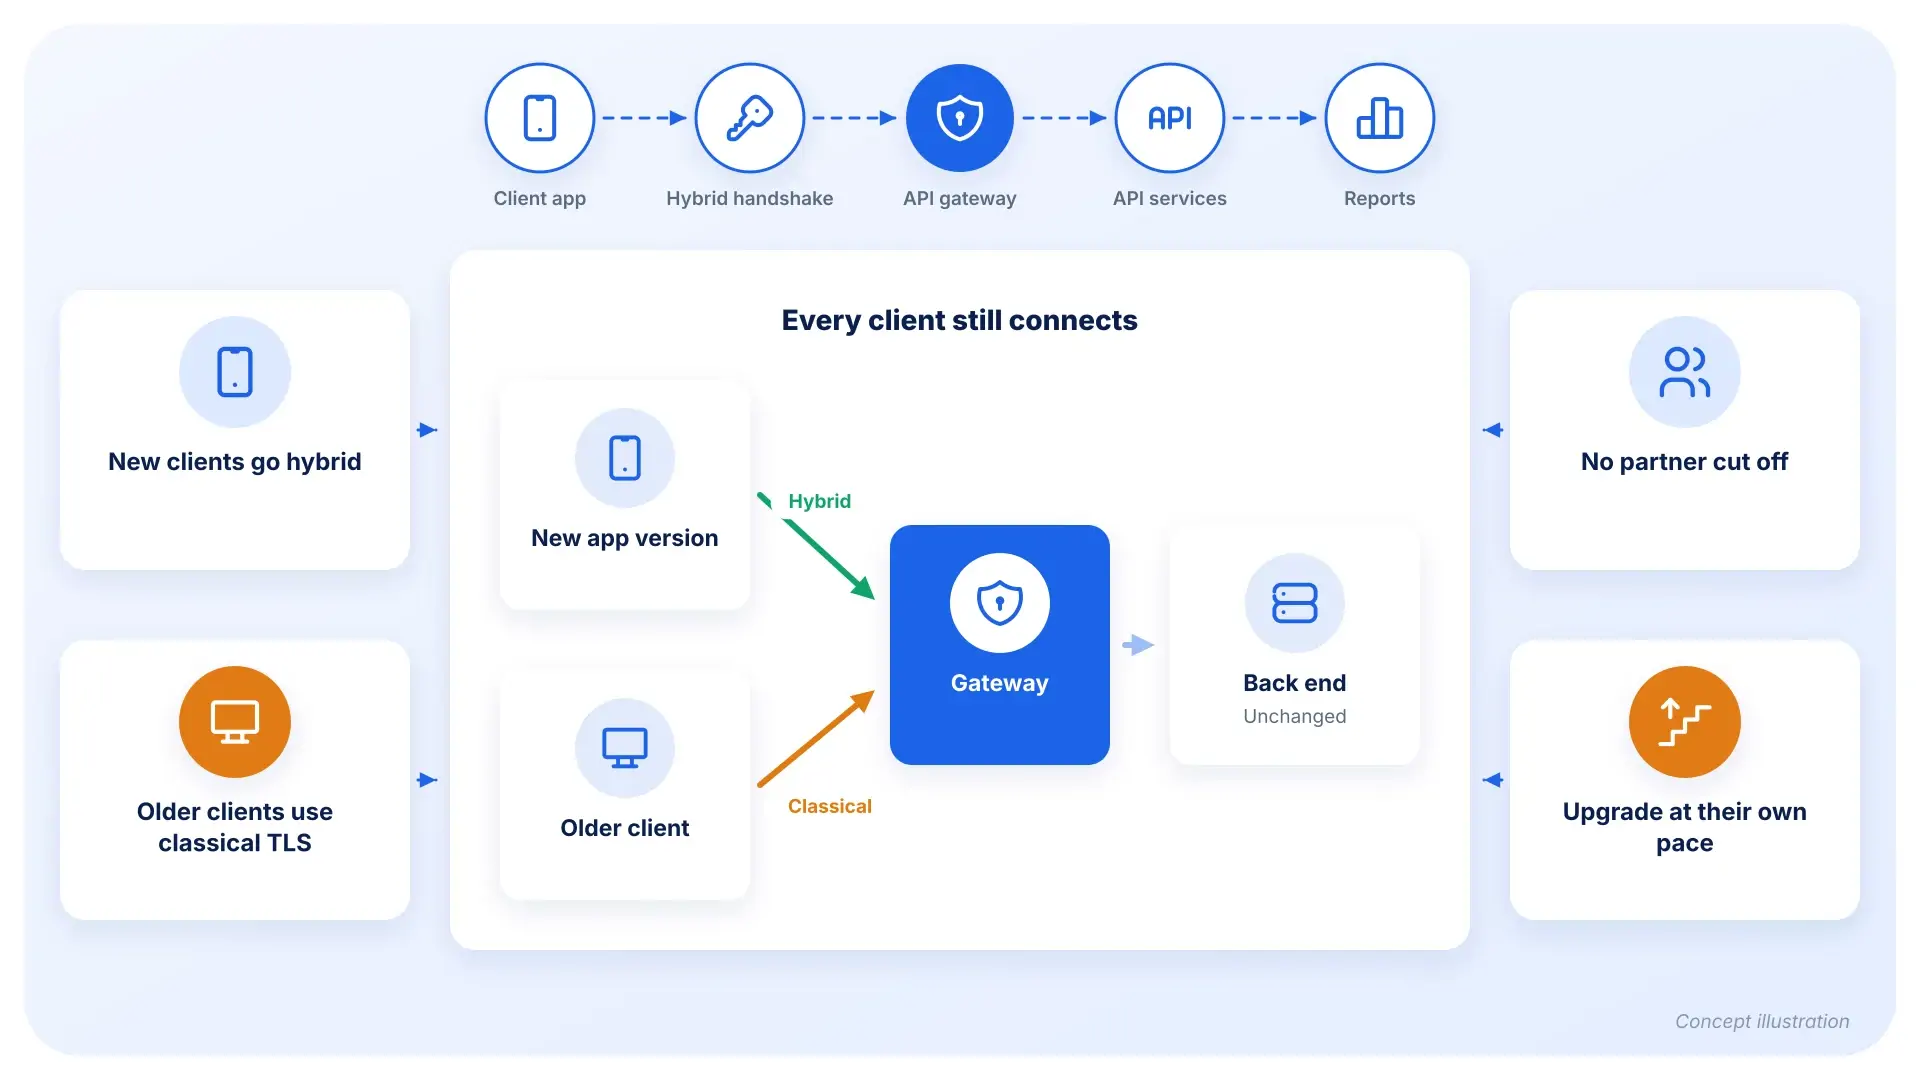
Protects client and transaction data against “harvest now, decrypt later”
Avoids rewriting back-end services for post-quantum cryptography
Lets teams move API by API, with evidence at each step
Protects client and transaction data against “harvest now, decrypt later”
Avoids rewriting back-end services for post-quantum cryptography
Lets teams move API by API, with evidence at each step
Where It Fits
API environments where many different clients connect to the same services.
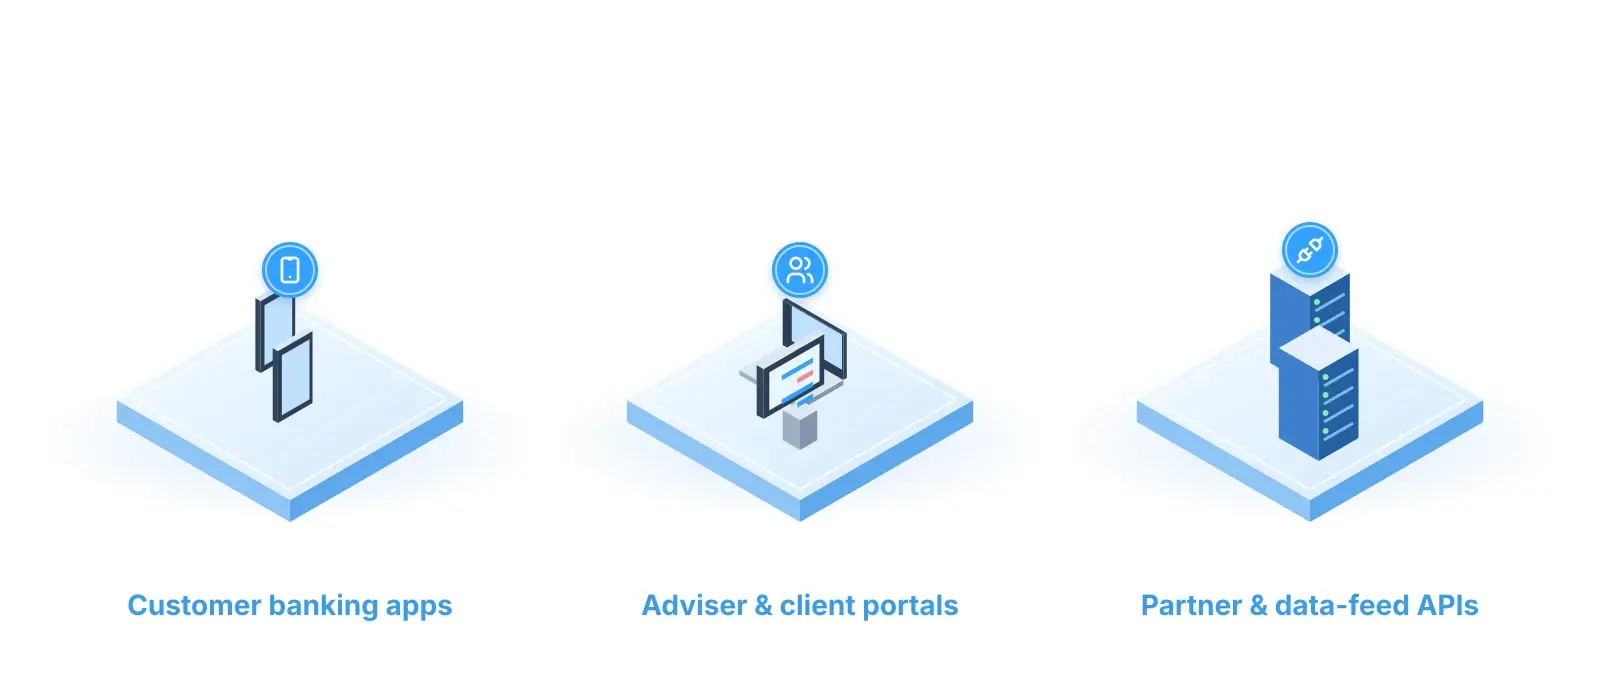
Customer Banking Apps
Mobile and web apps reach account and payment APIs through the gateway; modern app platforms already support hybrid key exchange.
Adviser and Client Portals
Portals used by advisers and their clients gain quantum-safe connections without a change to the portal code.
Partner and Data-Feed APIs
APIs used by partners and data providers are protected, while partners that cannot upgrade yet still connect.
Business Impact
Practical outcomes of adding a quantum-safe layer at the API entry point.
Protect Data in Transit Today
Client and transaction data gains post-quantum protection without waiting for every system to change.
No Back-End Rewrites
Services behind the gateway stay as they are.
No Client Left Behind
Older apps and partners keep working while newer ones use post-quantum key exchange.
Evidence for Planning
Reports show which clients already connect quantum-safe and what the latency cost is.
Key Capabilities
What the gateway enables for platform and security teams.
Hybrid Key Exchange for HTTPS
Negotiates ECC + ML-KEM with clients that support it.
Graceful Fallback
Connection Reporting
Performance Checks
Deployment & Integration
The gateway is added at the API entry point, inside existing infrastructure.
In Front of Existing APIs: Deployed at the entry point, alongside or behind the current API management layer.
On-Premise or Cloud: Runs on standard servers, virtual machines or cloud instances in the customer’s environment.
Works with Existing Certificates: Uses the organisation’s current certificates and key-management setup.
Delivered with Partners: KPS and its partners adapt the rollout to each API platform, starting with a proof of concept.
Designed to fit your setup
Reference scenarios
A wealth platform exposes APIs to its client app, adviser portal and many partner integrations. The gateway adds hybrid post-quantum key exchange at the entry point, while partners that have not upgraded still connect.
Key Outcomes
Client and adviser traffic protected in transit
No change to platform services
Visibility of partners still on classical TLS

Contact Us
For any questions, support requests or partnership opportunities, please reach out to us via:


