
Quantum-Safe Gateway
Protect connections from existing devices, sites and APIs against future quantum attacks, without changing the systems behind them.
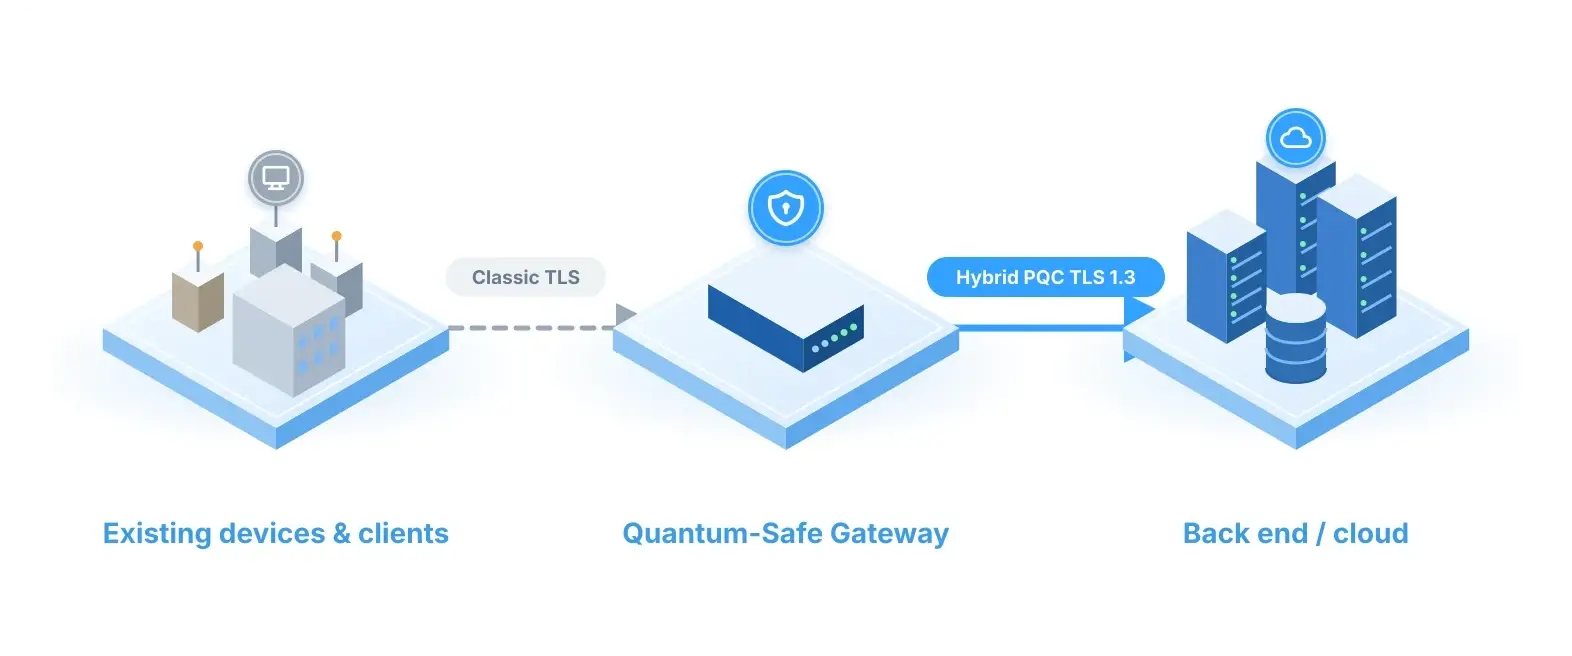
Quantum-safe connections for systems that cannot change quickly
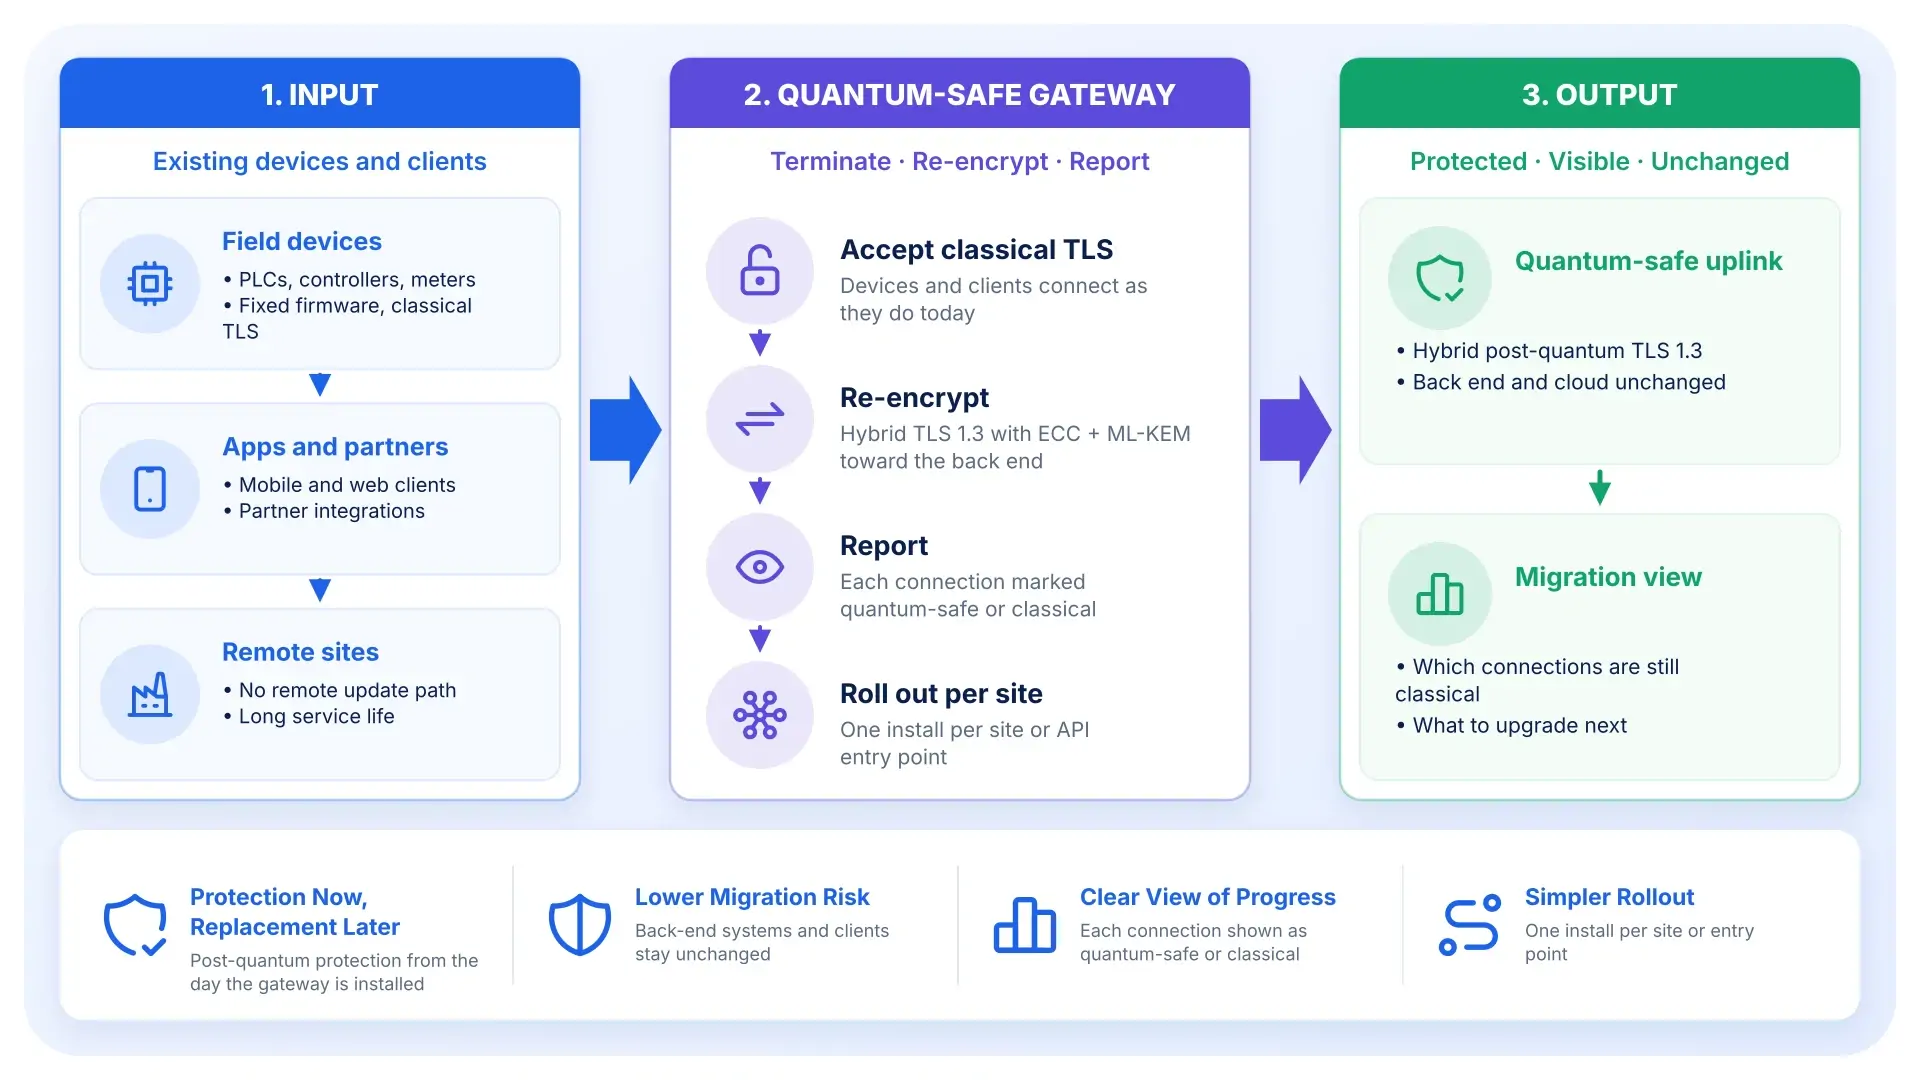
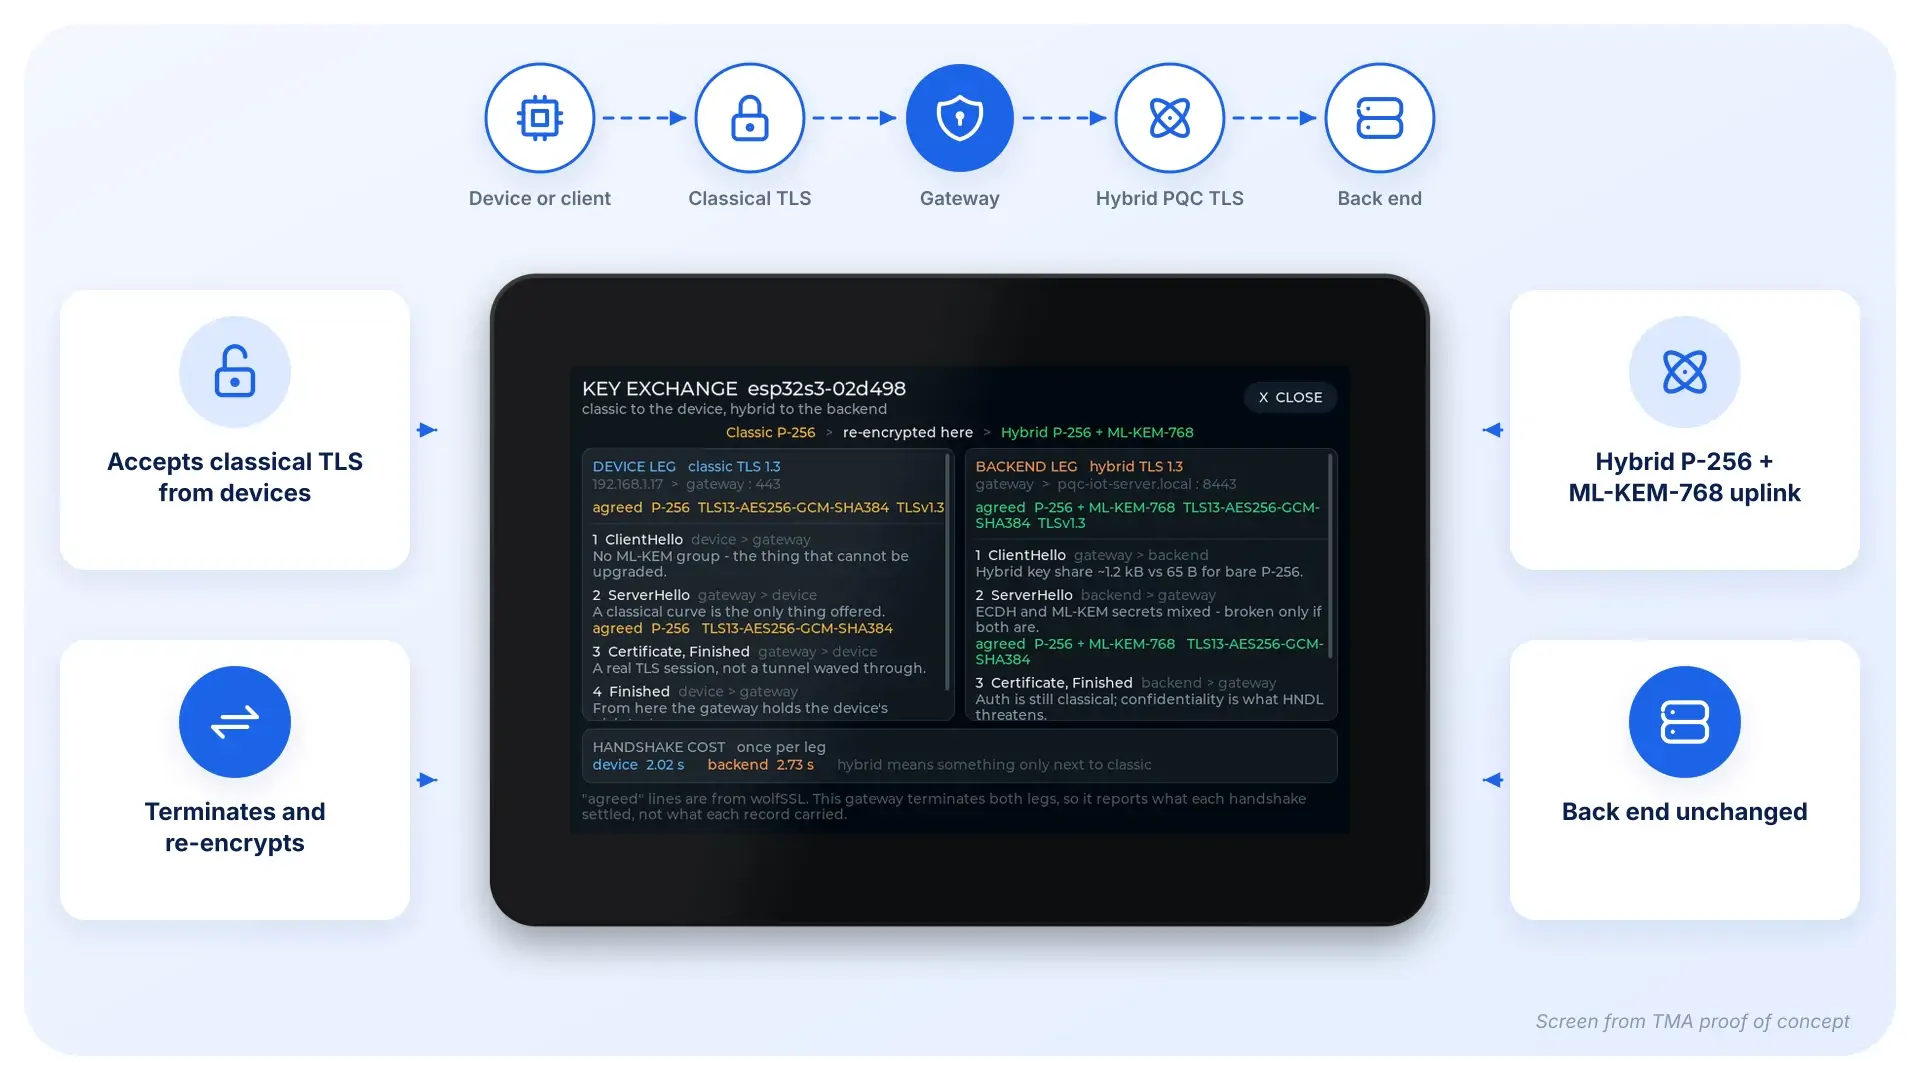
Many organisations run equipment and applications that will stay in service for years: field devices with fixed firmware, sites without remote updates, and APIs used by many apps and partners. Replacing or rewriting all of them for post-quantum cryptography is rarely realistic. The Quantum-Safe Gateway is placed in front of these systems and upgrades their connections to hybrid post-quantum TLS 1.3 (ECC + ML-KEM), so data leaving a site or reaching an API is protected while everything behind it keeps working as before.
Hybrid post-quantum TLS 1.3 using the NIST ML-KEM standard alongside ECC
Inline deployment, with no changes to devices, apps or back-end systems
One gateway per site or per API entry point
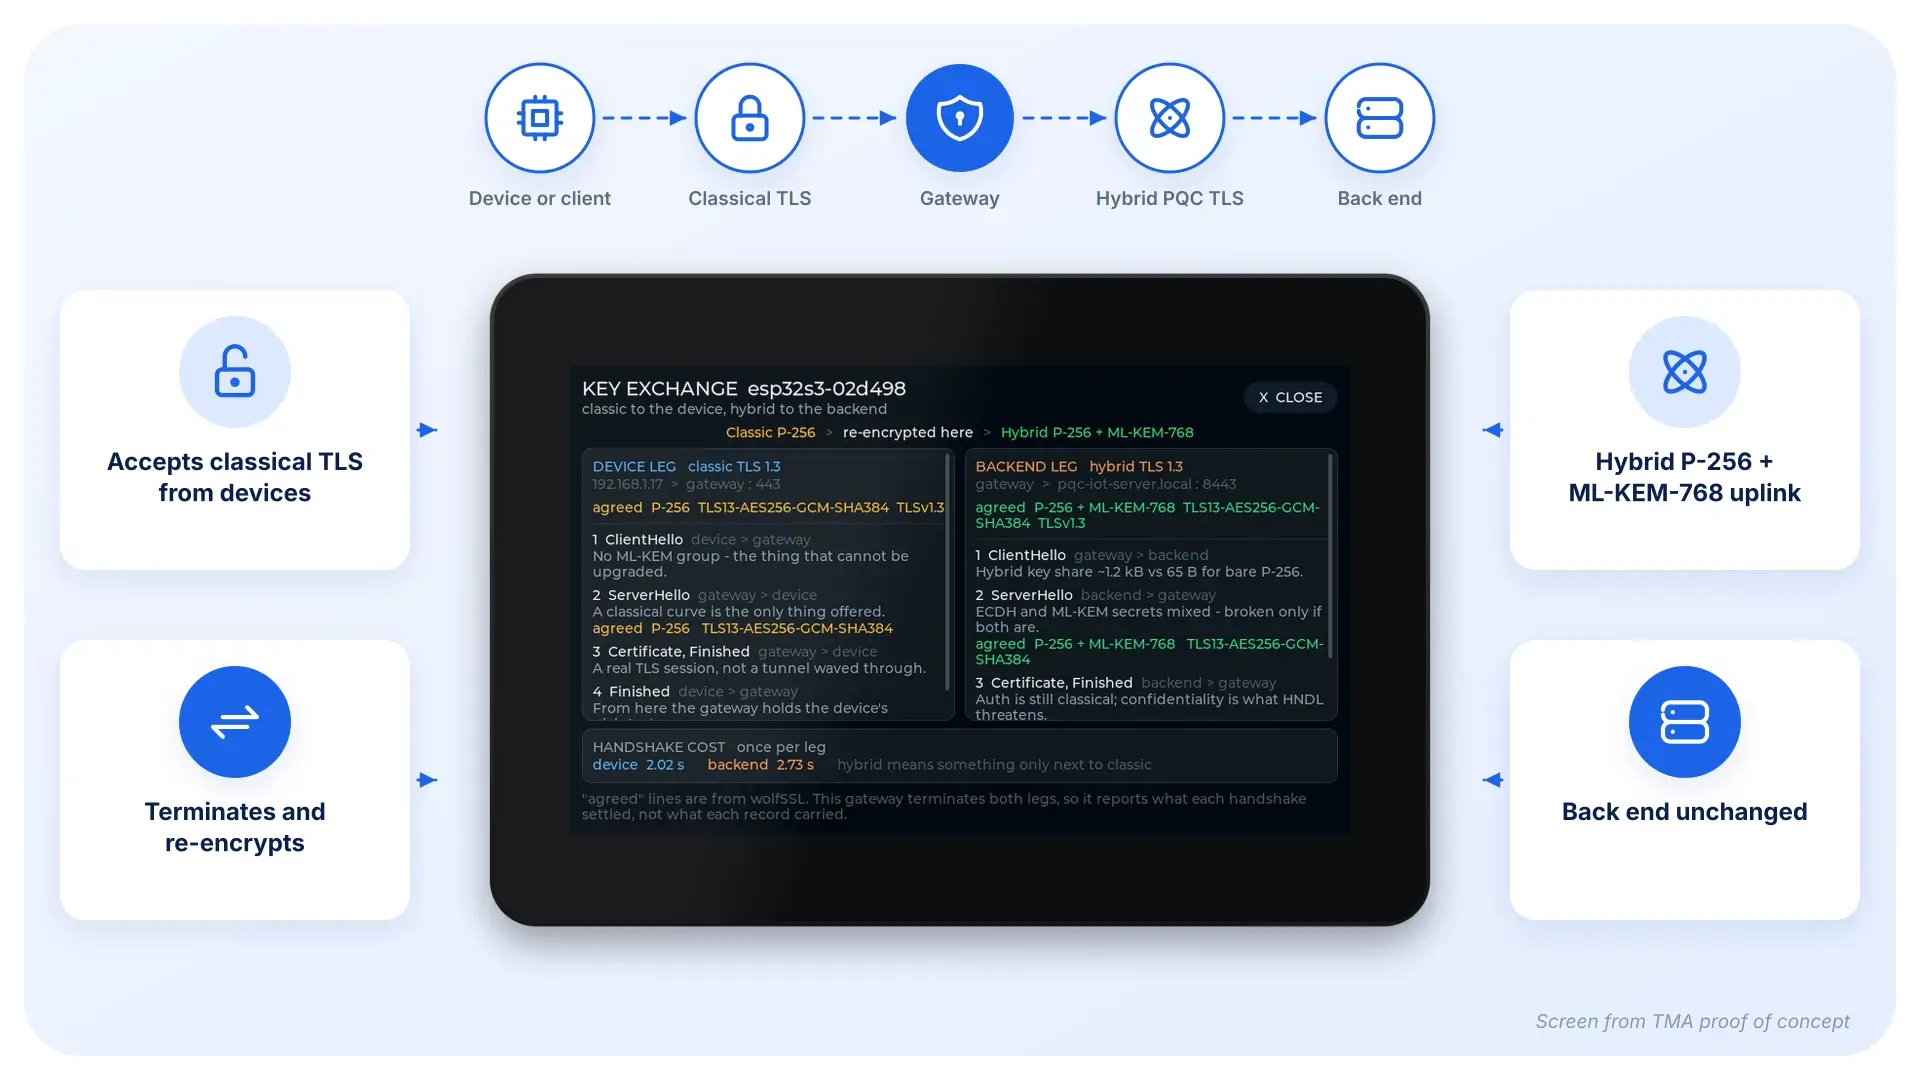
Hybrid post-quantum TLS 1.3 using the NIST ML-KEM standard alongside ECC
Inline deployment, with no changes to devices, apps or back-end systems
One gateway per site or per API entry point
Protects long-lived data in transit from “harvest now, decrypt later”
Avoids costly device replacement or application rewrites
Lets organisations move to post-quantum security one site or one API at a time
Protects long-lived data in transit from “harvest now, decrypt later”
Avoids costly device replacement or application rewrites
Lets organisations move to post-quantum security one site or one API at a time
Where It Fits
Operational environments where connections need protecting but the systems behind them are hard to change.
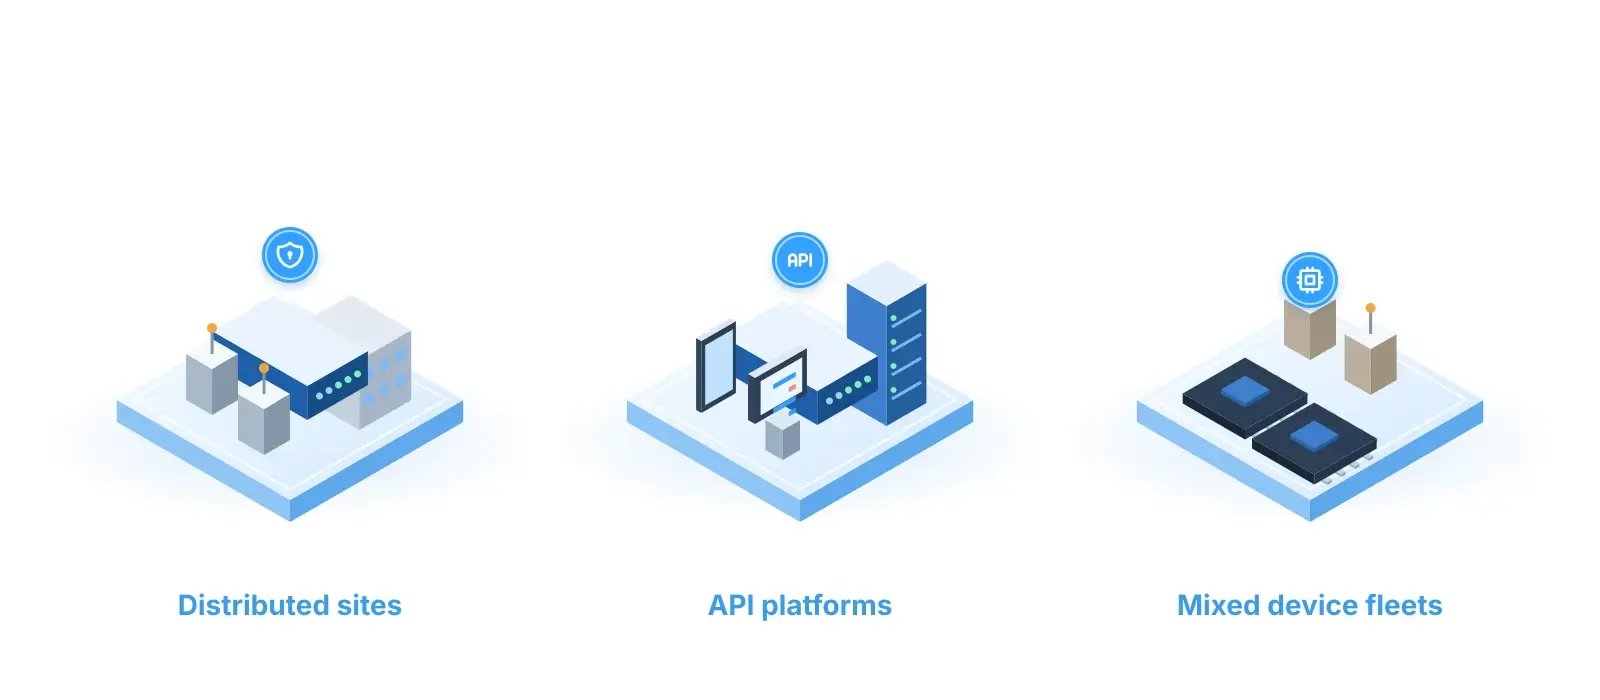
Distributed Sites with Legacy Equipment
Placed at each site, the gateway takes the existing TLS traffic from controllers, meters or devices and sends it on to the back end or cloud over hybrid post-quantum TLS.
Customer and Partner API Platforms
Placed in front of web, mobile and partner APIs, the gateway adds post-quantum key exchange to inbound HTTPS traffic while older clients still connect.
Mixed Old and New Device Fleets
Older devices connect through the gateway, while new devices can use the KPS Embedded PQC SDK directly, so both reach the same back end safely.
Business Impact
Practical outcomes of adding a quantum-safe layer in front of existing systems.
Protection Now, Replacement Later
Sites and APIs gain post-quantum protection today; devices and applications can be upgraded on their normal cycle.
Lower Migration Risk
Back-end systems and clients stay unchanged, so there is less to test and less to break.
Clear View of Progress
A dashboard shows which connections are already quantum-safe and which still use classical encryption.
Simpler Rollout
One install per site or entry point keeps deployment effort predictable.
Key Capabilities
What the gateway enables in day-to-day operations.
Upgrade Connections in Place
Accepts the classical TLS that devices and clients already use, and re-originates it as hybrid post-quantum TLS 1.3 toward the back end.
Keep Every Client Working
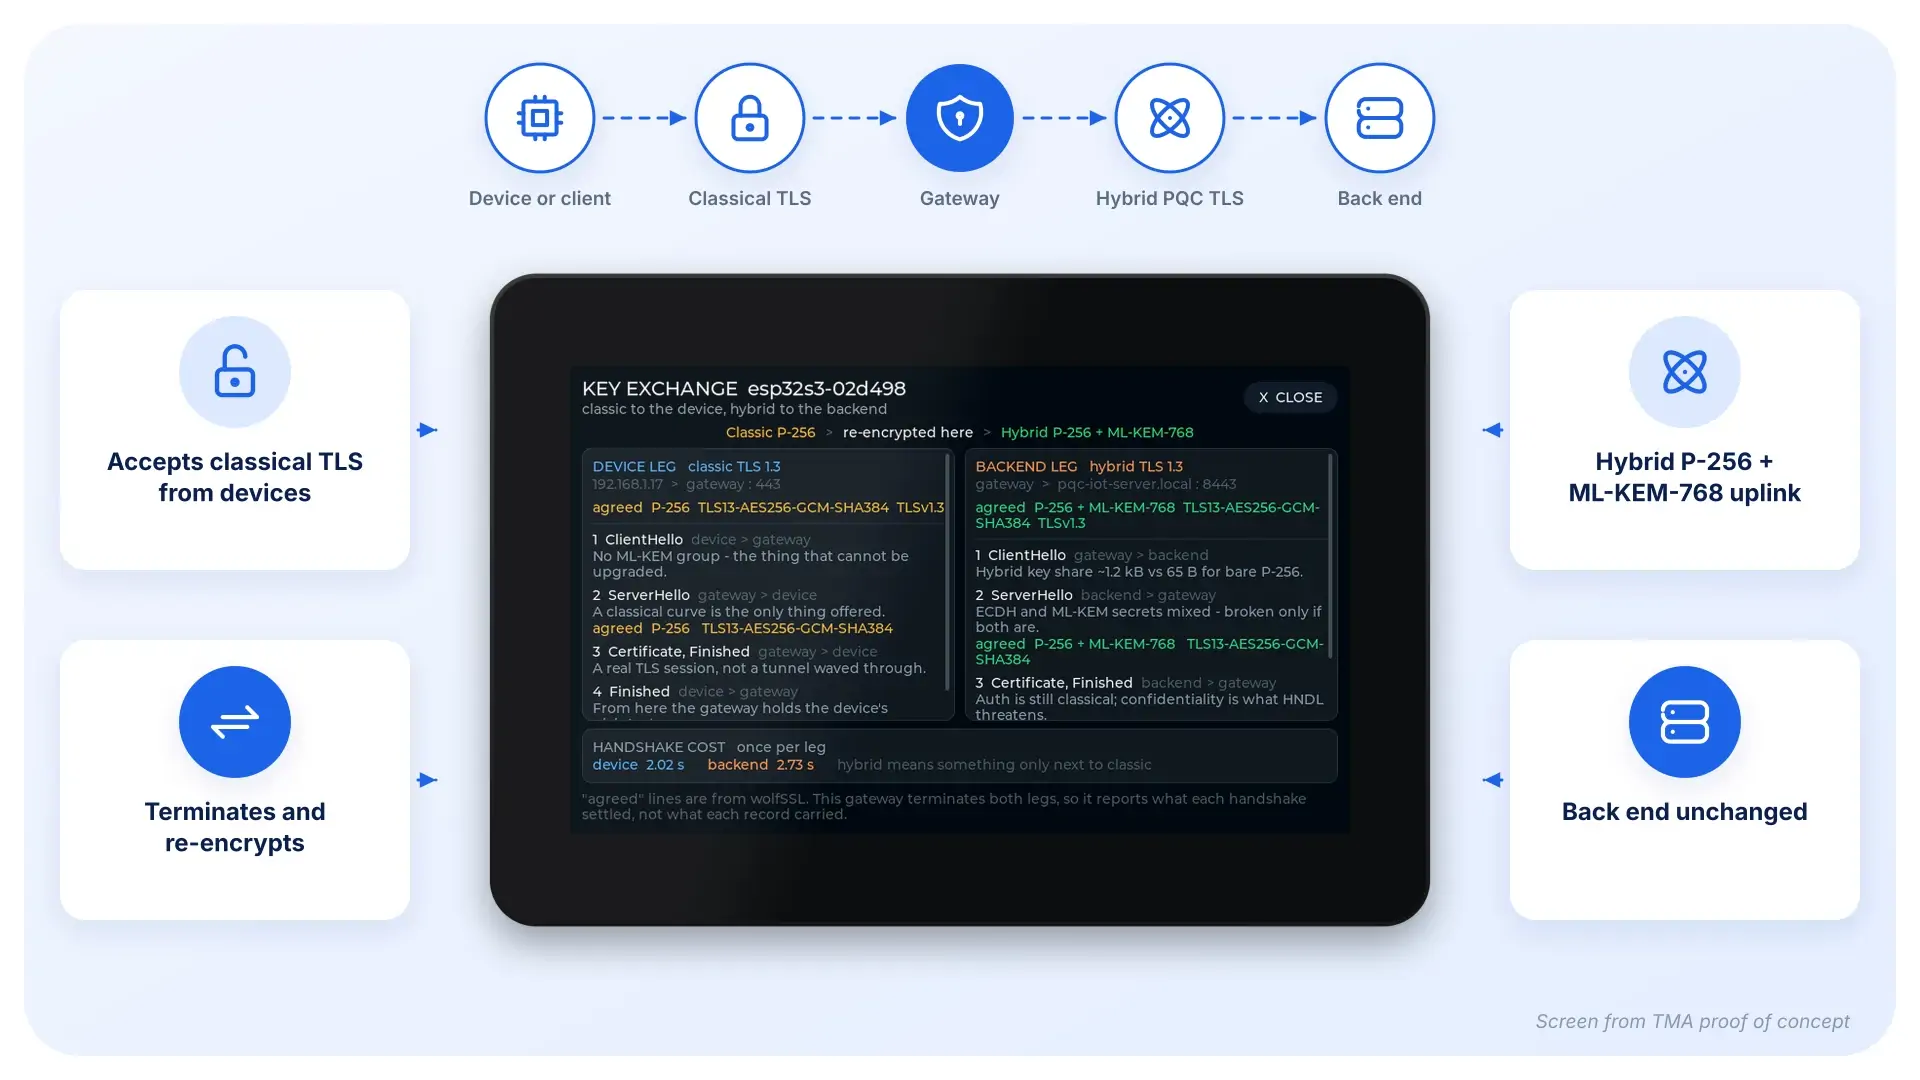
See Who Is Still Classical
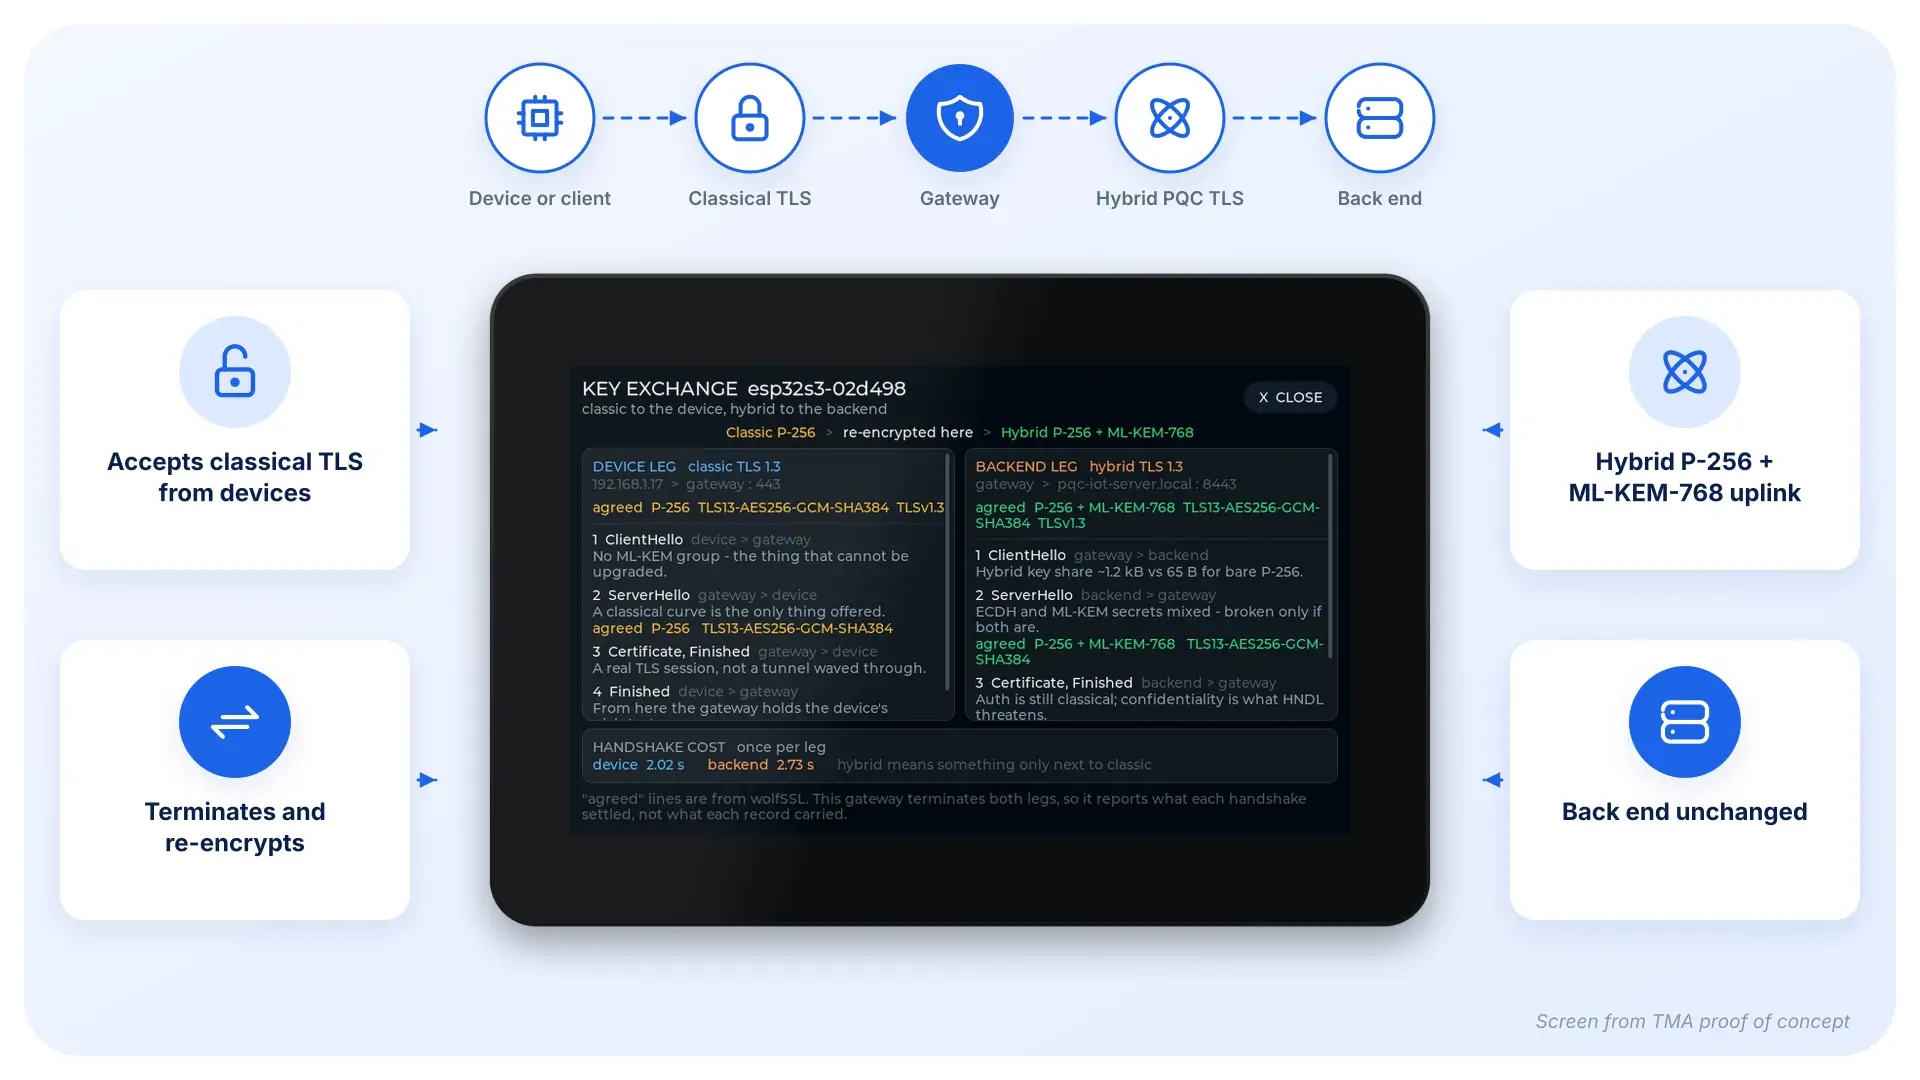
Fit the Site or the API
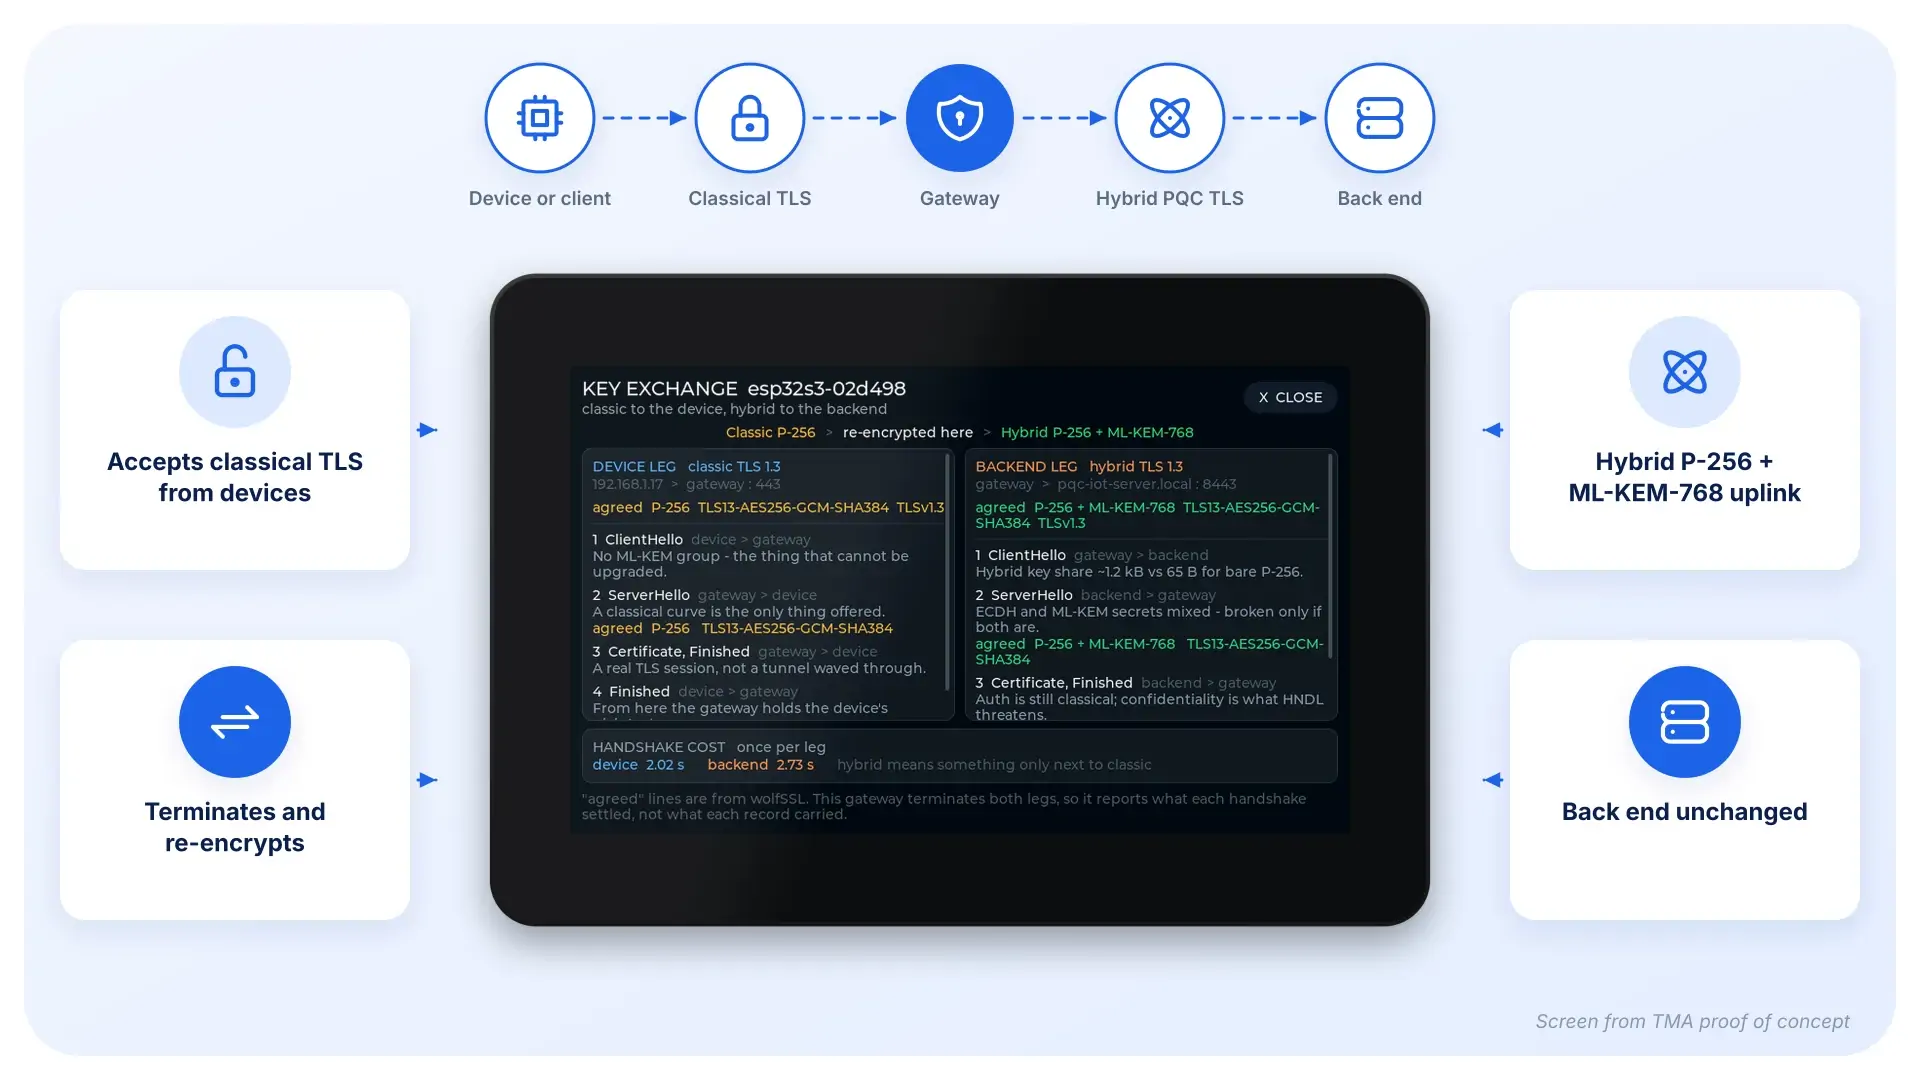
Deployment & Integration
The gateway is designed to sit inside existing infrastructure, not replace it.
On-Site or On-Premise: Installed inline at a site or in the data centre, on standard hardware or a virtual machine.
In Front of Existing APIs: Added at the API entry point, with no change to back-end services.
Works with Existing Keys and Certificates: Integrates with the organisation’s current certificate and key-management setup.
Delivered with Partners: KPS and its partners customise the rollout for each environment, starting with a proof of concept.
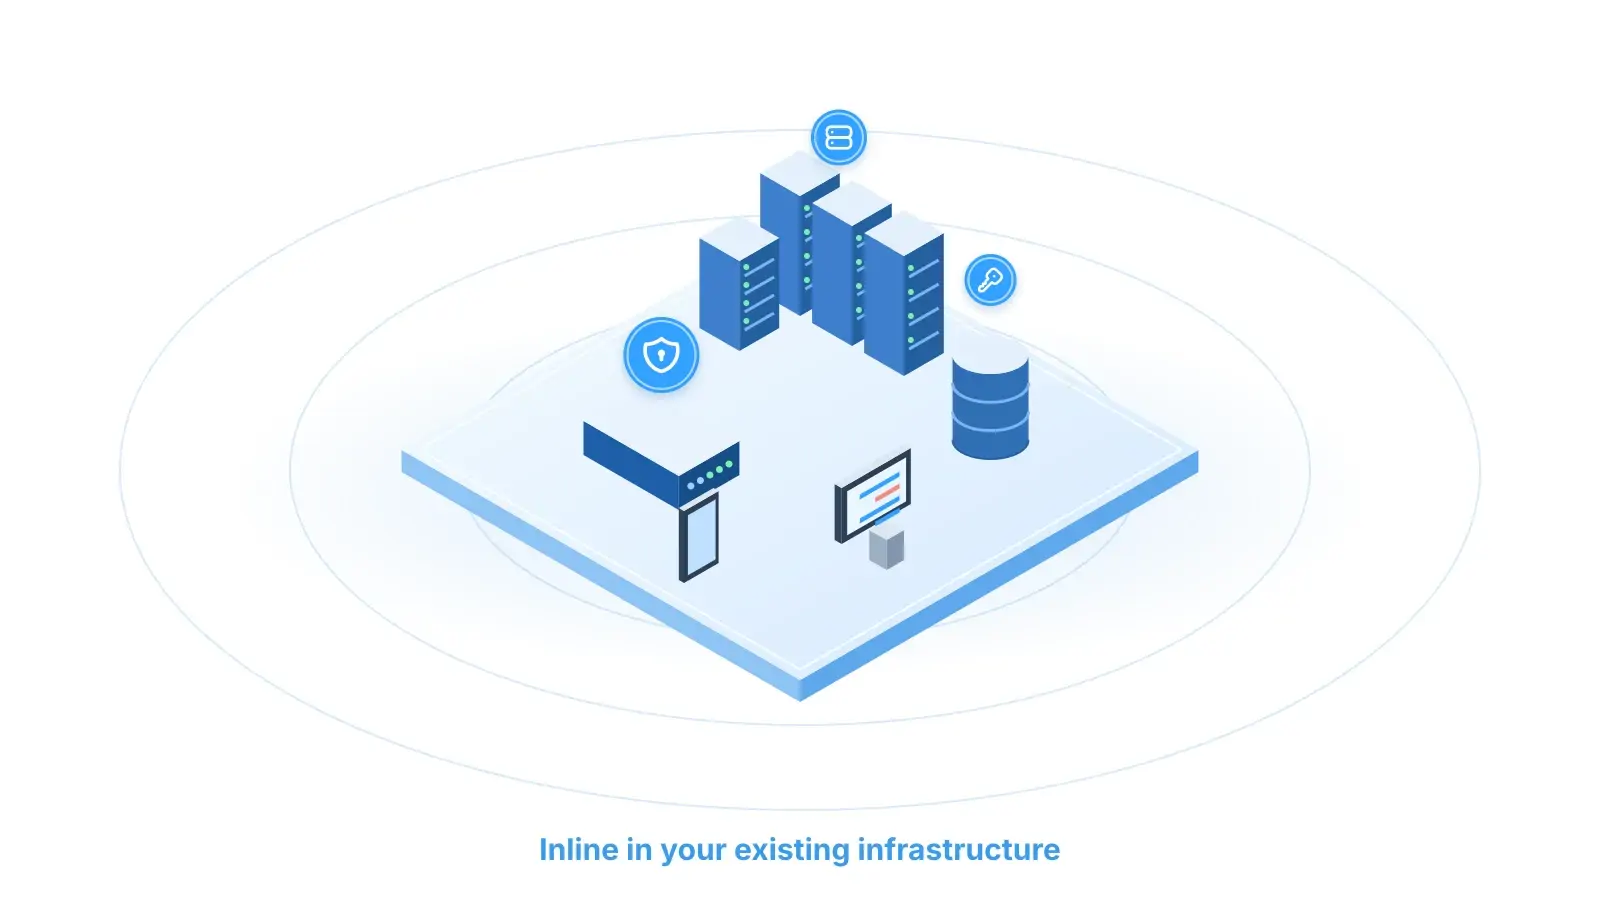
Designed to fit your setup
Reference scenarios
Devices such as PLCs, SCADA controllers and smart meters often run fixed firmware for many years with no remote update path. A gateway at each site terminates their classical TLS and sends the data to the back end or cloud over hybrid post-quantum TLS 1.3. Devices are not touched and can be replaced gradually later.
Key Outcomes
No device changes
One install per site
Quantum-safe uplink from day one

Contact Us
For any questions, support requests or partnership opportunities, please reach out to us via:


